Search results for tag #messaging
NEWSCARD: Decentralized, Encrypted Paste Bin via Usenet Newsgroups
- NEWSCARD * Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS #CyberSecurity #Privacy #ComSec #OpSec #OpenSSL #ChaCha20
[image description]
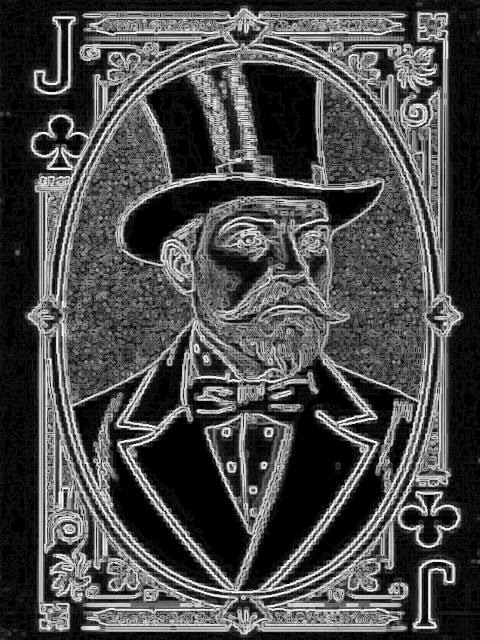
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.
GrapheneOS plans its own messenger solution with RCS and E2EE
GrapheneOS plans its own messenger solution with RCS support and end-to-end encryption. In addition, outdated AOSP default apps are to be replaced.
#Android #Datenschutz #GrapheneOS #IT #Messaging #Motorola #Security #news
Signal Introduces Automatic Key Verification. This will further prevent MITM attacks
https://signal.org/blog/automatic-key-verification/
#tech #technology #news #technews #security #privacy #signal #messaging
Signal expands privacy and control with linked Android phones/tablets and iPhones, plus end-to-end encrypted message syncing. 🔐
Automatic key verification adds key transparency, while phone-number-free signup is being developed with an anti-abuse barrier. 🛡️
#TechNews #Signal #Privacy #Encryption #KeyTransparency #OpenSource #FOSS #Security #Messaging #E2EE #Linux #Technology #DigitalRights
"In recent years, the Signal messaging app has become a newsroom staple, enabling journalists, colleagues, sources, and others to speak to one another securely with end-to-end encryption. This means no one except those in conversation — not even the service provider — can read your messages or listen in on your calls. Journalists use it individually, and we also see a trend toward using organizational Signal tiplines.
But it’s important to understand this is not a ”set it and forget it” decision. When talking to sensitive contacts, you do need to maintain your account to ensure it is safe and does not fall into the wrong hands.
Imagine if someone took over your Signal account. They could impersonate you, causing reputational damage, or worse, putting sources at risk. Unfortunately, this is not a hypothetical. We have seen at least one public example (and some less public) where newsrooms have lost access to Signal identifiers, sometimes leading to abuse.
There are a few simple things journalists can do to maximize the safety of their Signal account."
https://freedom.press/digisec/blog/signal-account-safety/
#Messaging #Signal #Privacy #Surveillance #Encryption #PrressFreedom #Journalism #Media
WhatsApp is rolling out usernames, letting users hide their phone numbers from people outside their contacts for added privacy. 🔒📱
Users can reserve names now, with optional username keys adding another layer of control before messaging begins. ✅
#TechNews #WhatsApp #Privacy #Usernames #Meta #Messaging #CyberSecurity #DataPrivacy #Encryption #Technology #Mobile #Tech #DigitalRights #Software #Username
«Your End-to-End Encrypted Messages:
Aren't As Secure As You Think
Here's what end-to-end encryption protects—and what it doesn't.»
I know, this is not a new topic for most of you here, but you can forward it outside of the Fediverse ;)
💬 https://lifehacker.com/tech/end-to-end-encrypted-messages-security-issues
#signal #whatsapp #telegram #identity #messaging #chat #itsec #e2ee #encryption #privacy #protection #security #issues #secruityissues #online
WhatsApp is adding usernames — message people without either side seeing a phone number. Your number unlocks a lot of personal info; a username keeps it private from other users (not from Meta). Reserve yours: Settings → Account → Username.
 boosted
UK device-scanning proposal for nude image detection draws Signal criticism over mandatory on-device inspection and expanded age verification across phones and apps. 📱
Signal warns the plan risks normalizing client-side surveillance and weakening private communication protections under encrypted messaging systems. 🔐
🔗 https://www.techspot.com/news/112712-signal-attacks-uk-plan-scan-devices-nude-images.html
#TechNews #Privacy #Encryption #Signal #UK #OnlineSafety #Surveillance #Cybersecurity #DigitalRights #FOSS #Messaging #DataPrivacy #Security
 🐦🔥nemo™🐦⬛ 🇺🇦🍉

Four easy steps to elevate your privacy & security this year:
Choose a privacy-respecting browser 🌐 Check out: https://privacytests.org/
Use a privacy-first search engine 🔎 (Startpage, DuckDuckGo, self-hosted options etc.) further reading: https://www.privacyguides.org/en/search-engines/?h=search+engine
Use privacy-respecting email 📧 (Proton, Tuta, ) further reading: https://www.privacyguides.org/en/email/
Use only E2EE messaging apps 🔒 (cross-platform with minimal metadata: Signal) further reading: https://www.privacyguides.org/en/real-time-communication/
You're welcome… spread the word! Sharing is caring 🎁💬
The gift that keeps on giving: data retention, compartmentalization, FOSS, privacy & security. #FCKBigTech stick it to them… #FCKSurveillanceCapitalism 🖕Privacy security isn't a sprint; it is a marathon… Even a journey of over 9k steps begins with the first one… 🙏 💚Use E2EE, full-disk encryption, back up, and update…
#Privacy #Security #E2EE #FOSS #OpenSource #DataProtection #Browser #SearchEngine #Email #Messaging


WhatsApp Clone, but Decentralized with P2P Messaging
"Secure and private" is the general goal.
This is a technical/concept demo of a fairly unique approach using a browser-based, local-first and webrtc.
This is intended to introduce a new paradigm in client-side managed secure cryptography. We can avoid registration of any sort.
Features:
* P2P
* End to end encryption
* Signal protocol
* Post-Quantum cryptography
* File transfer
* Local-first
* No registration
* No installation
* No database
* TURN server
Feel free to reach out for clarity instead of diving into the docs/code.
IMPORTANT: While this is aiming to provide a secure experience, it isnt audited or reviewed. **Shared for testing, feedback and demo purposes only.** Please use responsibly.
#Privacy #OpenSource #P2P #WebRTC #Decentralization #DigitalSovereignty #CyberSecurity #FOSS #SelfHosted #NoCloud #AntiCorp #Encryption #WebDev #TechLiberty #PrivateMessaging #Networking #DataPrivacy #InternetFreedom #LocalFirst #SoftwareEngineering #WebApps #ZeroKnowledge #PrivacyTech #IndieDev #NoSignup #NoInstall #DecentralizedWeb #SecureMessaging #BrowserApp #TechEthics #P2P #WebRTC #PeerJS #ZeroData #EphemeralData #Encryption #E2EE #BrowserToBrowser #NoInstall #Privacy #Security #Decentralized #Messaging #VideoCall #NoTracking #PrivateMessaging #Prototype #Demo #WorkInProgress #CloseSource #OpenSource #WebDev #GitHub #TechDevelopment #WhatsApp #ChatApp #InstantMessaging #PWA
This is intended to introduce a unique approach in client-side managed secure cryptography. We can avoid registration of any sort.
Features:
PWA
P2P
End to end encryption
Signal protocol
Post-Quantum cryptography
Multimedia
File transfer
Video calls
Local-first
No registration
No installation
No database
TURN server
https://www.reddit.com/r/positive_intentions
#Privacy #OpenSource #P2P #WebRTC #Decentralization #DigitalSovereignty #CyberSecurity #FOSS #SelfHosted #NoCloud #AntiCorp #Encryption #WebDev #TechLiberty #PrivateMessaging #Networking #DataPrivacy #InternetFreedom #LocalFirst #SoftwareEngineering #WebApps #ZeroKnowledge #PrivacyTech #IndieDev #NoSignup #NoInstall #DecentralizedWeb #SecureMessaging #BrowserApp #TechEthics #P2P #WebRTC #PeerJS #ZeroData #EphemeralData #Encryption #E2EE #BrowserToBrowser #NoInstall #Privacy #Security #Decentralized #Messaging #VideoCall #NoTracking #PrivateMessaging #Prototype #Demo #WorkInProgress #CloseSource #OpenSource #WebDev #GitHub #TechDevelopment #WhatsApp #ChatApp #InstantMessaging #PWA
Alt...
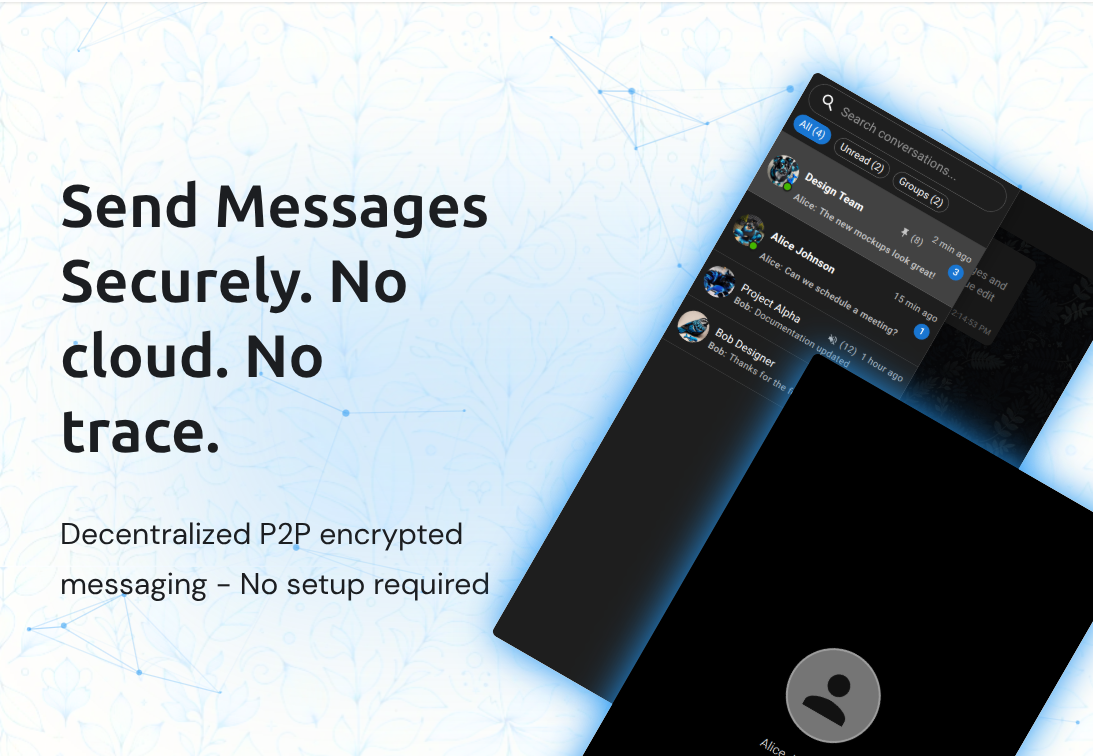
Send Messages Securely. No cloud. No trace.
Decentralized P2P encrypted messaging - No setup required
Delta Chat is a messaging platform that works over email.
Setup is similar to a email client.
Messaging is decentralized and interoperable.
Supports end-to-end encryption via PGP.
PGP encryption keys are created automatically.
Default desktop client is based on Electron.
Electron is based on the Google Chromium web browser.
Website: https://delta.chat
Mastodon: @delta
#DeltaChat #Messaging #Privacy #InfoSec #E2EE #OpenPGP #PGP #OpenSource #FOSS #CyberSecurity #Encryption #FreeSoftware
Alt...
Delta Chat logo.

"Despite advancements in secure messaging, PGP (Pretty Good Privacy) encryption—developed in the 1990s—remains a gold standard for privacy. Unlike modern apps reliant on centralized servers or phone numbers, PGP ensures end-to-end encryption without third-party dependencies. This article explores PGP’s enduring relevance, key management best practices, and how it compares to contemporary solutions like Signal."More: https://undercodetesting.com/why-pgp-encryption-still-outperforms-modern-messaging-apps/
NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @crypto@a.gup.pe @infosec@a.gup.pe @selfhosting@a.gup.pe

Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.
NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @crypto@a.gup.pe @infosec@a.gup.pe

Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.
NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @usenet@lemmy.world @crypto@a.gup.pe @infosec@a.gup.pe
Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.