Search results for tag #infosec
 [
American Express ordered to fix security gaps after a customer complained about improper employee access.
It seems that a customer reported a privacy concern and fought AmEx for 4 years to get them to implement stronger access controls or monitoring of employee access to data.
Now, the AU govt has ordered AmEx to rectify security flaws in five of its data systems to guard against “insider threats” and to restrict employee access to specific customer information to protect vulnerable and high-profile customers.
and:
https://www.oaic.gov.au/__data/assets/pdf_file/0031/264919/Report-of-investigation-into-AMEX.pdf
h/t, @TheAge (paywalled):
https://www.theage.com.au/business/banking-and-finance/american-express-ordered-to-fix-security-gaps-after-customer-was-spied-on-20260612-p606ei.html
#AmEx #AmericanExpress #insiderthreat #accesscontrols #logging #enforcement #privacy #FinSec #infosec
A source wants to reach you safely. With most messengers that starts with a problem: they need your phone number, you get theirs, and a server in the middle logs that you two talked.
Zerion skips all of that. You share a QR code or link, the connection runs device to device over Tor, and no record of the contact exists outside your two phones.
Source code and protocol docs are public. Verify before you trust: https://github.com/zerionproject/Zerion

People who have been around the tech world longer than I have: I've been reading for a while how some people seem to feel like the industry peaked somewhere in the 2000s and that it all went downhill from there.
There was one hype after the next and people just kept on jumping on the bandwagon because everyone was doing it. I've read this sentiment about containers, Kubernetes, the Cloud in general but there are probably more.
Do you feel that LLMs are more of the same of this or does this feel qualitatively different? If so, how? I'm trying to find some perspective in all this as I haven't been around the block for long enough to have it myself.
Boosts appreciated.
PSA regarding a change in how Secure Boot will work in Fedora soon. The change isn't urgent, but it is something you should take a look at.
If you have any questions about this, please ask in our forum. 🙏
➡️ https://fedoramagazine.org/expiration-of-microsoft-secure-boot-keys/
Forum: https://discussion.fedoraproject.org/c/ask/6
#Fedora #Linux #OpenSource #Cybersecurity #InfoSec #SecureBoot
#tech #technology #BigTech #data #security #privacy #safety #InfoSec #IT #surveillance #computing #digital #online #internet #web #cloud #meme
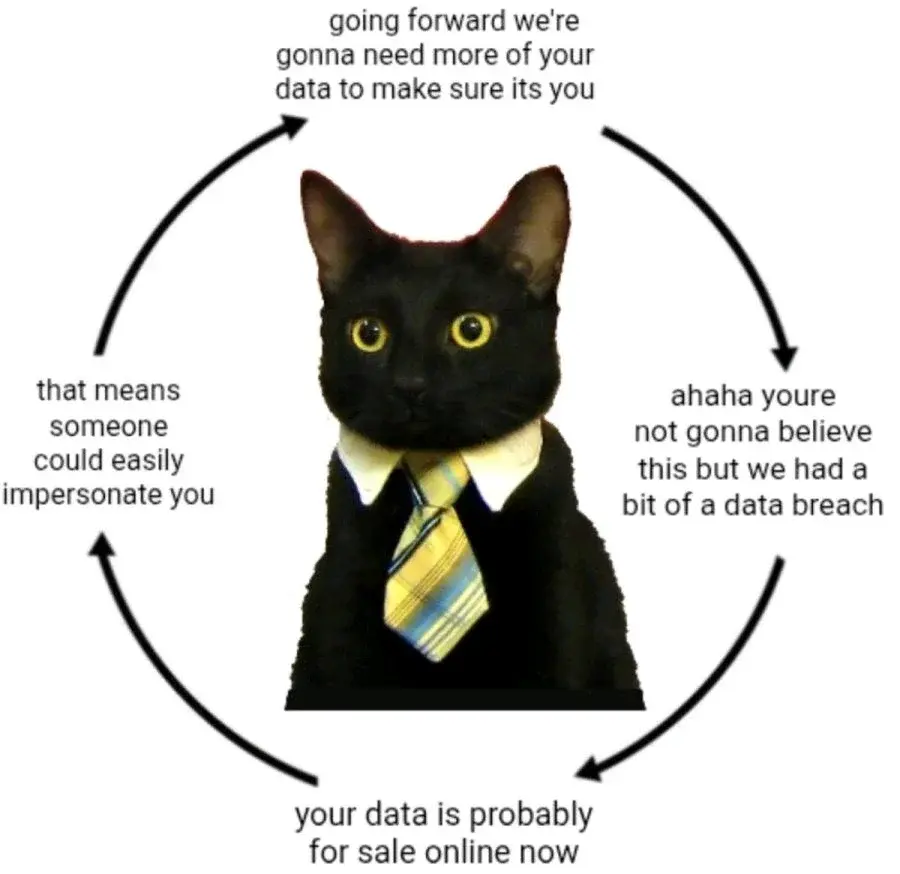
Alt...
Meme, showing a continuous circle of data breach messages from corporations…
Ahaha you're not gonna believe this but we had a bit of a data breach.
Your data is probably for sale online now.
That means someone could easily impersonate you.
Going forward we're gonna need more of your data to make sure its you.
#Github Security Advisories program is struggling under the load of new submissions. Delays in CVE assignment up to a month are being reported. Apparently, May 2026 was the highest volume month ever, and they are working through a backlog.
source: https://www.openwall.com/lists/oss-security/2026/06/10/9
It is not very hard to figure out what is going on: The amount of AI-assisted reports is flooding the systems. Considering the asymmetric nature of the situation (limited human resources processing increasing number of reports), it is unlikely the it is getting any better soon.
If just tracking and assigning issues is getting this hard, it can't bode well for actually fixing and patching them.


 Built something I’ve wanted for a while...
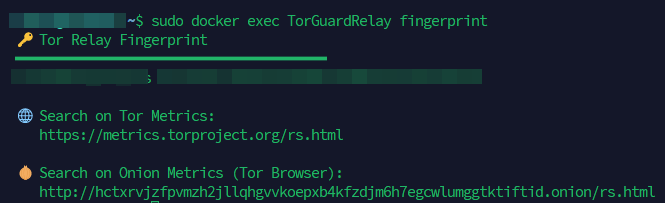
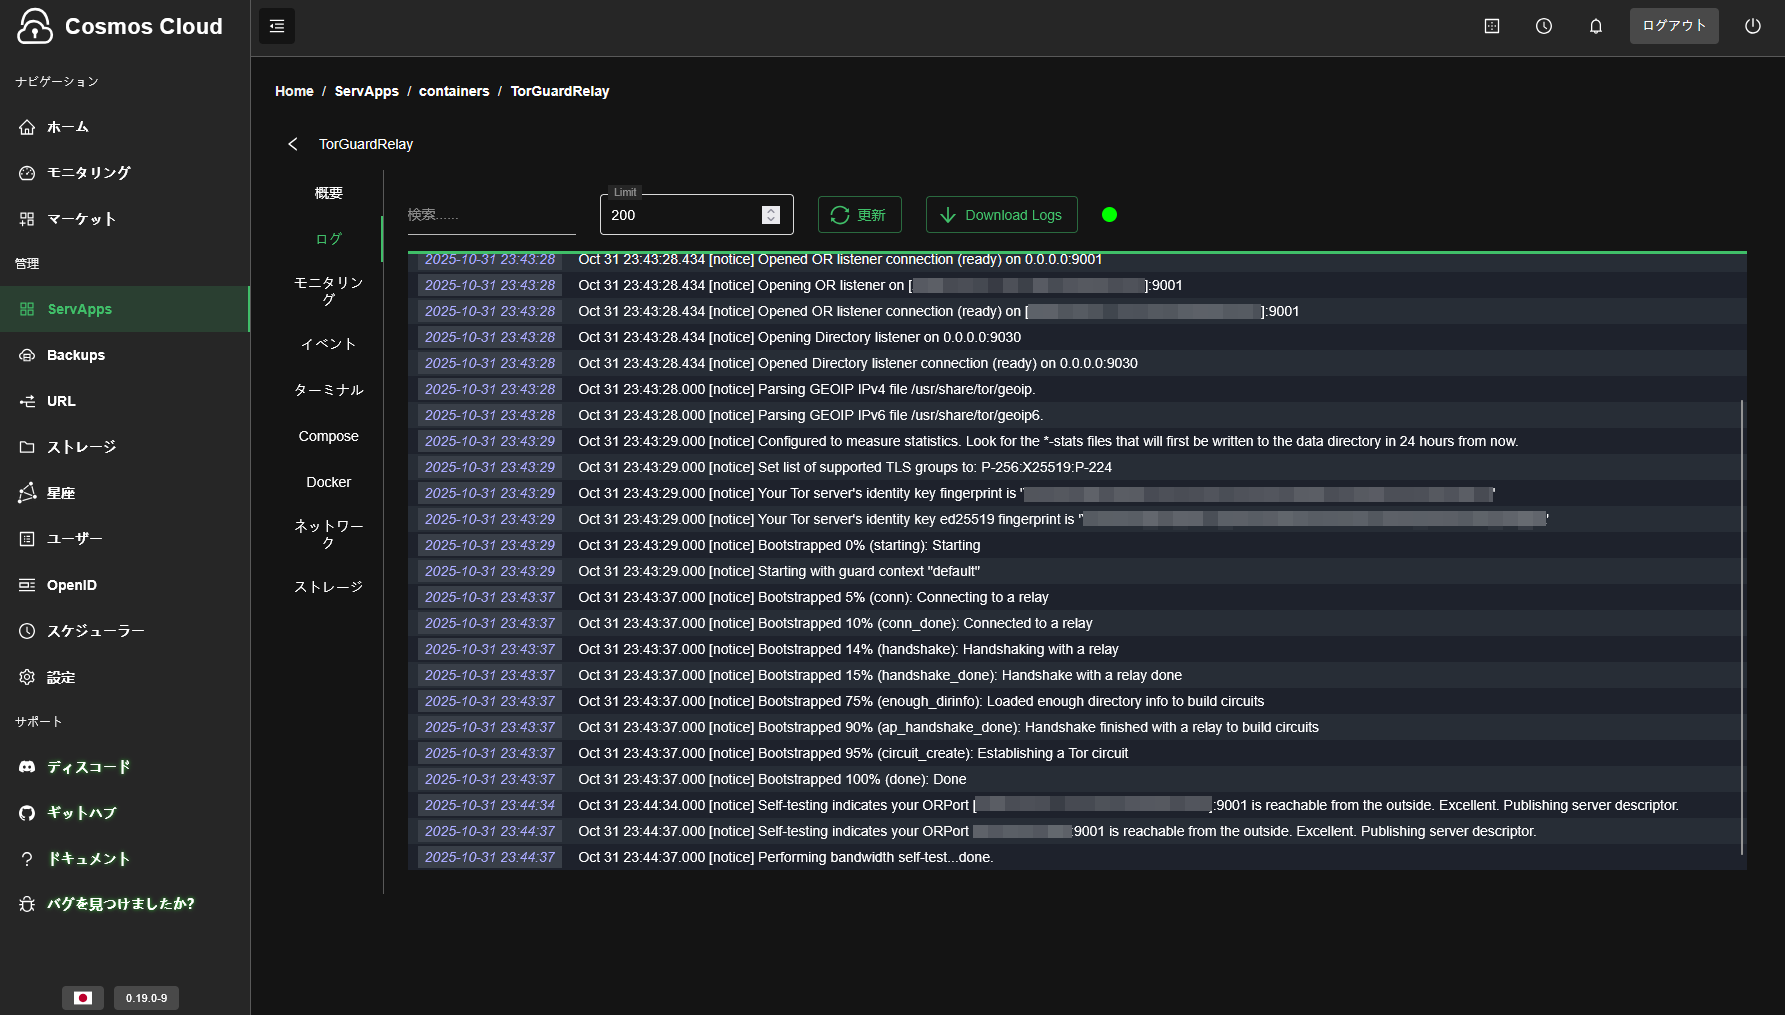
An open-source Docker container that makes running a Tor relay actually simple and reliable.
One command. Self-healing. Multi-arch. Runs everywhere from Raspberry Pi  to VPS

🔗 https://github.com/r3bo0tbx1/tor-guard-relay
If you care about privacy infrastructure:
🧱 Try it out
🐛 Report bugs
💡 Suggest features
⭐ Star it to help others discover it
 Maintaining this in my free time, donation info’s in the README (and please support @torproject, @eff and @privacyguides too).
Protecting privacy, one relay at a time ✨
#Tor #Privacy #OpenSource #Docker #FOSS #SelfHosting #Infosec

The Net-NTLMv1 Rainbow Table is now complete and ready to share!
#InfoCon hosts several tables, as well as word lists, old school style.
Check out https://infocon.org/ for the torrent files.
#InfoSec #Hacking
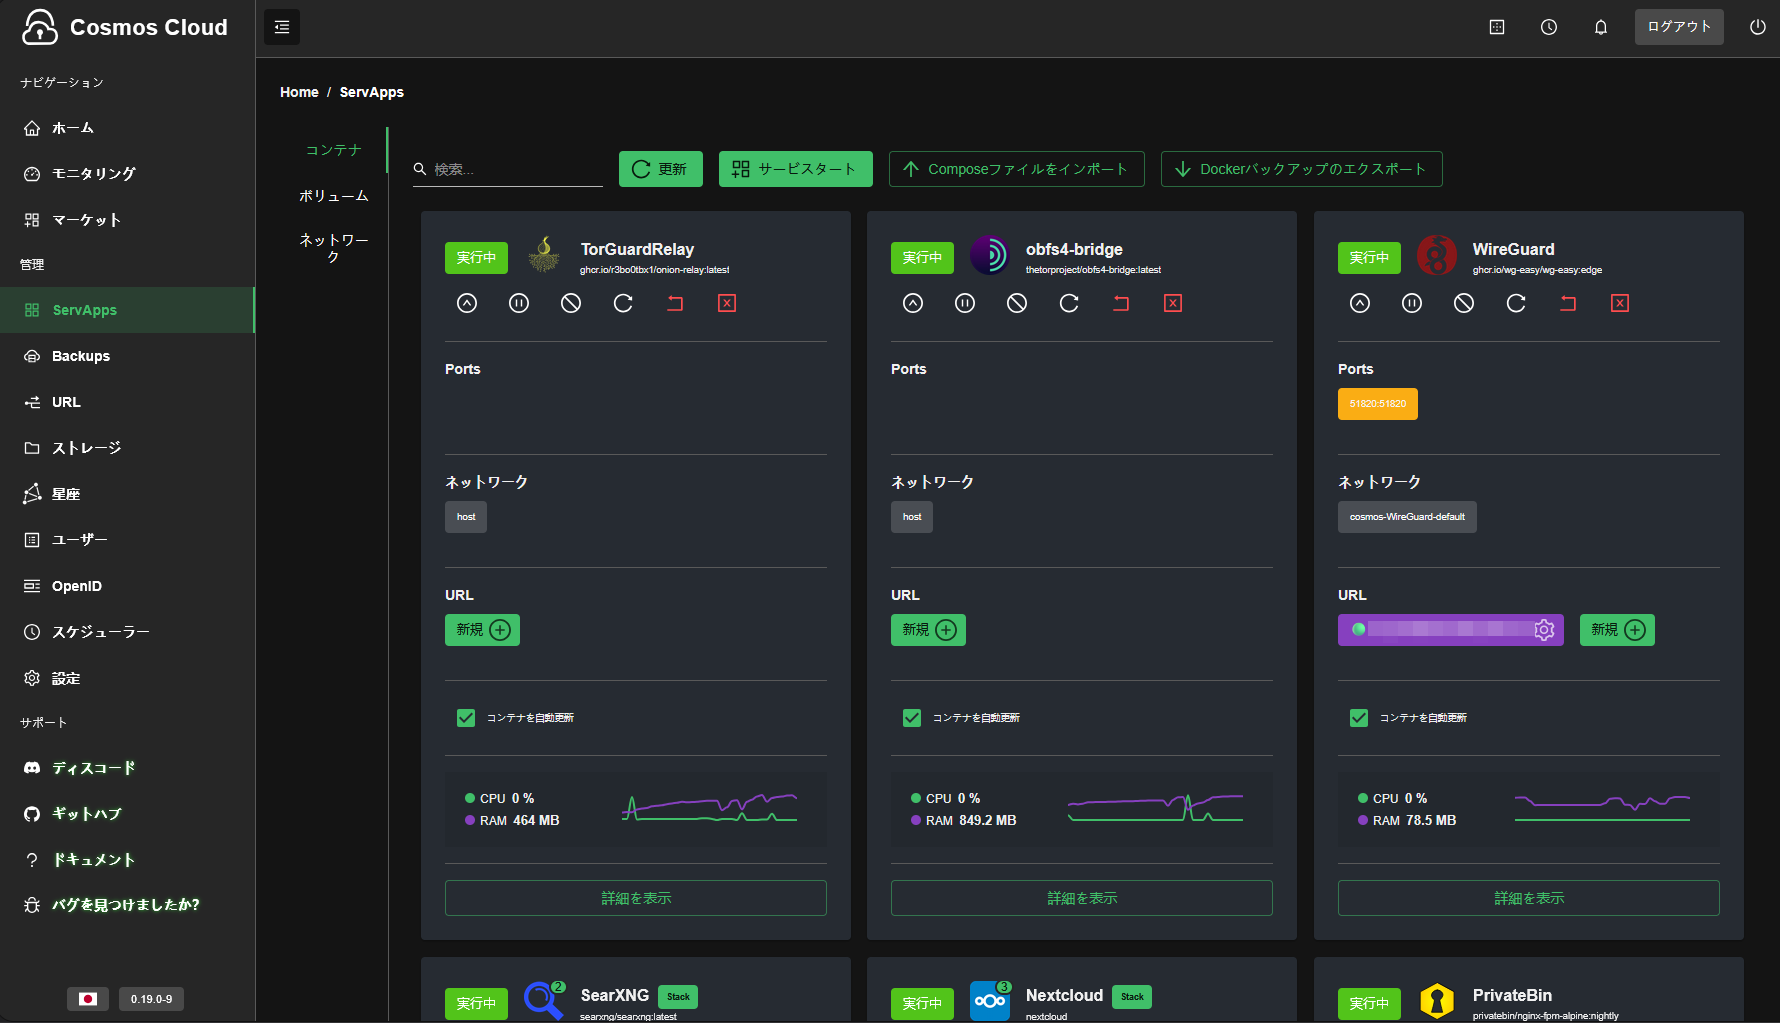
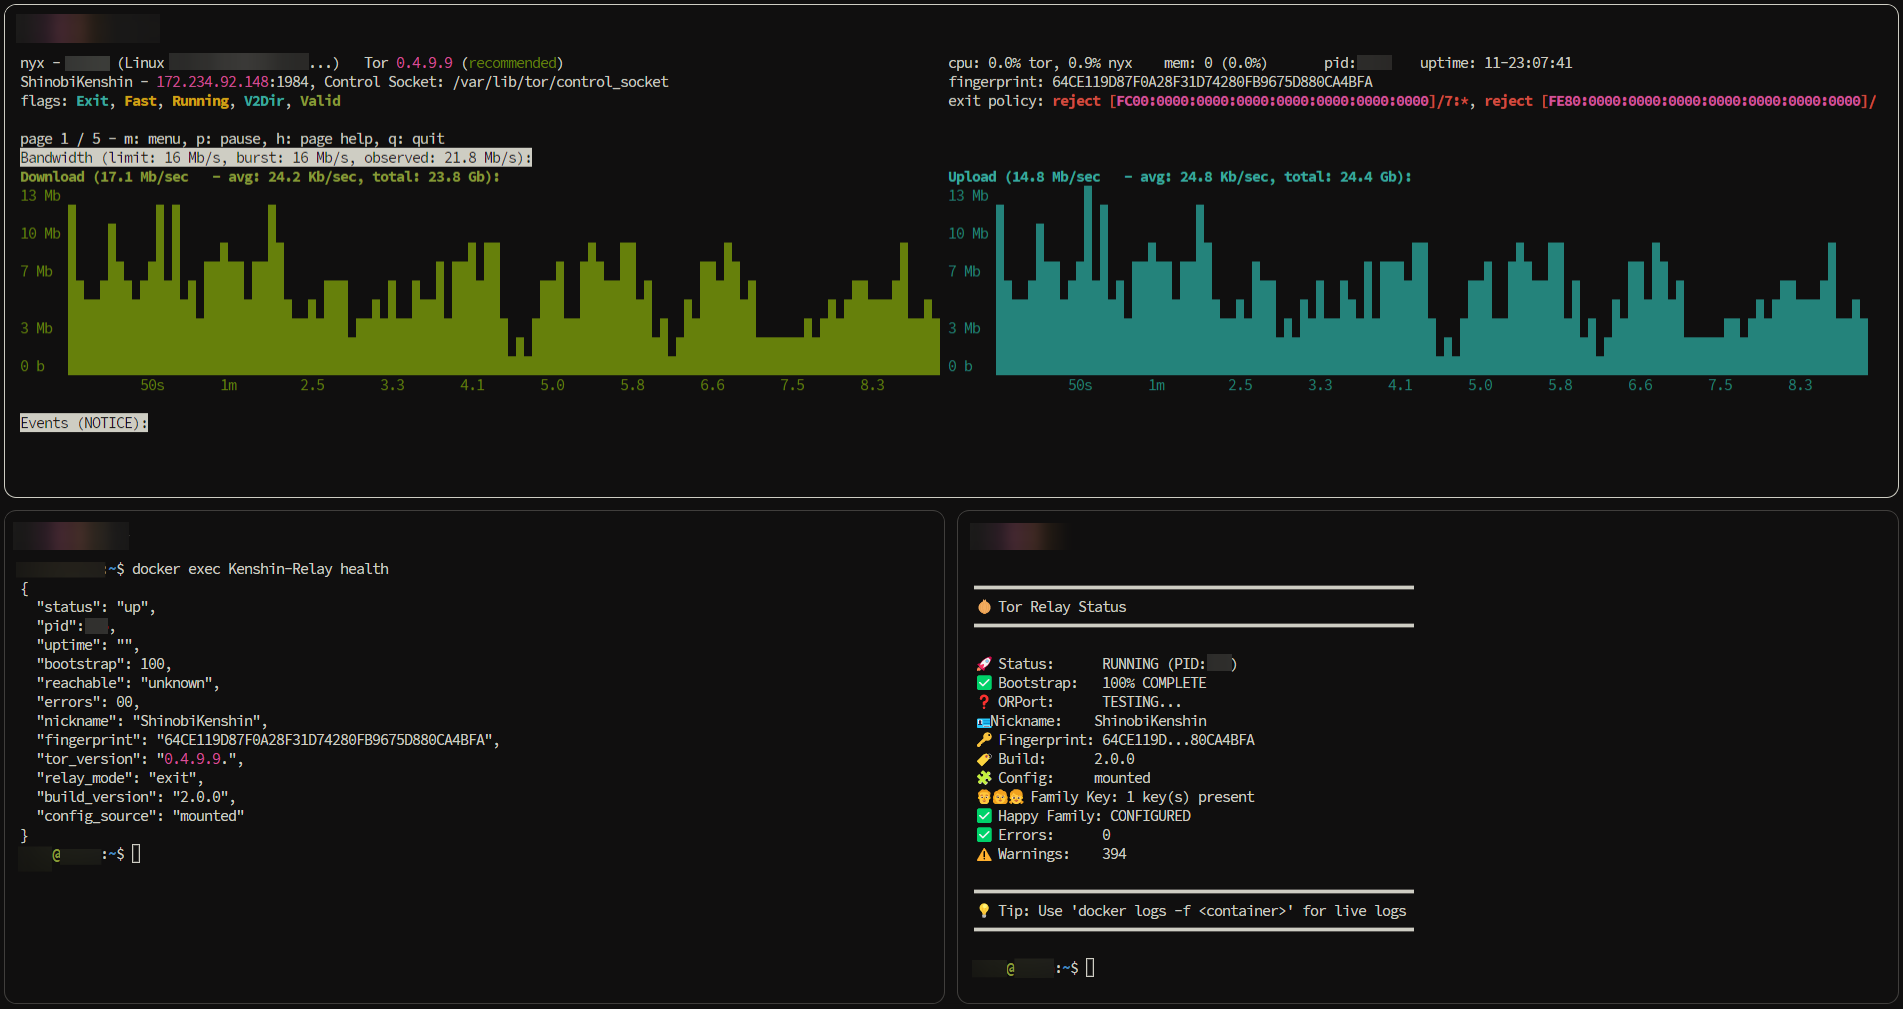
onion-relay v2.0.0 is out, and it's been a long road from v0.0.1 ⬇️
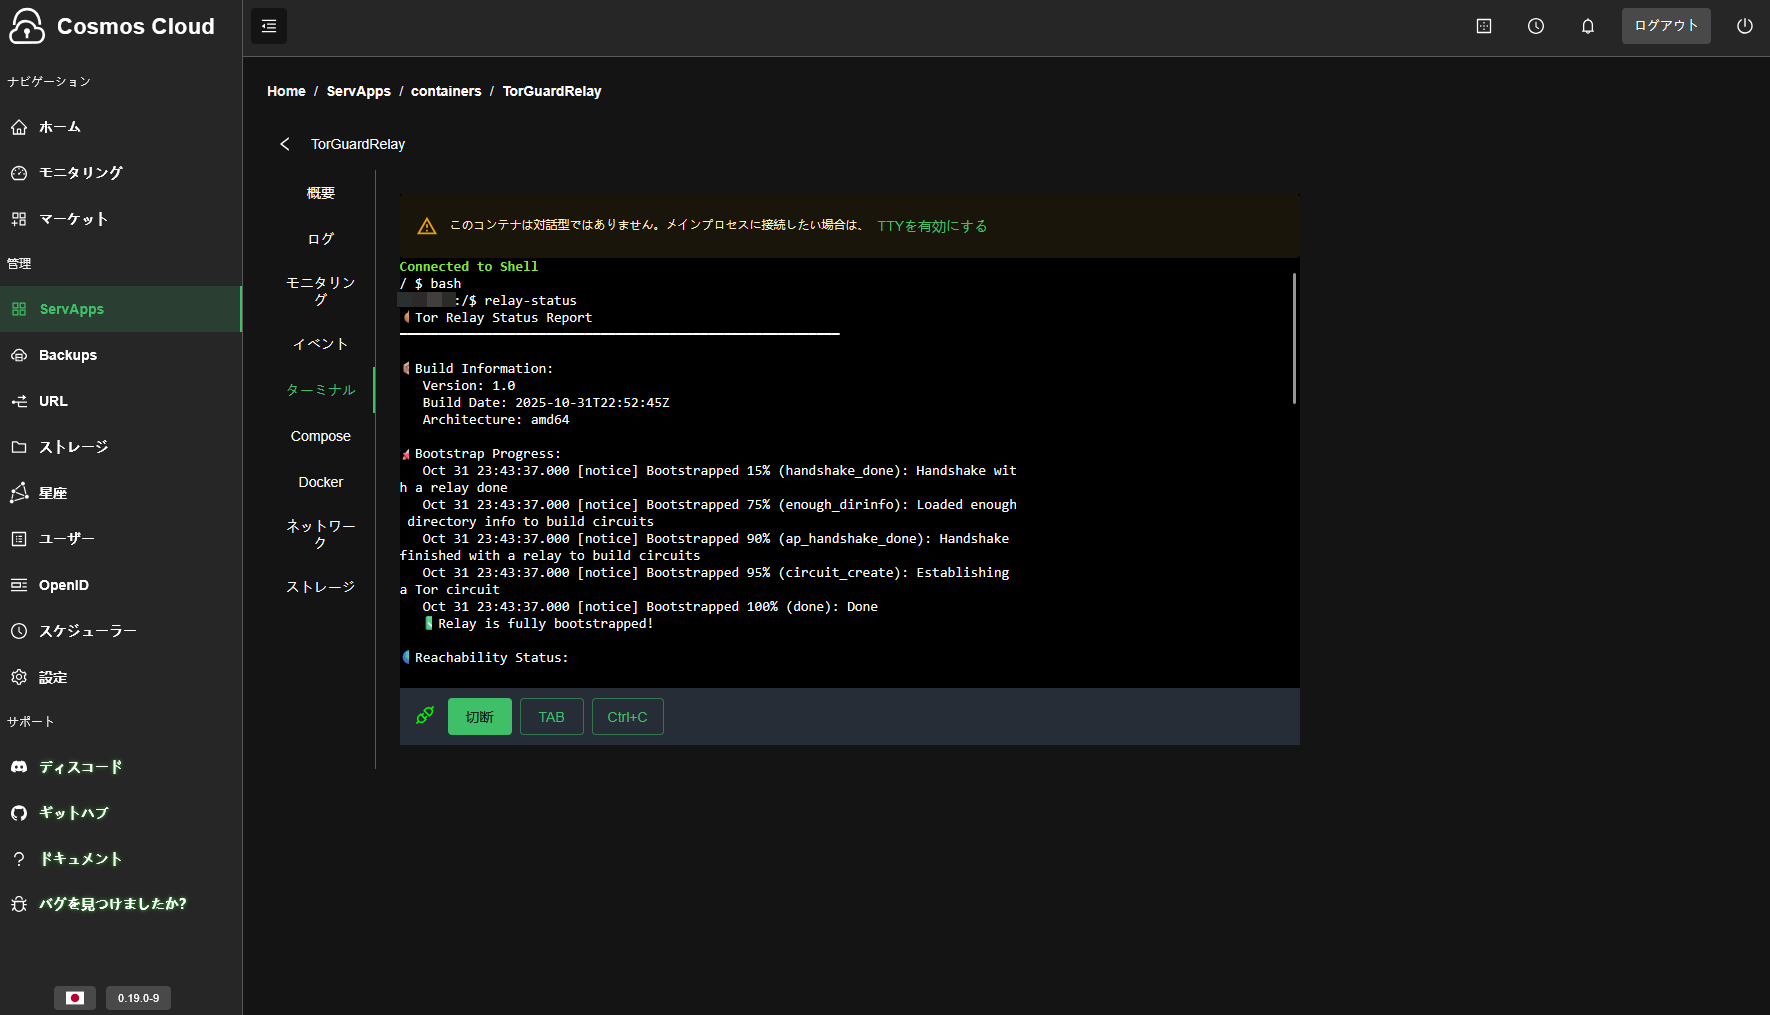
ℹ️ What started as "one command to run a relay" is now a hardened, production-tested AIO stack: guard, exit, and bridge (obfs4) in a 16.8 MB image.
What's new in v2.0.0:
🩺 health + status tools now expose build_version & config_source
⚡ healthcheck.sh fails fast on missing/empty torrc
🔒 DirPort now defaults to 0 (disabled) in ENV-generated configs
What the project has grown into since launch:
🔑 Happy Family support (Tor 0.4.9+ FamilyId, 🪦 RIP MyFamily lists)
🧰 6 busybox only diagnostic tools
🌍 Battle-tested across 10+ countries: https://relays.brokenbotnet.com
🔐 35+ security fixes, CVE coverage, weekly automated rebuilds
🐋 Works with Docker CLI, Compose, Cosmos Cloud & Portainer
 https://github.com/r3bo0tbx1/tor-guard-relay
If you care about privacy infrastructure:
🥢 Try it out
🐛 Report bugs
💡 Suggest features
⭐ Star it to help others find it
Still maintaining this in my free time, donation info
in the README. And please support @torproject
@eff and @privacyguides too.
Protecting privacy, one relay at a time ✨
#Tor #Privacy #OpenSource #Docker #FOSS #SelfHosting #Infosec
📜 Scrolls volume 32 is out! Go check it out for the latest #indieweb, #fediverse and #infosec / #cybersecurity stuff.
https://shellsharks.com/scrolls/scroll/2026-03-06
Have a great weekend!

 [
https://feddit.uk/post/45043385
#signal #moxiemarlinspike #telegram #paveldurov #infosec #encryption
Delta Chat is a messaging platform that works over email.
Setup is similar to a email client.
Messaging is decentralized and interoperable.
Supports end-to-end encryption via PGP.
PGP encryption keys are created automatically.
Default desktop client is based on Electron.
Electron is based on the Google Chromium web browser.
Website: https://delta.chat
Mastodon: @delta
#DeltaChat #Messaging #Privacy #InfoSec #E2EE #OpenPGP #PGP #OpenSource #FOSS #CyberSecurity #Encryption #FreeSoftware
Alt...
Delta Chat logo.
Cryptomator is a client-side encryption tool for cloud storage services.
Data protected via AES-256 encryption.
Individual and business features.
Managed and self-hosted options.
ENCRYPTED
File content.
File/Folder name.
NOT ENCRYPTED
File/Folder access/creation/modification timestamp.
Number of files/folders in a folder/vault.
File size.
Website: https://cryptomator.org
Mastodon: @cryptomator
#Cryptomator #Encryption #InfoSec #Privacy #CyberSecurity #FreeSoftware #FOSS #FLOSS #OpenSource
Alt...
Cryptomator logo.

NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @crypto@a.gup.pe @infosec@a.gup.pe @selfhosting@a.gup.pe

Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.

I wish people would stop giving credit to "prominent cybersecurity/cryptography experts" just because they released some "cypherpunk" book or software of unproven impact 30 years ago and have since then retreated into golden tenure, writing technically empty but catchy preprints with provocative titles. These "Ludd grandpas" (you know at least a couple of names of who I'm referring to) are, unfortunately, still worshipped by a large number of semireligious followers, who contribute to the spread of their moldy ignorance.
Thinking deeper, maybe mine is a typical case of rejection for the image in the mirror: I hope I will never become like that in the future.
The world does not stop at your rants. Keep moving and stay open-minded, or become obsolete.
#cybersecurity #security #infosec #cryptography #crypto #academia #rant #luddism
NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @crypto@a.gup.pe @infosec@a.gup.pe

Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.