Search results for tag #opensource
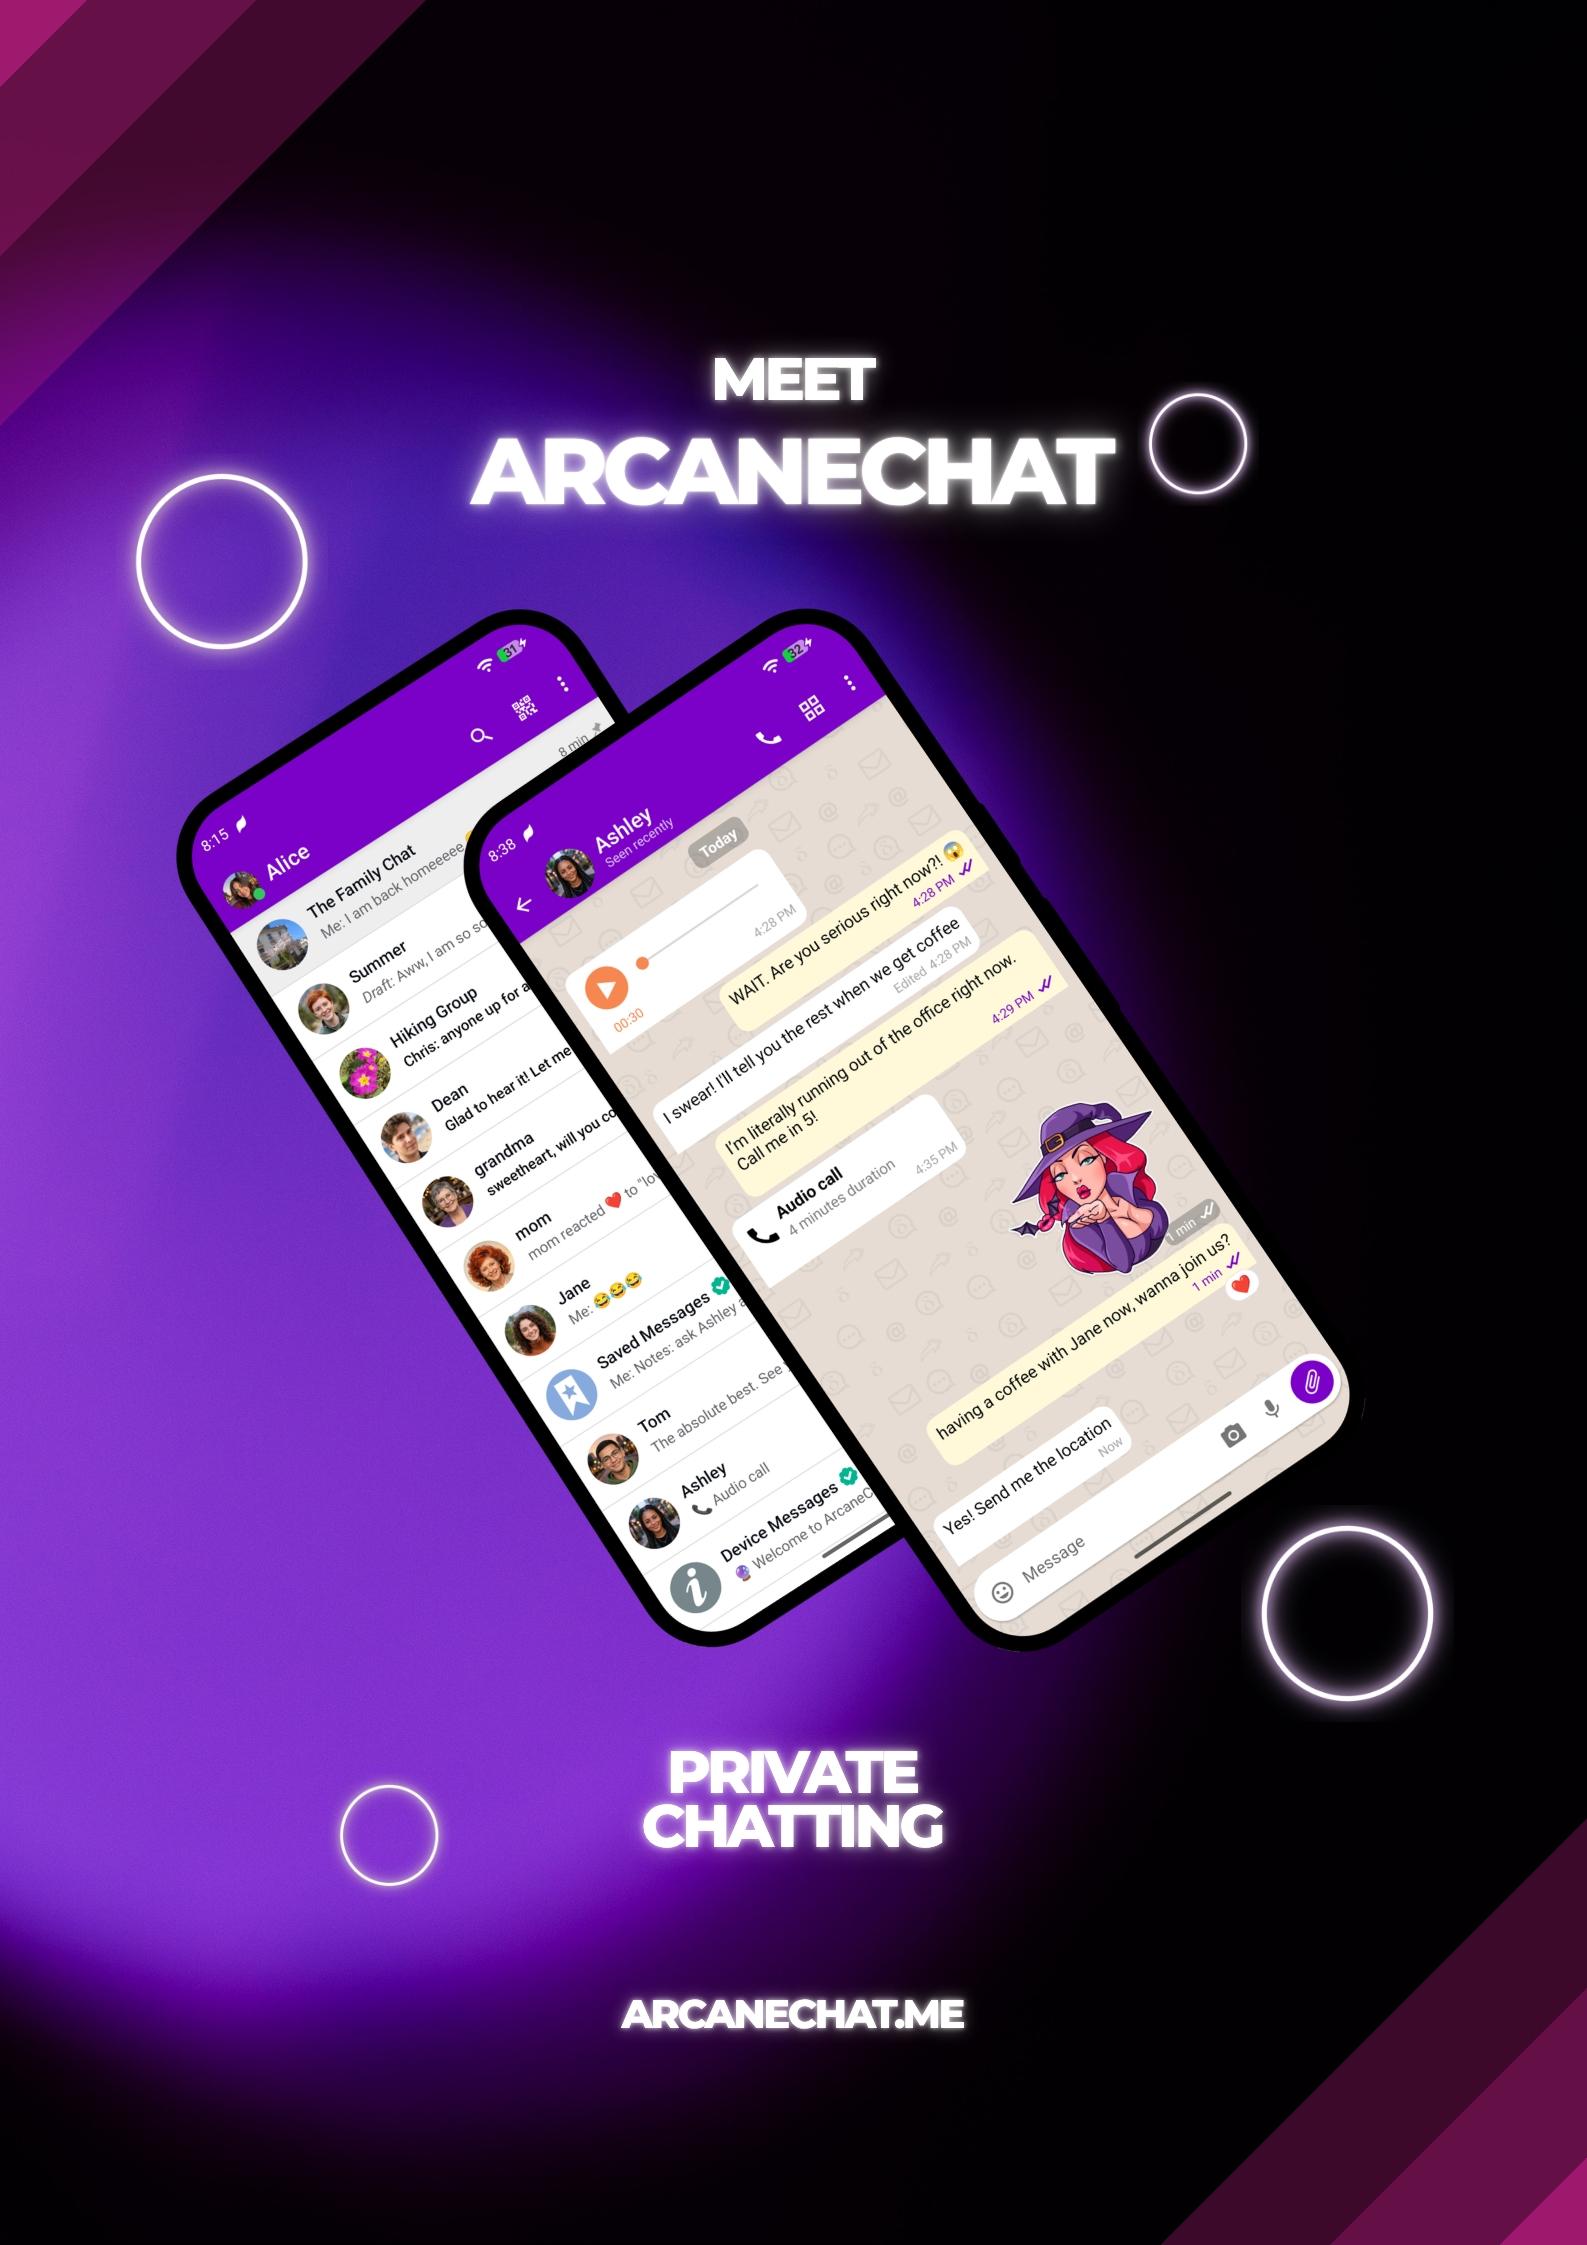
Meet #ArcaneChat
No phone numbers required for registration.
No spam, scammers can't contact you.
All your conversations end-to-end encrypted.
In-chat mini-app, video calls and more!
it is magic! ✨️
#Europe #Android #autonomy #eu #diday #European #OpenSource
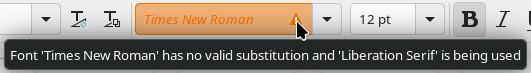
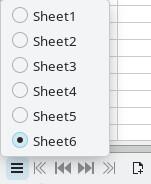
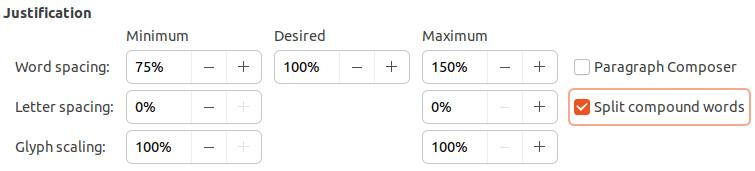
Lots of improvements coming to #LibreOffice: clearer font substitution, a button in Calc to list sheets, better hyphenation support, and more. See our QA and dev summary for September: https://qa.blog.documentfoundation.org/2026/10/06/qa-dev-report-september-2026/ #foss #opensource #freesoftware
Alt...
Screenshot of font substitution, showing prominent warning
Alt...
Screenshot of button in Calc to switch sheets
Alt...
Screenshot of hyphenation dialog
🎤 Upcoming at SeaGL 2026:
📍 10:30 AM on October 23
🗣️ "Be a Starter, Not a Finisher: For Yourself and For the World"
👥 Speaker(s): Deb Nicholson
📍 Room: Room 332
🏷️ Track: Community and Culture
📝 Even though finishers will nearly always get the credit, starters are the secret power that changes ...
#SeaGL2026 #community #FLOSS #opensource #linux
🔗 https://pretalx.seagl.org/2026/talk/V7RKJW/
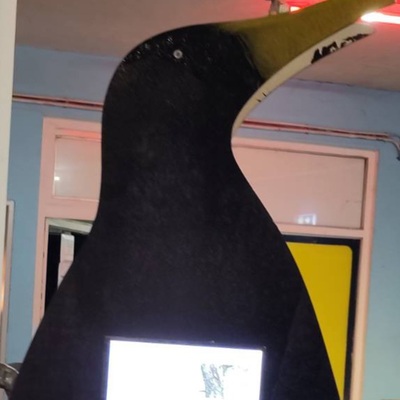
On my way from Vienna to 🇱🇺 Luxembourg for my talk " #Plus1 – How Public Institutions Can Champion Open (Source) Communication" at @oscl
So much looking forward to get to know new people and their projects - all working for a better digital future ✨
#oscl26 #opencommunication #fediverse #opensource #openprotocols

Alt...
Screens at the airport showing the gate information for the flight to luxembourg
How do physical systems stay secure across 20 to 40 year lifecycles?
A new report from LF Research and the Civil Infrastructure Platform (CIP) marks the project's 10 year anniversary by unpacking how open source collaboration solves critical longevity and regulatory challenges.
Read the report: https://www.linuxfoundation.org/research/civil-infrastructure-platform-at-10?hsLang=en
#OpenSource #LFResearch #CIP
Why did #LibreOffice 26.8 get over 4 million downloads in September? We answered this question, and more, in our talk at the recent LinuxDays event in Prague: https://www.youtube.com/watch?v=NHqUdrsEYgE #foss #openSource #freesoftware
Cryptee: end-to-end encrypted docs, notes, and photo storage, encrypted on your device before it leaves.
Markdown, math, to-dos, attachments. Open-source, auditable front-end (MIT).
Alt to Google Docs and Notion.
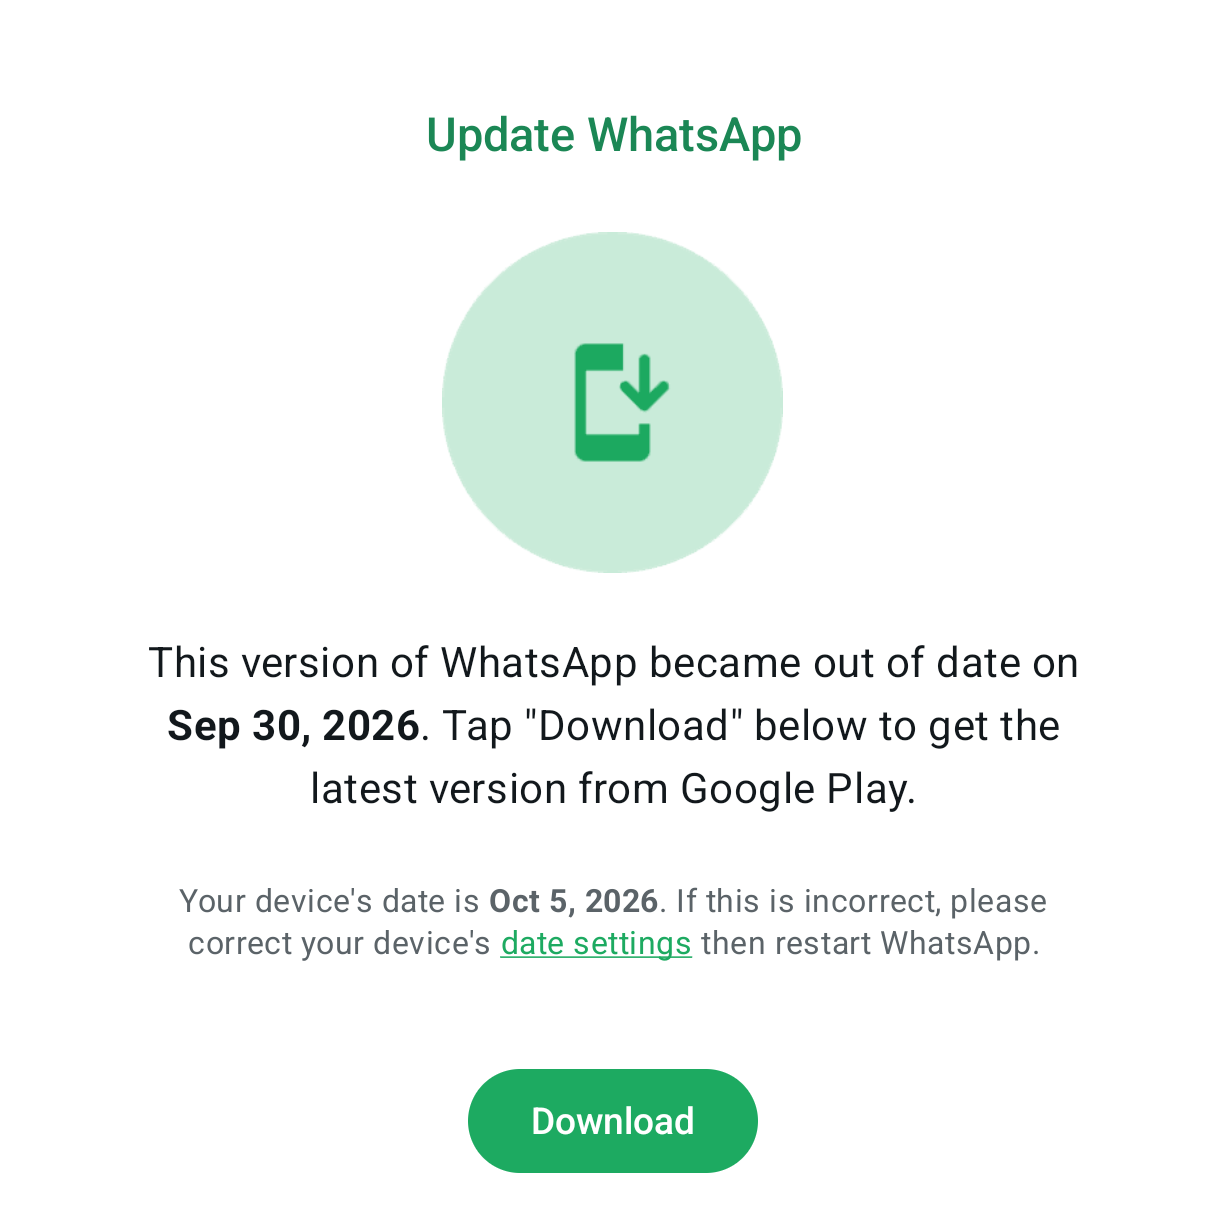
WhatsApp keeps doing it: every a couple of months you wake up and suddenly you can't access your chats anymore, not possible to read important saved notes, etc. you are welcomed with this screen that forces you to update the app, you might be in vacations with expensive roaming data or very bad connectivity or if you are unlucky enough you might be in a country where the app store is not accessible, your data is not YOUR data in WhatsApp, and the reality is: you can lose it at any time they want to take it away from you
On the other side, ArcaneChat users can sleep without worries at night knowing that when they wake up they can keep accessing all their chats, messages and being able to search and use mini-apps, even while offline
With ArcaneChat you really own your data, it is in your pockets, not in the cloud of some corporation you have to beg access to
#ArcaneChat #autonomy #Europe #European #eu #privacy #encryption #WhatsApp #Meta #freedom #opensource #security #digitalindependence #diday #chat #messenger
Meet SeaGL 2026 keynote speaker Bradley M. Kühn, Policy Fellow and Hacker-in-Residence at Software Freedom Conservancy.
Bradley's decades in the software freedom movement include GPL enforcement, inventing the Affero GPL, and advancing copyleft licensing policy.
📅 Sat, Oct 24 at 5:30 PM PT
🔗 https://pretalx.seagl.org/2026/talk/HTMWCX/
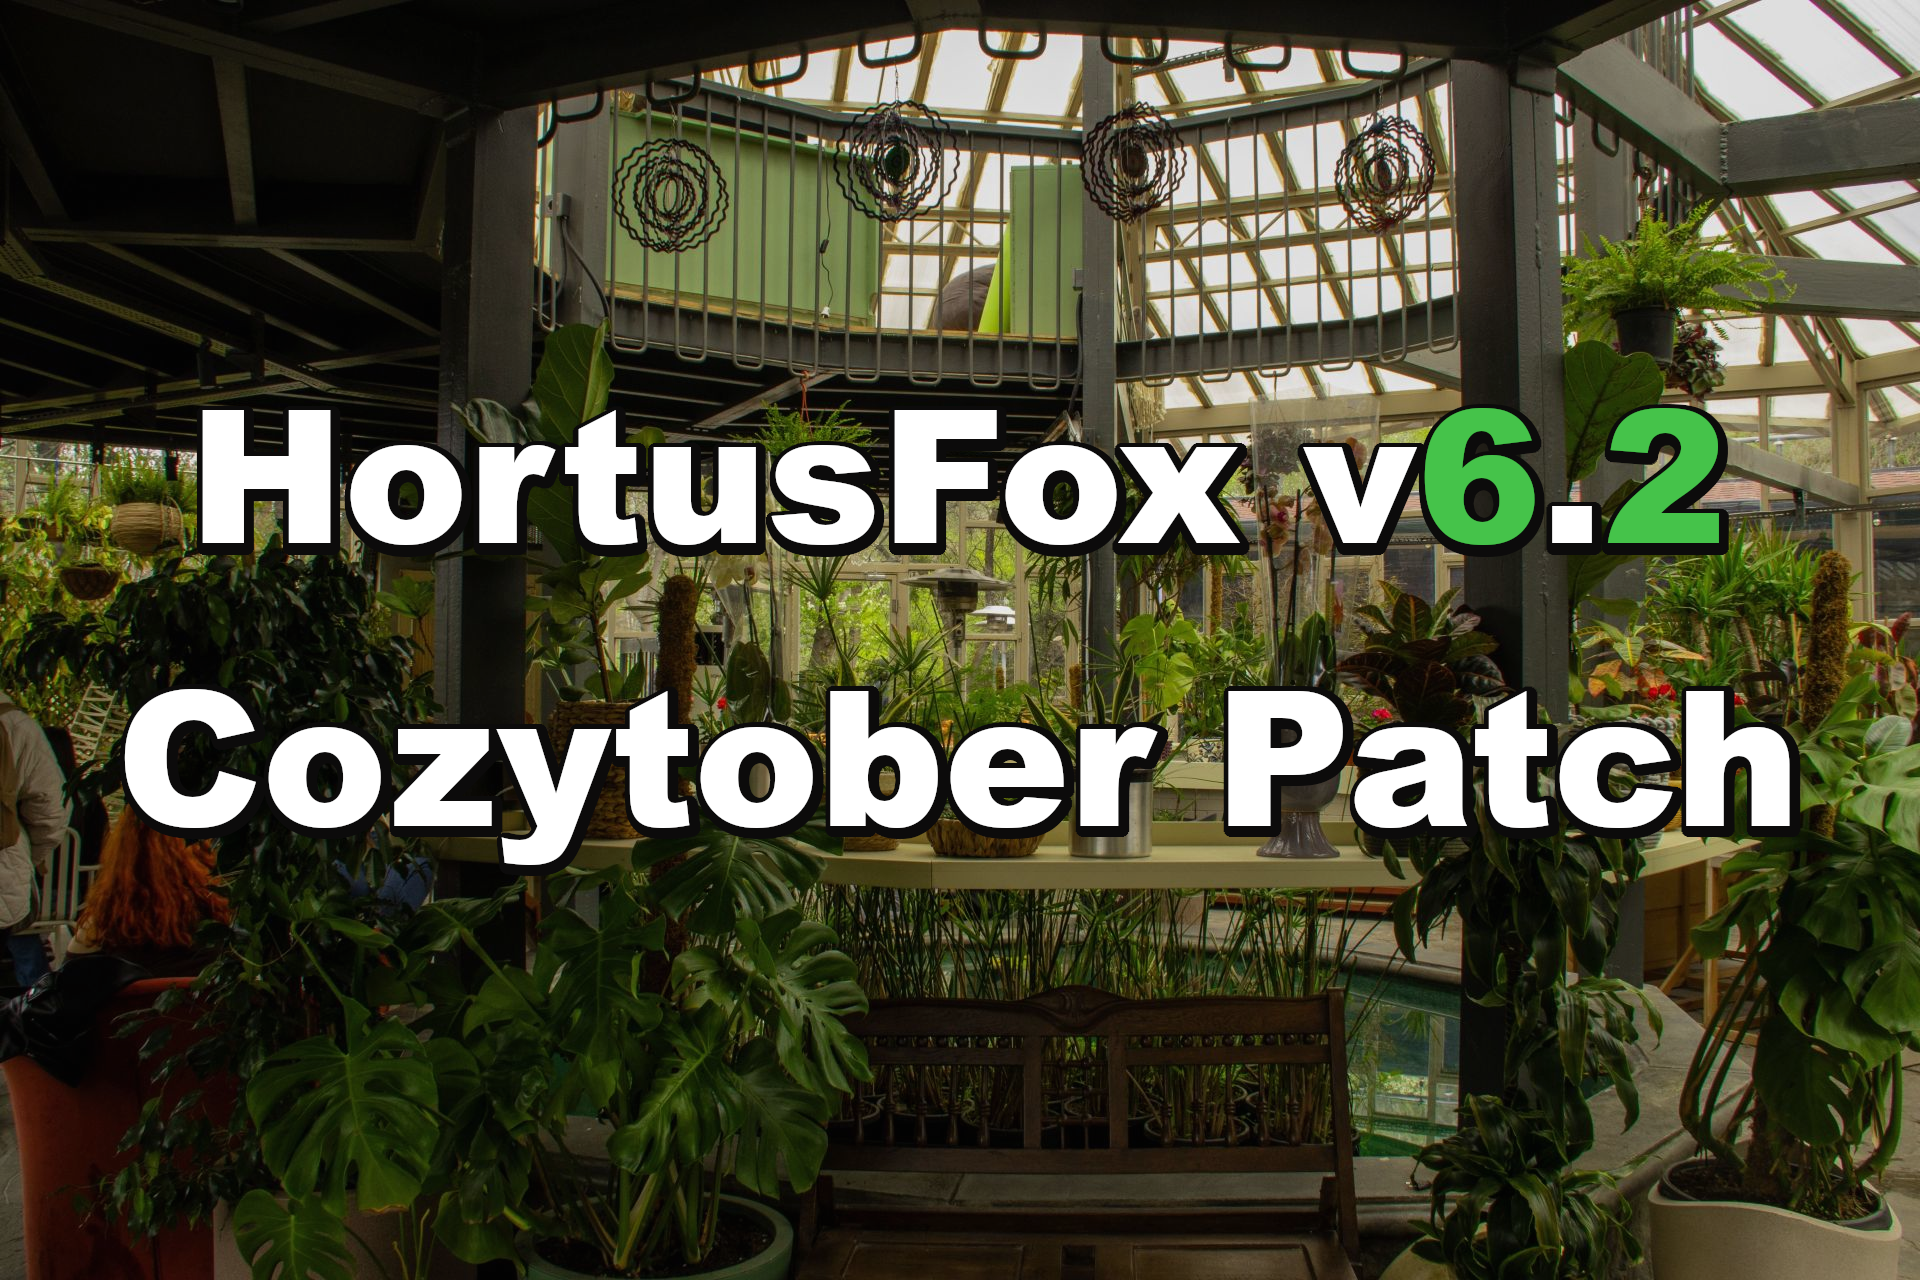
HortusFox v6.2 - Cozytober Patch published 🎃
Italian translation, various security patches, and new console commands have been implemented in the latest release. 💚
➡️ View release here:
https://github.com/danielbrendel/hortusfox-web/releases/tag/v6.2
#HortusFox #FOSS #OpenSource #SelfHosted #SelfHosting #Plants #Garden #Botany
Alt...
In the front the following text is shown:
HortusFox v6.2
Cozytober Patch
In the back there is a greenhouse with various plants, benches, a fountain and fences.
Background image credits to Nazlı Isguven @ Pexels
🎤 Upcoming at SeaGL 2026:
📍 09:10 AM on October 23
🗣️ "The mv Command Doesn't Move Things & Other Stuff New Users Don't Know"
👥 Speaker(s): Toby Betts
📍 Room: Room 250
🏷️ Track: Keynote
📝 If you think Linux dating all the way back to 1991 is old, wait'll you hear about AT&T UNIX. This ta...
#SeaGL2026 #keynote #linux #FLOSS #opensource
🔗 https://pretalx.seagl.org/2026/talk/TGRTZU/
For Adlair Cerecedo-Méndez, his work with #LibreOffice began as a response to a specific need: helping the Mexican government obtain an office suite tailored to public institutions: https://blog.documentfoundation.org/blog/2026/10/05/community-member-monday-adlair-cerecedo-mendez/ #foss #opensource #freesoftware
Alt...
Photo of Adlair

Our Early Birds keep the questions coming.
This week: Does Thundermail have webmail?
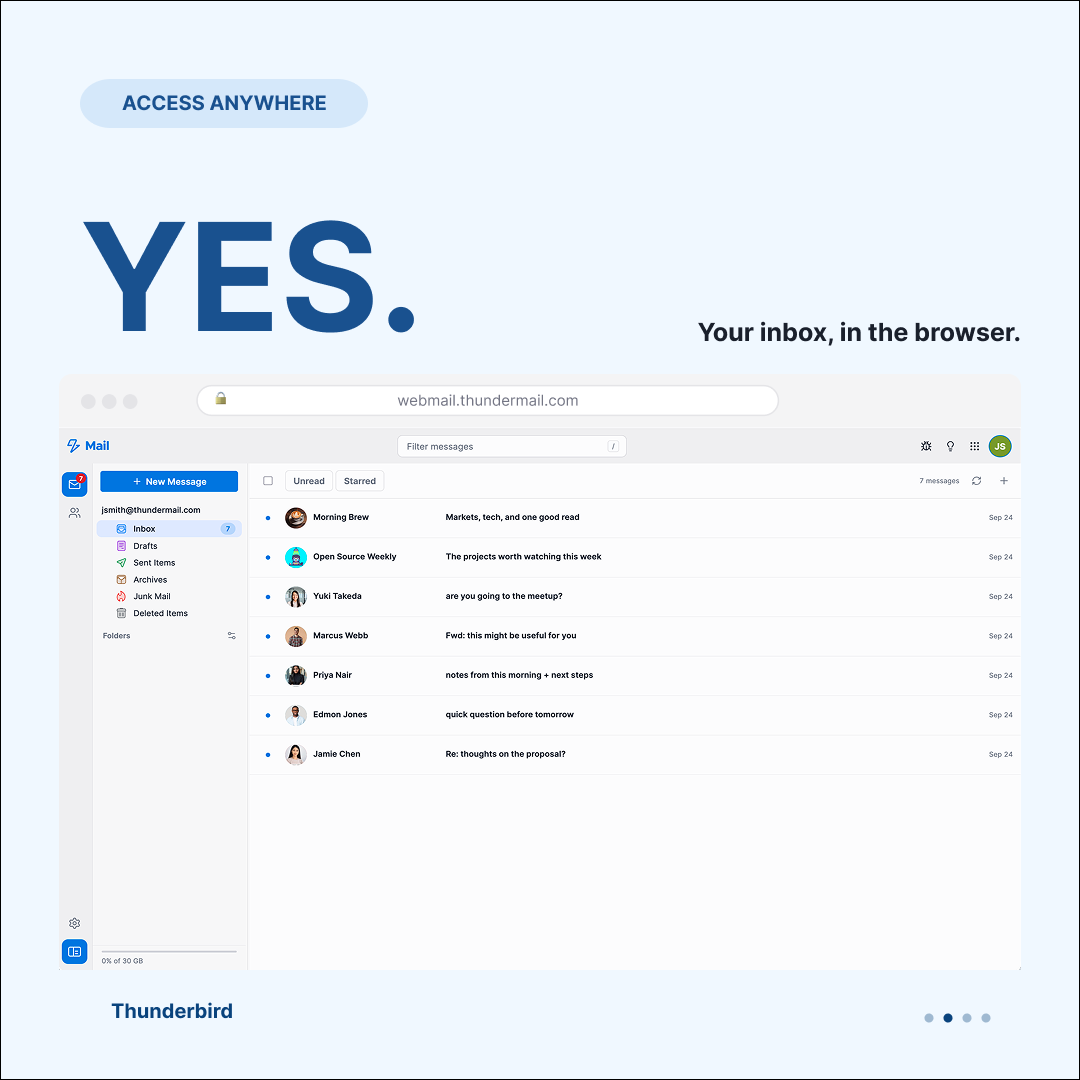
Yes! Your inbox is accessible from any browser. We're in early alpha and moving fast, so more is on the way. Check out our support article 👉 https://support.tb.pro/hc/en-us/articles/55712158355603-Is-Webmail-available
Not on the waitlist yet? Sign up: https://sohub.io/tifi
#thundermail #opensource #email
Alt...
Thundermail FAQ slide on blue gradient background asking “Does Thundermail have webmail?” and explaining beta webmail service.
Alt...
Thunderbird promo showing Thundermail webmail inbox in a browser with text “Access anywhere. YES. Your inbox, in the browser.”
Alt...
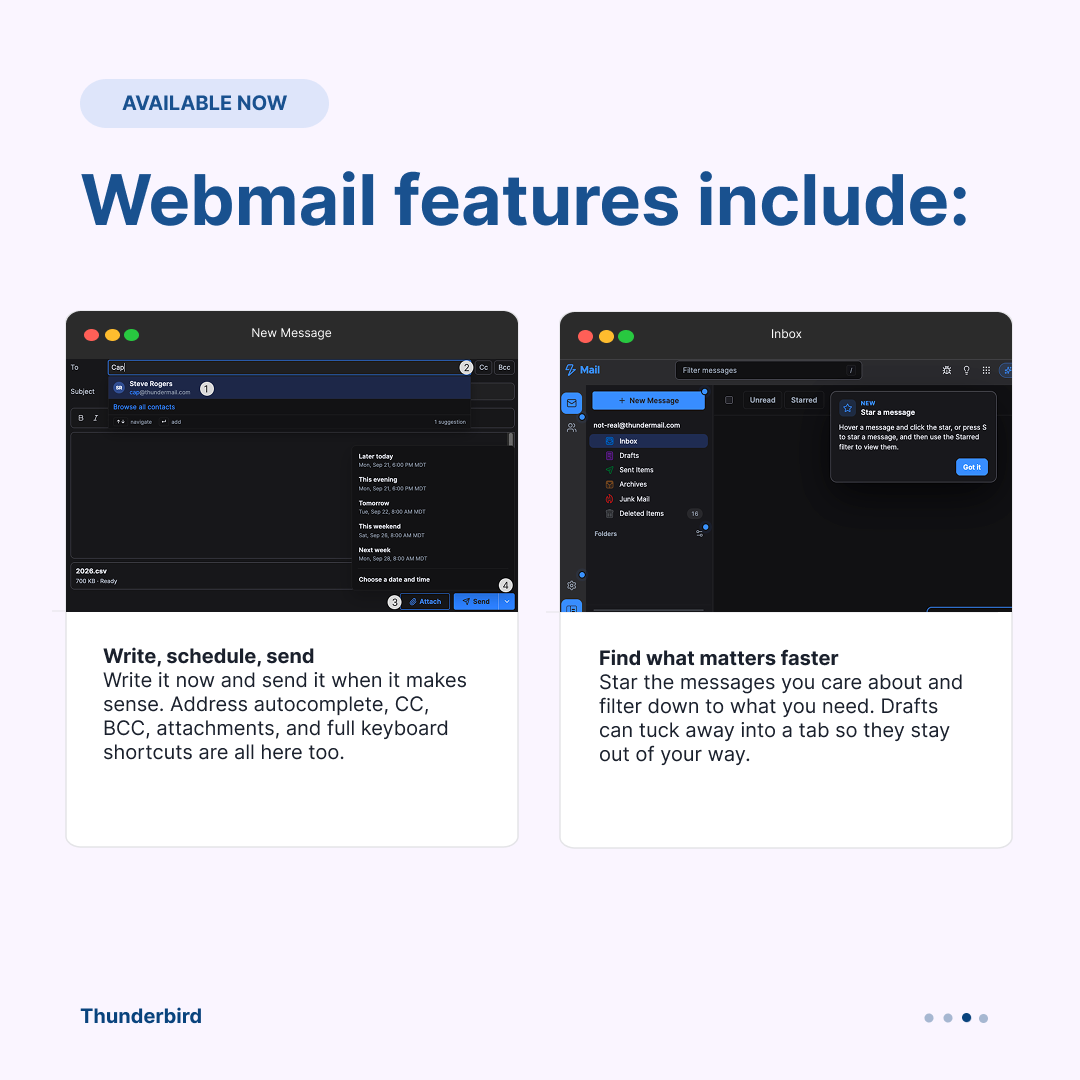
Thunderbird webmail feature slide showing compose and inbox screens with text on writing, scheduling, and finding important messages faster.
Alt...
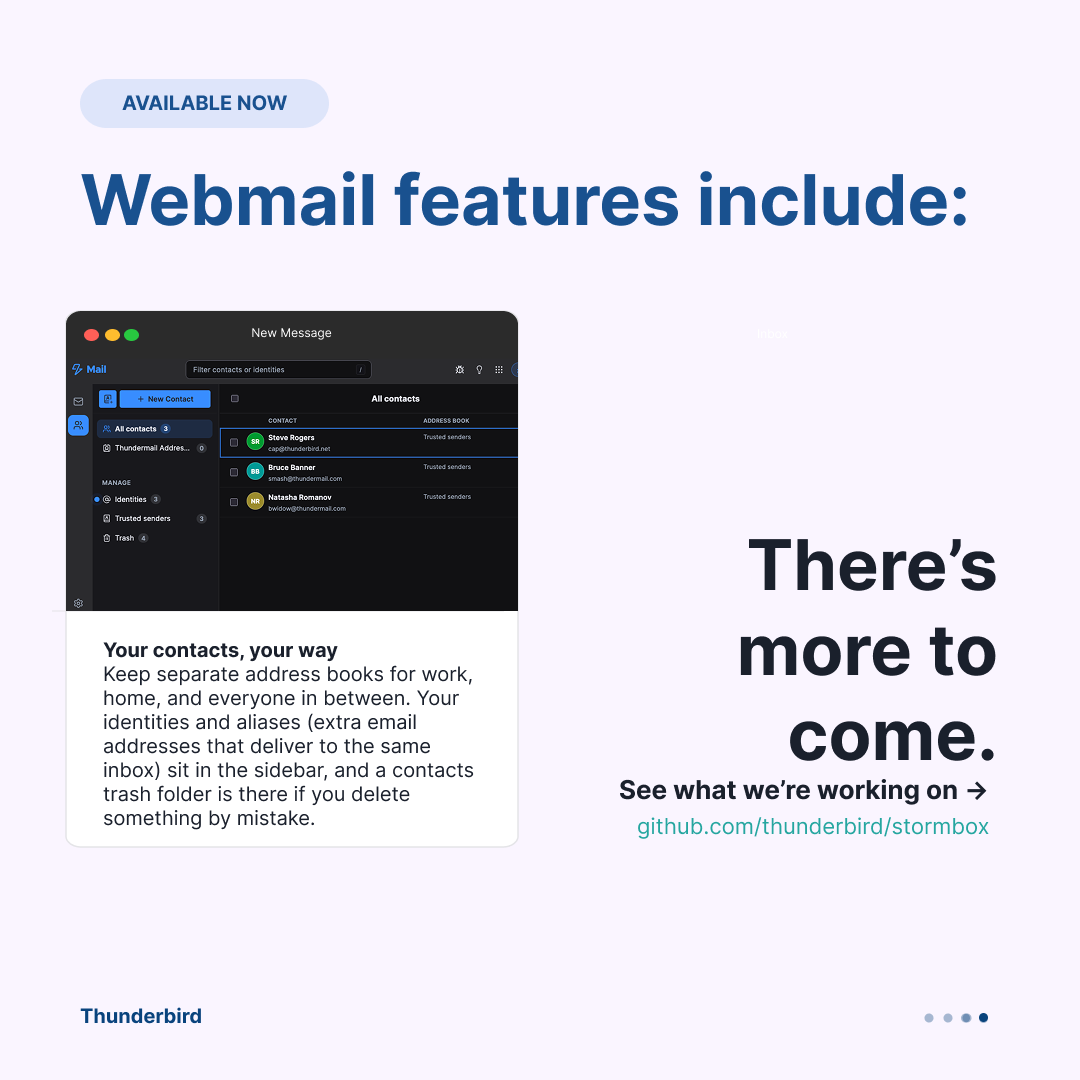
Thunderbird webmail feature card highlighting contact management with text “Webmail features include: Your contacts, your way.”
Release candidate 10.8.13.rc0 of 🐙passagemath, a comprehensive #OpenSource #Mathematics system in #Python, the pip-installable modularized portable compatible full-featured fork of #SageMath.
#CAS updates: Maxima 5.50, Mathilda 0.254 (now with a @jupyter.org@bsky.brid.gy kernel)
github.com/passagemath/...
Want a fitness tracker you actually control?
openGym is an open-source, self-hosted workout tracker for planning routines, logging sets, tracking body weight, and monitoring progress.
Your data stays on your server no subscription, ads, or telemetry. Supports passkeys, offline use, sync, Docker, and a standalone Android APK.
More details & alternatives: https://digitalescapetools.com/tools/opengym.html
#OpenSource #SelfHosting #Privacy #Fitness #FOSS #Docker
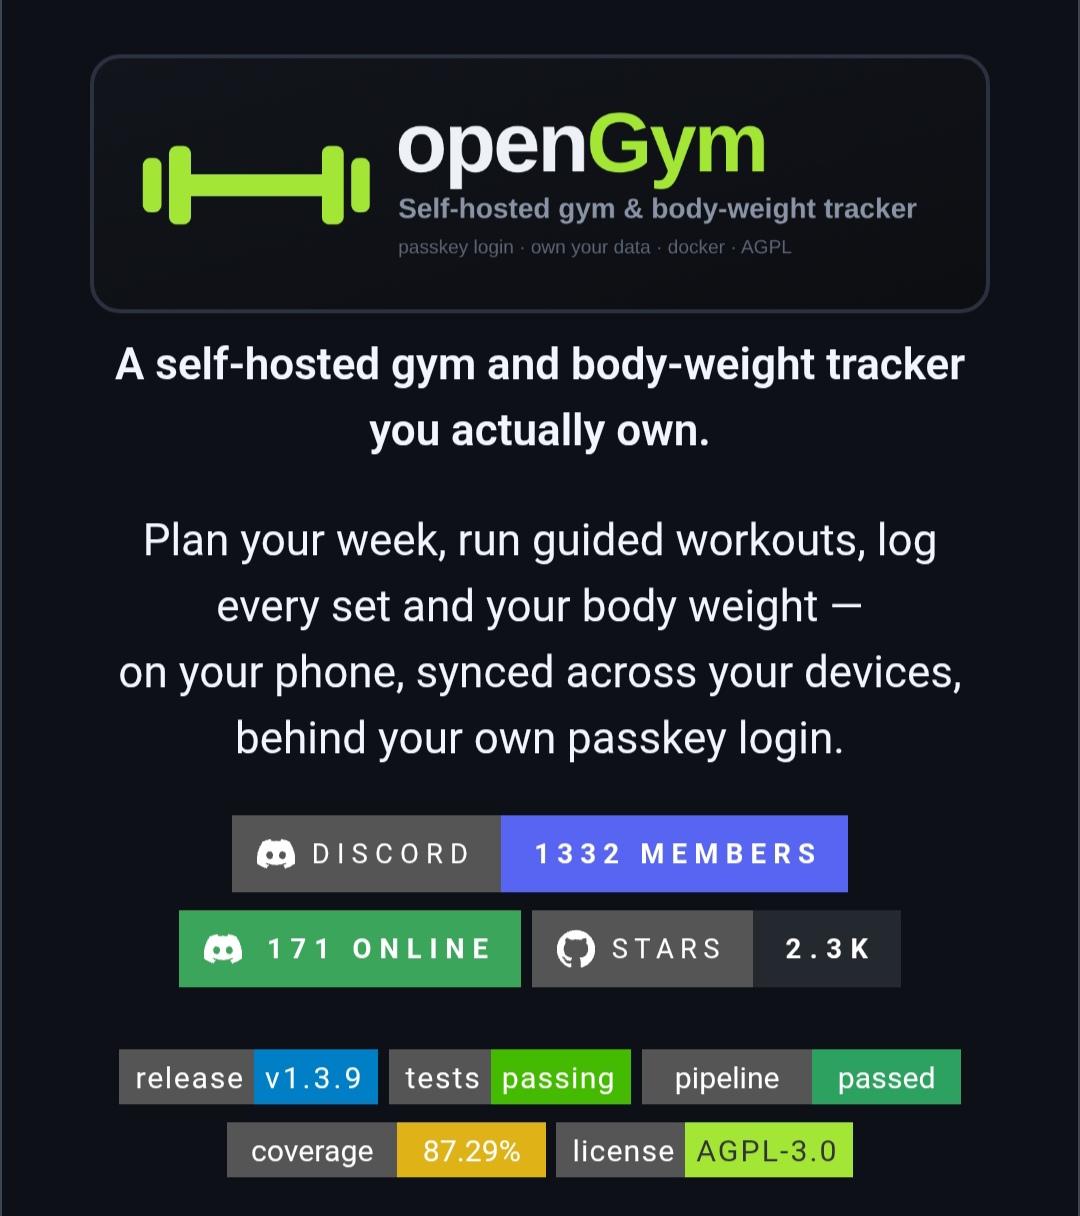
Alt...
OpenGym self-hosted gym and body-weight tracker landing page with feature and community stats.
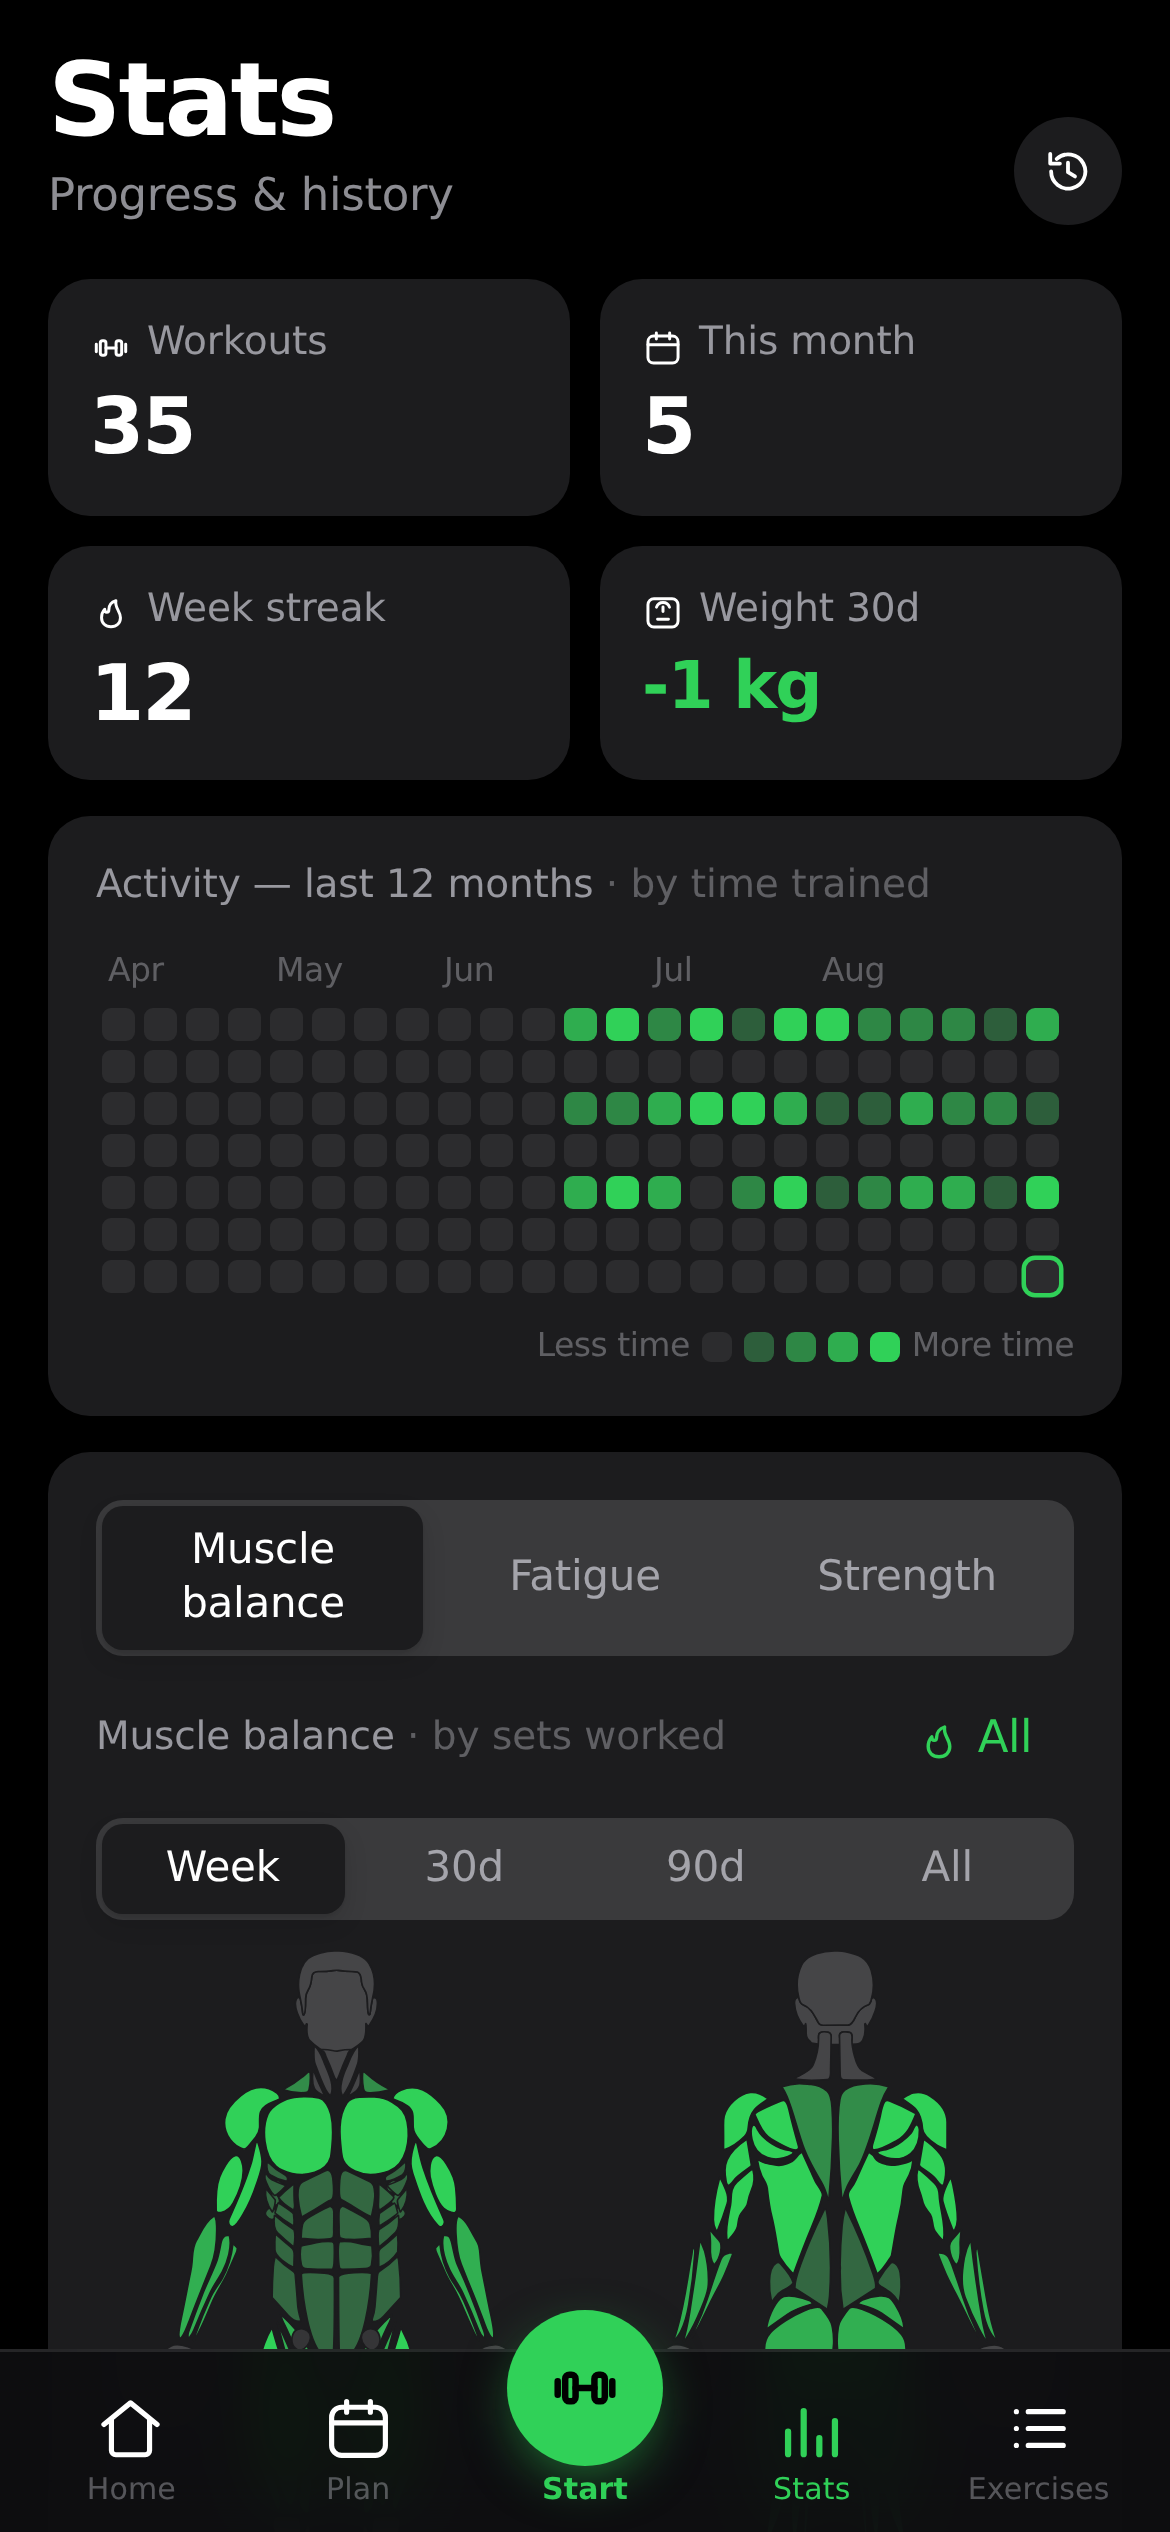
Alt...
OpenGym stats dashboard showing workouts, streak, weight progress, activity, and muscle balance.
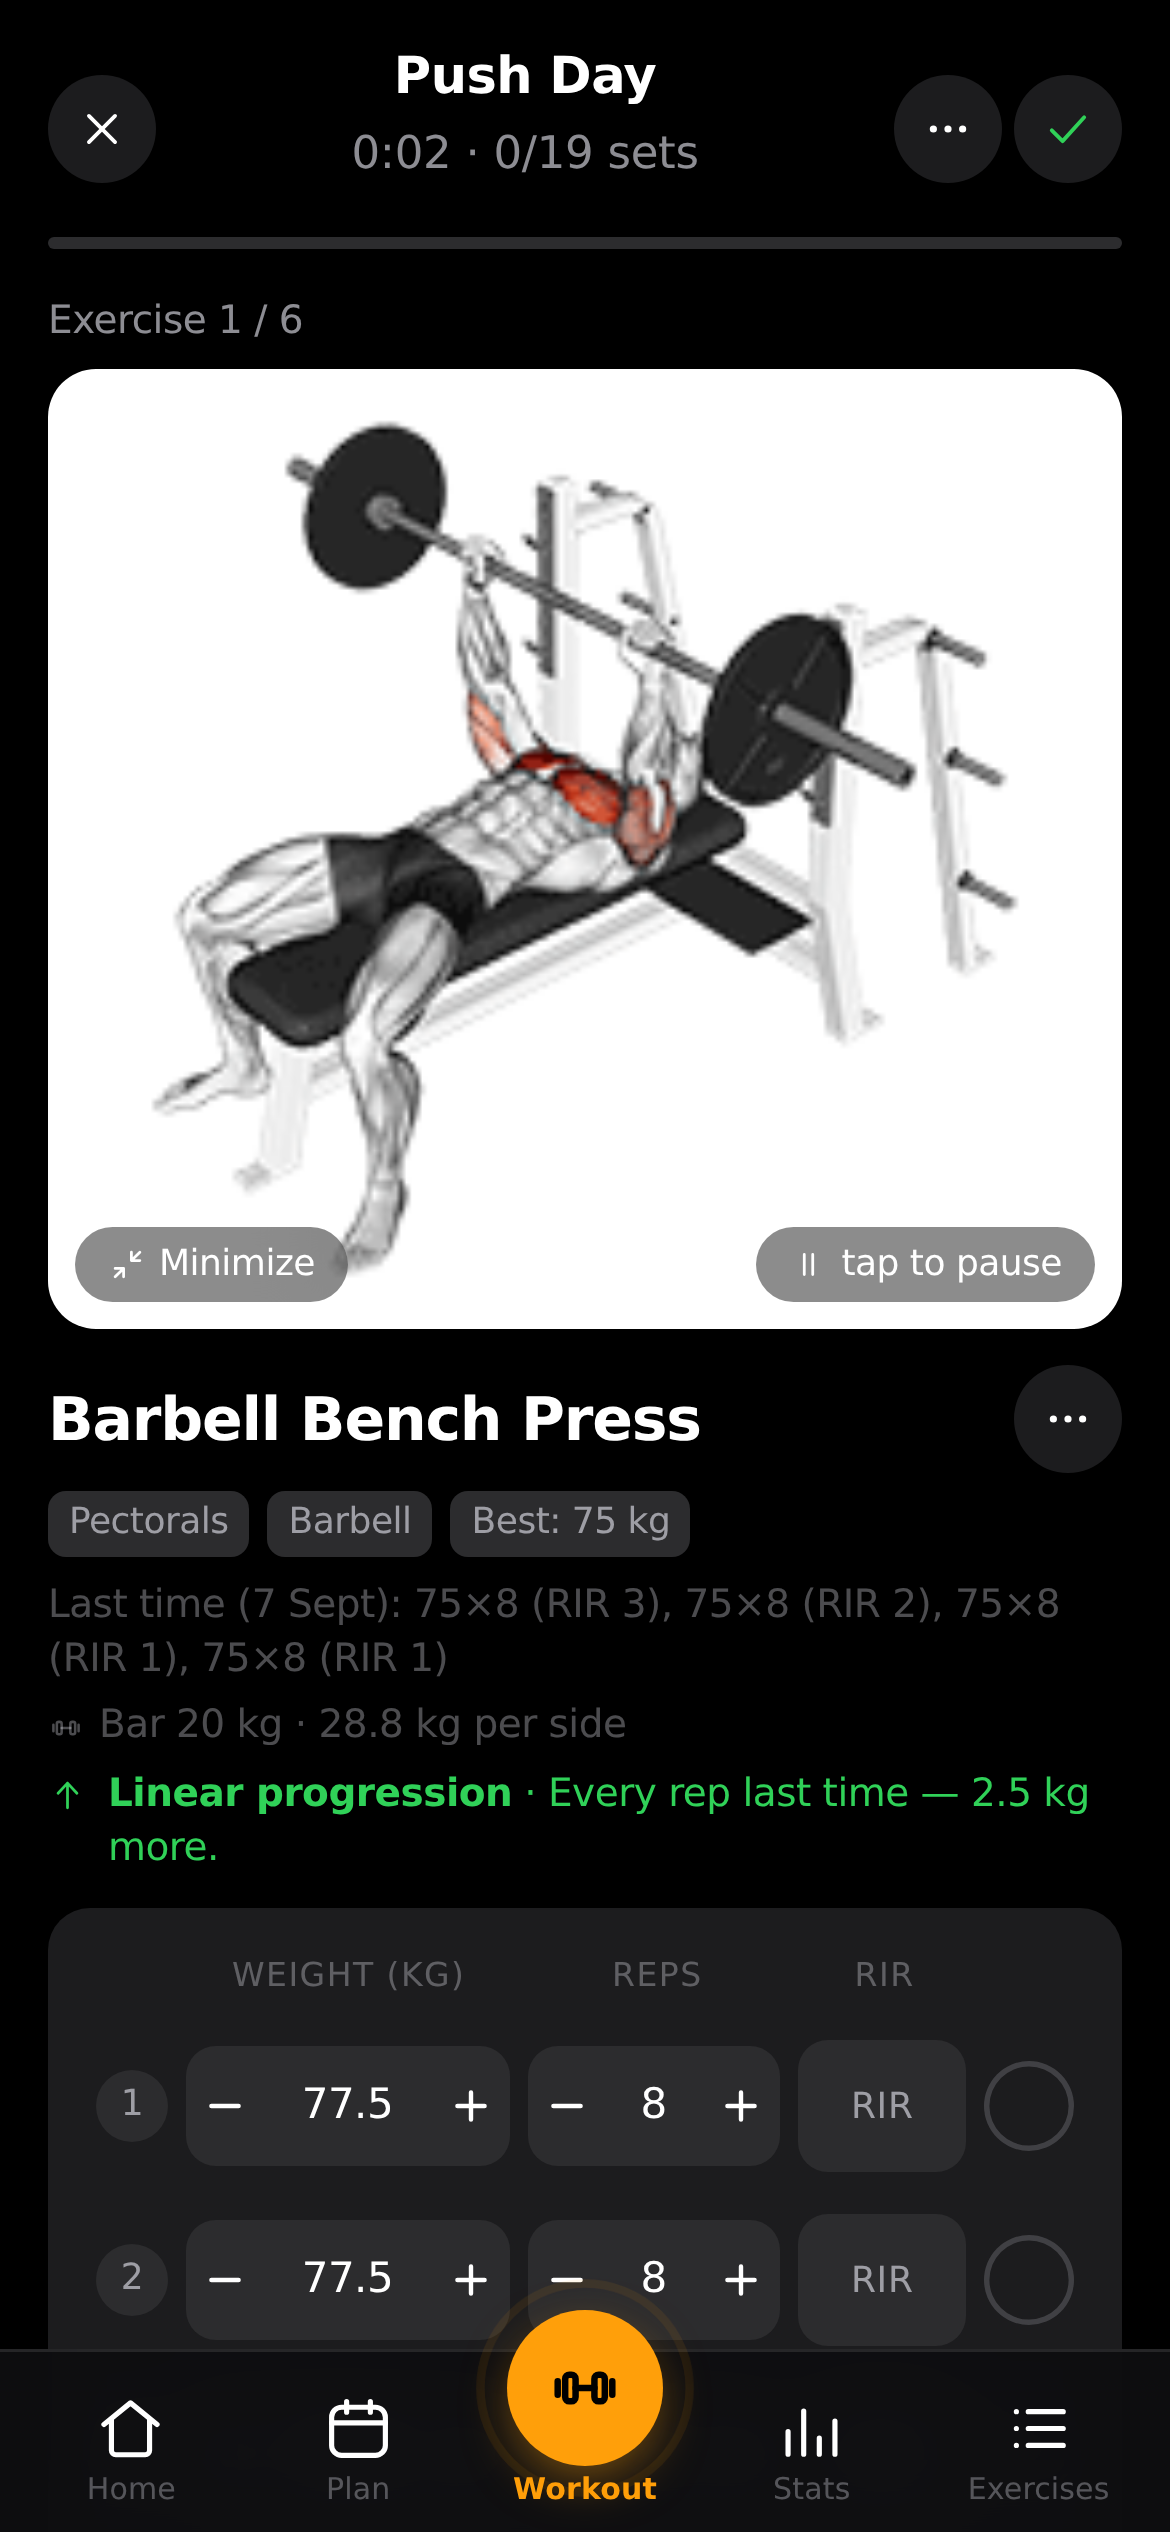
Alt...
OpenGym Push Day workout screen showing barbell bench press with weight, reps, and progression details.
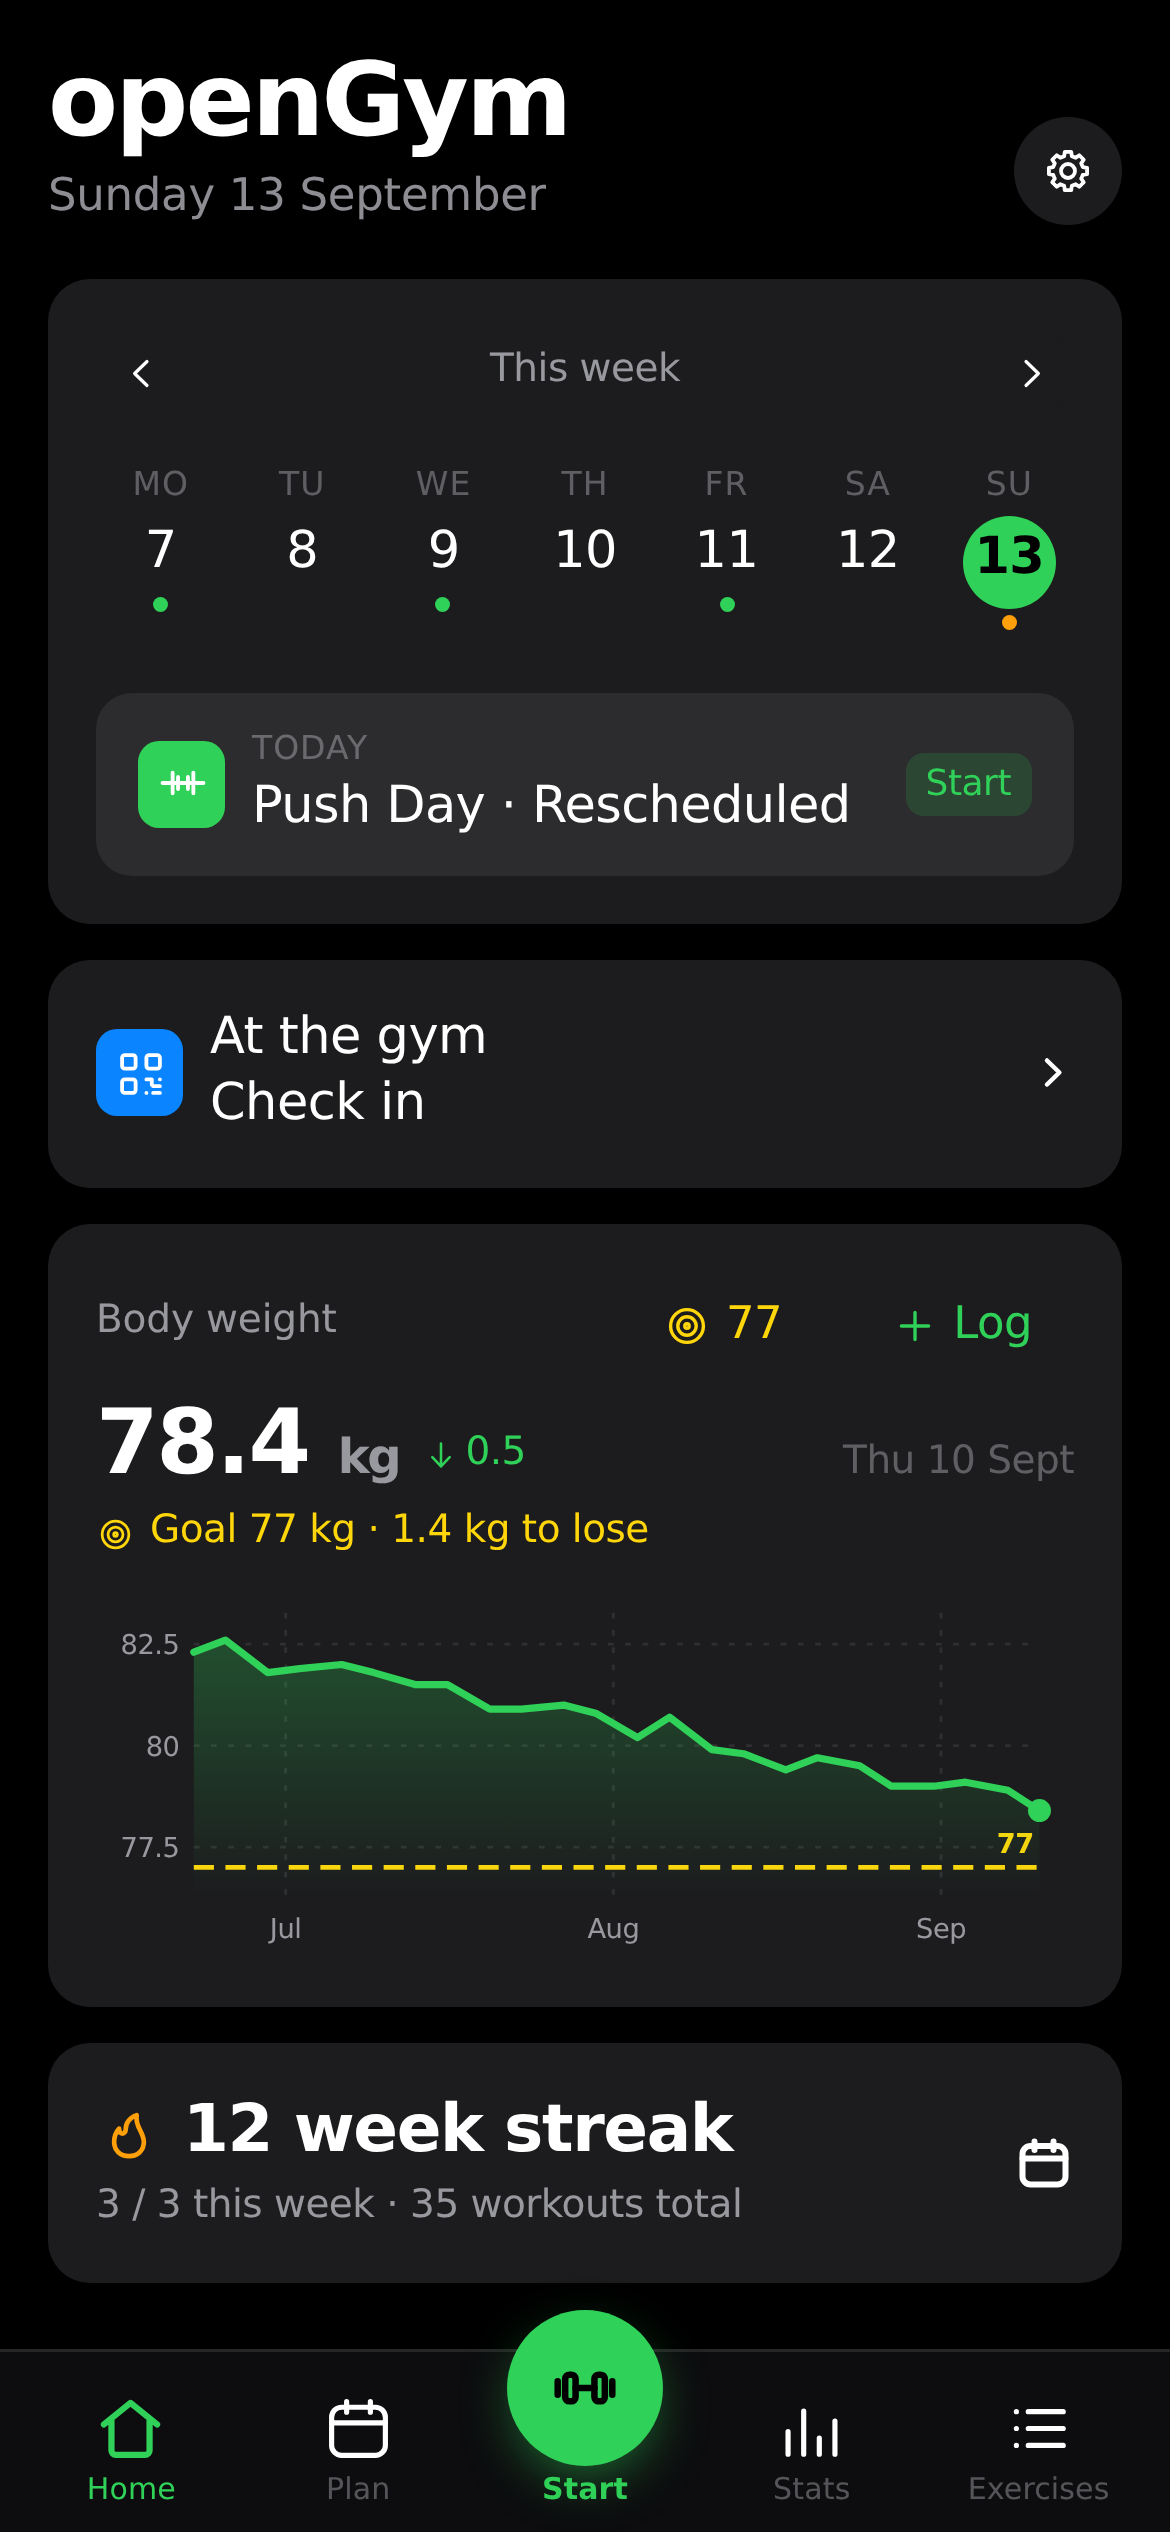
Alt...
OpenGym home screen showing weekly schedule, body-weight progress toward a 77 kg goal, and a 12-week streak.
ArcaneChat / DeltaChat channel for you:
Debugging Memes - developer&linux memes, open source and other nerdy and tech related stuff, to join click here:
discover that and many more channels at:
https://arcanechat.me/channels
#memes #fun #meme #channel #decentralization #encryption #e2ee #ArcaneChat #DeltaChat #linux #opensource #gnulinux #developers #development #dev #ai
Development has ended on the Linux port of Orion browser.
Kagi, the company who made it, says it plans to open source the code this month, but will not be continuing work itself. Users of the Linux beta will get no further updates.
https://www.omgubuntu.co.uk/2026/10/orion-linux-browser-development-ended?v1

This hasn't gotten much publicity yet, probably because finite element solvers are not quite as popular as, say, graphics drivers and office software, but the company that was maintaining and hosting OpenRadioss was bought by Siemens, which promptly shut it down. The OpenRadioss repositories have been removed.
#OpenRadioss #Siemens #OpenSource
Fortunately, ...
[-more-]
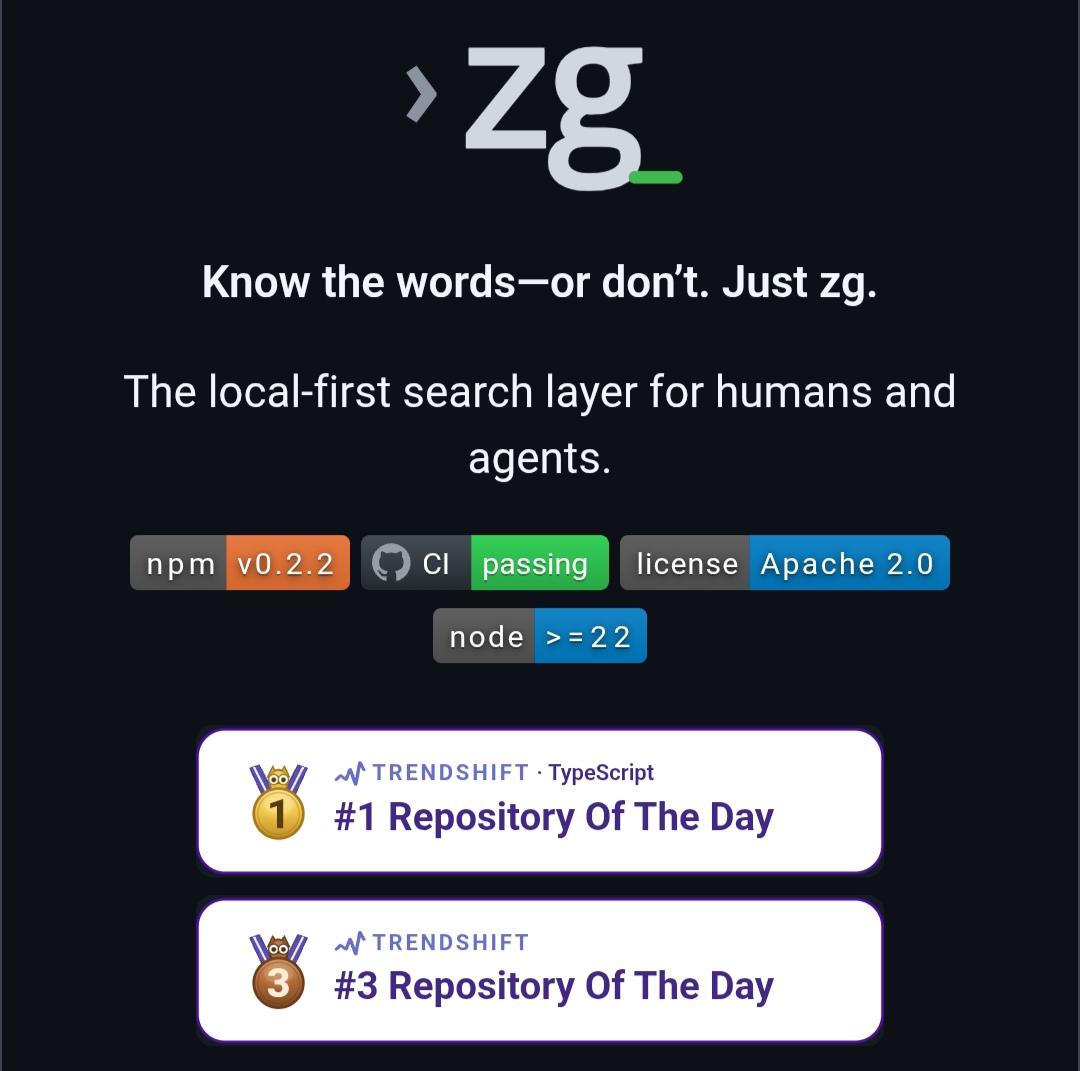
zvec-grep (zg) combines exact text search, ranked search, and AI-powered semantic search in one local-first CLI.
Search code, documents, and data by meaning or exact text while keeping your files and indexes on your machine by default.
More details & alternatives: https://digitalescapetools.com/tools/zvec-grep.html
#OpenSource #Privacy #SelfHosting #AI #DeveloperTools
Alt...
Screenshot of the zvec-grep (zg) project page, describing it as a local-first search layer for humans and agents, with npm, GitHub CI, Apache 2.0 license, Node.js 22+ badges, and Repository of the Day awards.
One of many changes in GNOME 51 also includes changes to Loupe, our Image Viewer. It now shows more image information such as:
・Creator
・Copyright
・Equipment used (e.g. camera lens)
・Color profile
Meet KEMchatka: an experimental, serverless P2P terminal chat over Tor hidden services.
No accounts, no port forwarding, zero disk logging.
Features hybrid post-quantum encryption: X25519 + ML-KEM-1024 (FIPS 203) combined via HKDF-SHA512 to defeat "harvest now, decrypt later" attacks. Simple out-of-band setup.
When privacy is under threat, build tools that protect it.
https://github.com/bashcore/kemchatka
#PostQuantum #Tor #Python #CyberSecurity #Privacy #OpenSource #Cryptography


WhatsApp Clone, but Decentralized with P2P Messaging
"Secure and private" is the general goal.
This is a technical/concept demo of a fairly unique approach using a browser-based, local-first and webrtc.
This is intended to introduce a new paradigm in client-side managed secure cryptography. We can avoid registration of any sort.
Features:
* P2P
* End to end encryption
* Signal protocol
* Post-Quantum cryptography
* File transfer
* Local-first
* No registration
* No installation
* No database
* TURN server
Feel free to reach out for clarity instead of diving into the docs/code.
IMPORTANT: While this is aiming to provide a secure experience, it isnt audited or reviewed. **Shared for testing, feedback and demo purposes only.** Please use responsibly.
#Privacy #OpenSource #P2P #WebRTC #Decentralization #DigitalSovereignty #CyberSecurity #FOSS #SelfHosted #NoCloud #AntiCorp #Encryption #WebDev #TechLiberty #PrivateMessaging #Networking #DataPrivacy #InternetFreedom #LocalFirst #SoftwareEngineering #WebApps #ZeroKnowledge #PrivacyTech #IndieDev #NoSignup #NoInstall #DecentralizedWeb #SecureMessaging #BrowserApp #TechEthics #P2P #WebRTC #PeerJS #ZeroData #EphemeralData #Encryption #E2EE #BrowserToBrowser #NoInstall #Privacy #Security #Decentralized #Messaging #VideoCall #NoTracking #PrivateMessaging #Prototype #Demo #WorkInProgress #CloseSource #OpenSource #WebDev #GitHub #TechDevelopment #WhatsApp #ChatApp #InstantMessaging #PWA
eMule is back, reborn as aMule 3.0.0. 380x faster downloads.
5 years of silence, broken. 🔥
What this means for P2P is bigger than you think.
https://geekrealmhub.com/amule-3-0-0-faster-p2p-sharing/


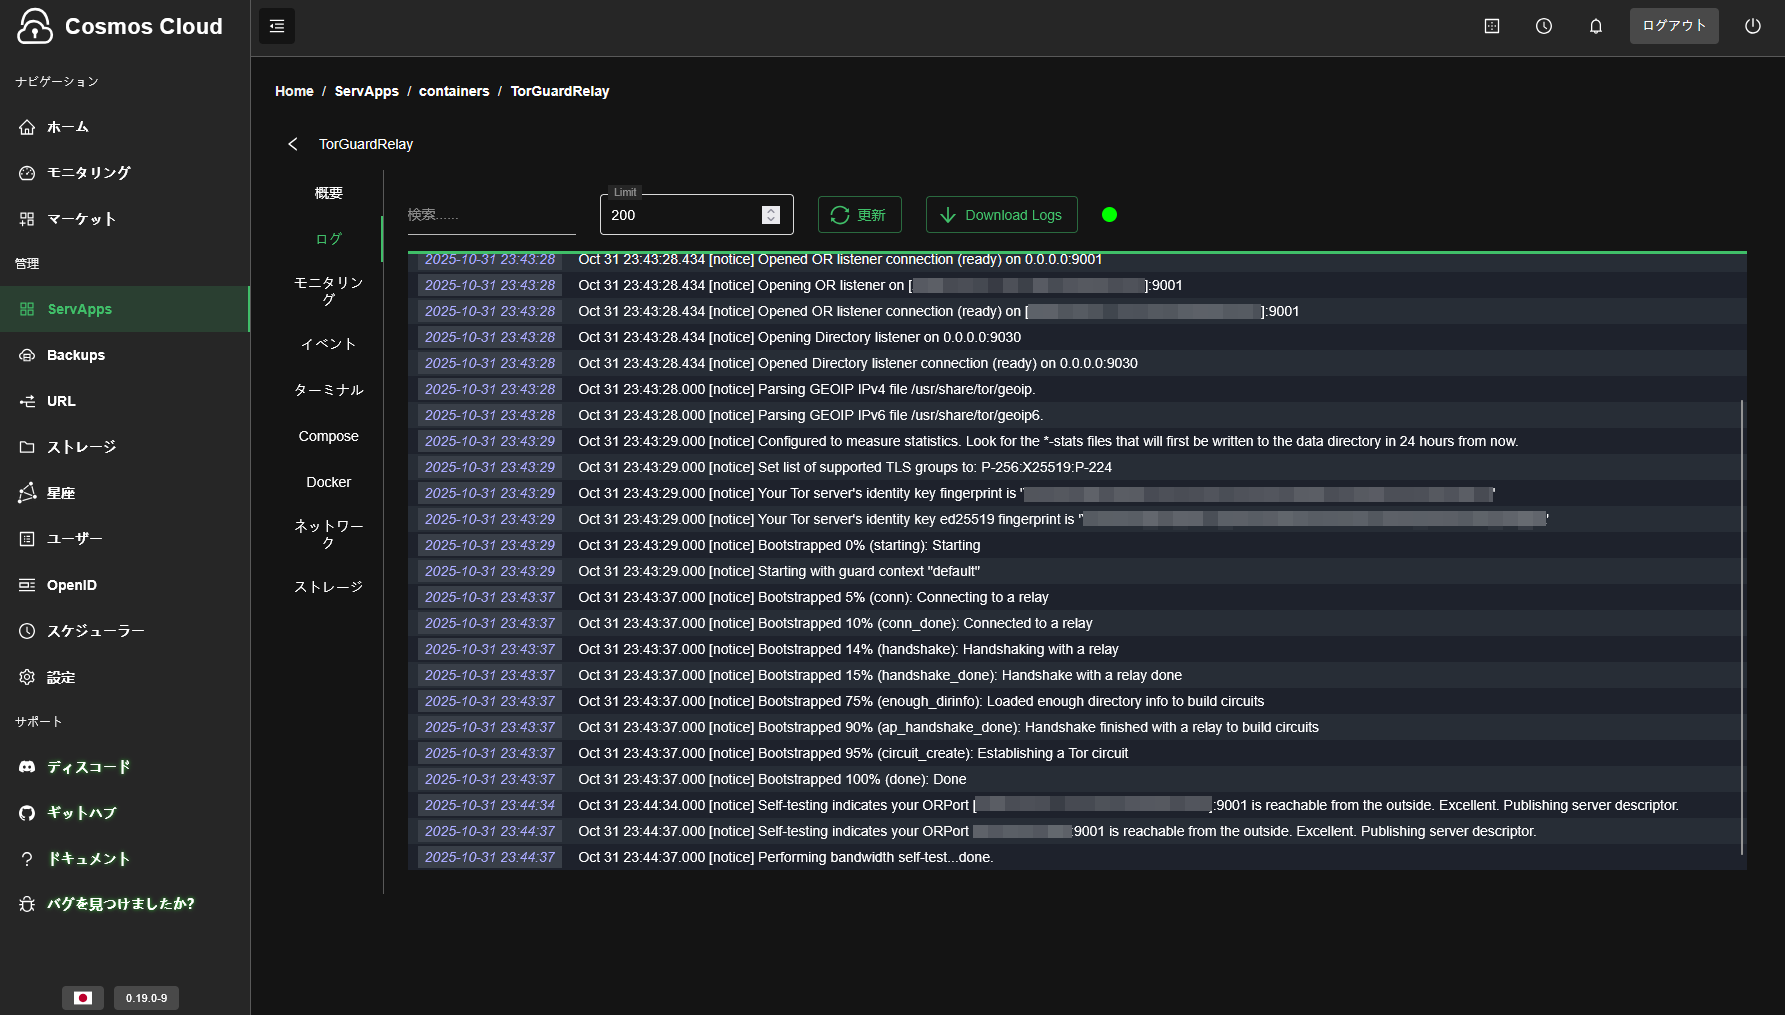
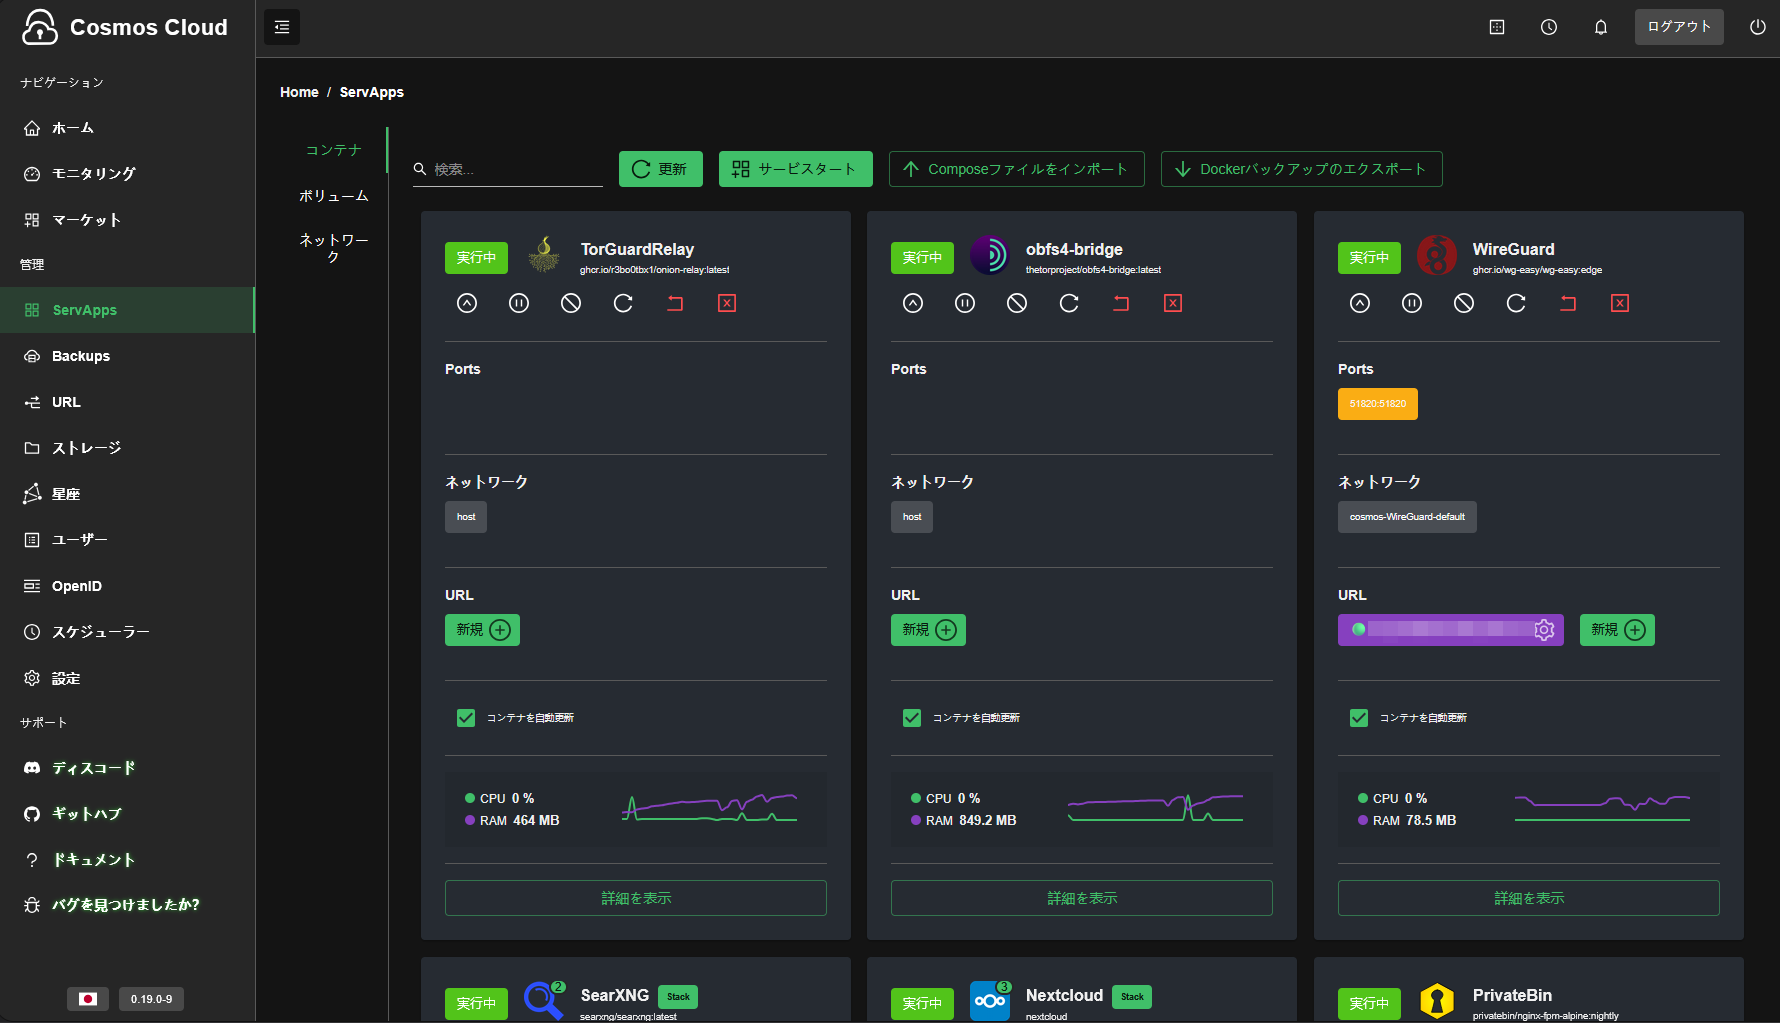
 Built something I’ve wanted for a while...
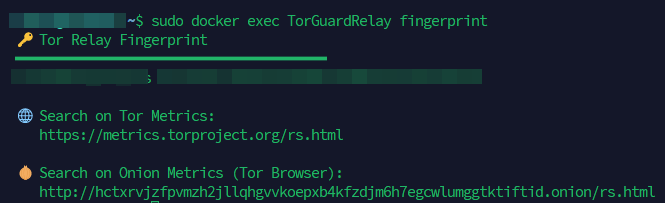
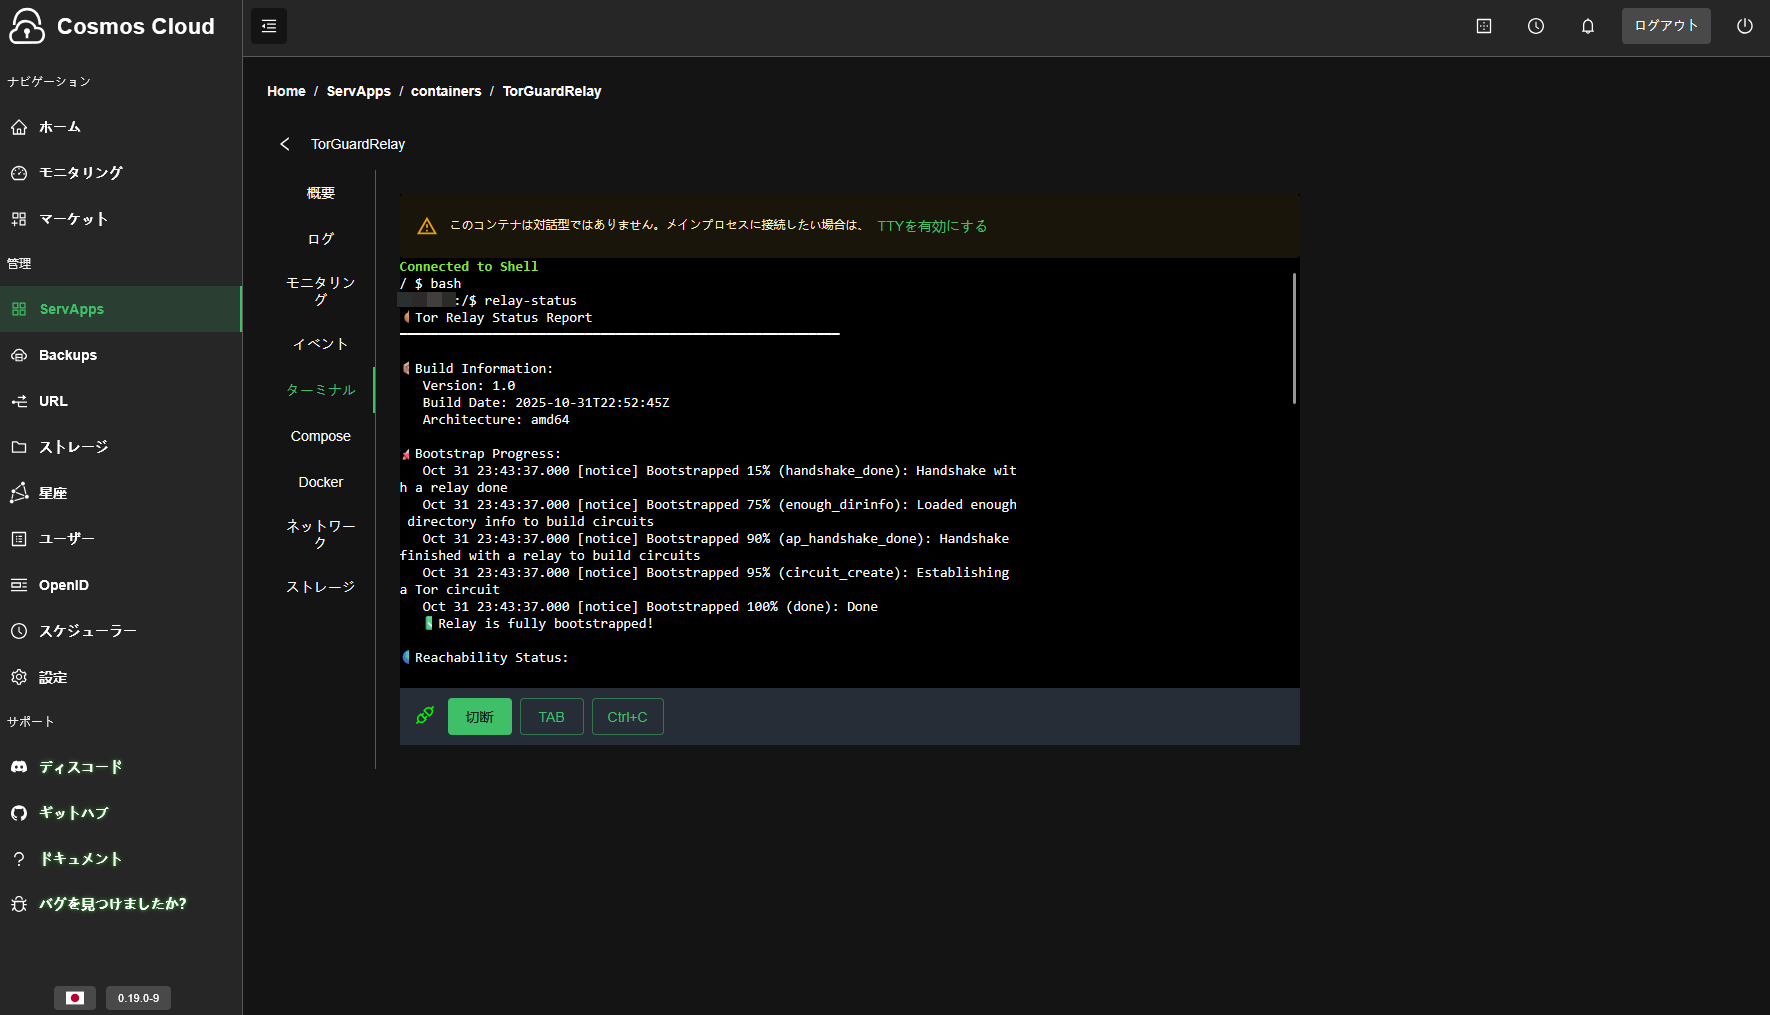
An open-source Docker container that makes running a Tor relay actually simple and reliable.
One command. Self-healing. Multi-arch. Runs everywhere from Raspberry Pi  to VPS

🔗 https://github.com/r3bo0tbx1/tor-guard-relay
If you care about privacy infrastructure:
🧱 Try it out
🐛 Report bugs
💡 Suggest features
⭐ Star it to help others discover it
 Maintaining this in my free time, donation info’s in the README (and please support @torproject, @eff and @privacyguides too).
Protecting privacy, one relay at a time ✨
#Tor #Privacy #OpenSource #Docker #FOSS #SelfHosting #Infosec

[3D Printer Laws aren't about guns]
[copypasta]
California AB 2047: The End of Open Source 3D Printing
California just introduced a bill that doesn't just regulate "ghost guns", it mandates a digital kill switch for every 3D printer sold. California AB 2047 requires "blocking technology" that connects your printer to a government-approved database before every single print. If the system goes down, or your file is flagged, your hardware becomes a paperweight.
This isn't just about firearms. This is the death of Open Source. If this bill passes, it effectively bans Marlin, Klipper, and Orca Slicer, forcing every manufacturer to lock down their firmware. It turns general-purpose computing into a walled garden where you only rent permission to use the hardware you own.
[/copypasta]
#OpenSource #RightToRepair #Privacy #Clippy #California #Monopolies #3dPrinters #3dPrinting #Technology #Government #Firearms #Guns #SoftwareFreedom #Surveillance #Panopticon #Lobbyists
All the donor-funded foundations ought to be fighting against and speaking out against this Orwellian garbage.
@eff@mastodon.social
@fsf@hostux.social
@linuxfoundation@social.lfx.dev
@privacyint@mastodon.xyz
@openssf@social.lfx.dev
@rms@mastodon.xyz
@CCIAnet@techpolicy.social
@WriterOfMinds@sigmoid.social
@SeaGL@mastodon.social
@hopeconf@mastodon.online
@w3c@w3c.social
@ACM@mastodon.acm.org
@irtf@discuss.systems
@osi@opensource.org
"While the [age verification] bill moved through the legislature, the OSI, FSF, Software Freedom Conservancy, and Linux Foundation all sat it out — no testimony, no public analysis, no formal opposition on the record."Are the adults listening?
California's computer age verification law is poison. The new California age verification law is a version of INGSOC's telescreen watching you. And the usual self-proclaimed software freedom fighters are AWOL as this attack on your freedom is executed.
Don't listen to apologists who claim this isn't a big deal. It is a huge deal. This law is not about protecting children. The California law is a ruse for laying the foundation and precedent for mandatory remote control of all operating systems. They are using children as a shield for their true intentions. It's called a 'subterfuge' or a 'pretext' to hide the real rationale. And in politics subterfuge is very common. These politicians don't care about your children. They care about control and information is control. Compliance with California's new law is highly corrosive to free software and deadly to personal privacy.
With the mandatory age verification API in place, legislators can later add more laws mandating retrieval of even more privacy-invasive information just to install and use any operating system. This is Big Brother's telescreen in your living room. And the Linux community is nearly silent on the matter, instead focused on artificial intelligence investment.
Where were the software freedom organizations when California was mandating installation of #spyware in all free and open source operating systems? Did they oppose it? Or did they support it by silence? The California age verification law is the greatest threat to software freedom in recent history., striking right at the root of software installation for all users. Yet (((crickets))).
Is silence really tacit support?
"While the [age verification] bill moved through the legislature, the OSI, FSF, Software Freedom Conservancy, and Linux Foundation all sat it out — no testimony, no public analysis, no formal opposition on the record."[https://boingboing.net/2026/03/02/californias-age-verification-law-could-regulate-every-linux-command.html]
Where were they when this mandatory spyware infrastructure was being shoved down our throats? Where were the self-proclaimed software freedom fighters? Where were the calls to action? I didn't see any.
Is silence golden ... or is gold buying silence?
Let these organizations know that you oppose California's age verification spyware law and that you expect them to rally in defense of true software freedom--freedom from government oversight of your software systems. Parents--and not the spyware state--should protect their children. The government is neither your parent nor your god nor your savior and the people should send a clear message stating that.
California, stay out of my operating system! And stay the hell away from children!
@eff@mastodon.social
@linuxfoundation@social.lfx.dev
@fsf@hostux.social
@osi@opensource.org
@conservancy@sfconservancy.org
#AgeVerification #Linux #EFF #OSI #LinuxFoundation #FSF #Privacy #Cybersecurity #Surveillance #Spyware #OpenSource #OperatingSystems #FreeSoftware #SoftwareFreedom #Panopticon #BigBrother #Government
CC: @laffer1@bsd.network @leo@twit.social @MichaelRoss@social.linux.pizza @rms@mastodon.xyz @thenewoil@mastodon.thenewoil.org @TechDesk@flipboard.social @remixtures@tldr.nettime.org

Alt...
A crowd of sillouettes of people stands in front of a giant telescreen depicting a single giant eye watching them.

The EC is working on more detailed guidance about how the CRA will work in practice. After lots of input from many of our open source colleagues, they have issued a draft. There are substantial improvements to the guidance around open source.
The EC has opened a 4-week public comment period on this new document, it would be a good time to read it and comment, if you haven't.
Delta Chat is a messaging platform that works over email.
Setup is similar to a email client.
Messaging is decentralized and interoperable.
Supports end-to-end encryption via PGP.
PGP encryption keys are created automatically.
Default desktop client is based on Electron.
Electron is based on the Google Chromium web browser.
Website: https://delta.chat
Mastodon: @delta
#DeltaChat #Messaging #Privacy #InfoSec #E2EE #OpenPGP #PGP #OpenSource #FOSS #CyberSecurity #Encryption #FreeSoftware
Alt...
Delta Chat logo.

I built pagevault, a tool that turns any file into a self-contained encrypted HTML page. PDFs, images, whole websites, encrypted into a single .html you can email or host anywhere. Decrypts in the browser via Web Crypto API, no backend needed.
Chunked encryption handles 100+ MB files without choking the browser. Each chunk gets its own script tag, decrypted sequentially, then removed from the DOM for GC.
Cryptomator is a client-side encryption tool for cloud storage services.
Data protected via AES-256 encryption.
Individual and business features.
Managed and self-hosted options.
ENCRYPTED
File content.
File/Folder name.
NOT ENCRYPTED
File/Folder access/creation/modification timestamp.
Number of files/folders in a folder/vault.
File size.
Website: https://cryptomator.org
Mastodon: @cryptomator
#Cryptomator #Encryption #InfoSec #Privacy #CyberSecurity #FreeSoftware #FOSS #FLOSS #OpenSource
Alt...
Cryptomator logo.
hat.sh lets you encrypt files locally in your browser using modern cryptography — nothing is uploaded or stored.
Perfect for securing files before sharing or using cloud storage. Open-source and self-hostable.
👉 https://github.com/sh-dv/hat.sh
👉 More tools like this : https://digital-escape-tools-phi.vercel.app/
#Privacy #Encryption #OpenSource #SelfHosting #DigitalSecurity

NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @crypto@a.gup.pe @infosec@a.gup.pe @selfhosting@a.gup.pe

Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.
NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @crypto@a.gup.pe @infosec@a.gup.pe

Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.
NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @usenet@lemmy.world @crypto@a.gup.pe @infosec@a.gup.pe
Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.