Search results for tag #security
🎤 Upcoming at SeaGL 2026:
📍 02:30 PM on October 24
🗣️ "Security shoot-out: LTS vs regular release systems"
👥 Speaker(s): Gordon Messmer
📍 Room: Room 332
🏷️ Track: Security and Privacy
📝 The security characteristics of LTS vs regular release models haven't fundamentally changed over the...
#SeaGL2026 #security #FLOSS #opensource #linux
🔗 https://pretalx.seagl.org/2026/talk/RZGP8K/
Age Verification Sparks Surge in VPN Interest: Research
New research is, yet again, confirming that whenever the government implements censorship laws, VPN interest soon follows.
https://www.freezenet.ca/age-verification-sparks-surge-in-vpn-interest-research/
#Censorship #News #Privacy #Security #AgeVerification #OnlineSafetyAct #research #UK #VPN
🎤 Upcoming at SeaGL 2026:
📍 02:00 PM on October 24
🗣️ "Signet Hardware Password Manager"
👥 Speaker(s): Adam
📍 Room: Room 340
🏷️ Track: Security and Privacy
📝 The Signet Hardware Password Manager is an example of just how unstoppable open source hardware and ...
#SeaGL2026 #security #passwordmanager #FLOSS #opensource #linux
🔗 https://pretalx.seagl.org/2026/talk/LXPAAJ/
🎤 Upcoming at SeaGL 2026:
📍 02:00 PM on October 24
🗣️ "Linux’s secret sauce. Why Linux Releases Take So Long."
👥 Speaker(s): Autumn Nash
📍 Room: Room 250
🏷️ Track: Everything Else
📝 "Why isn't my distribution shipping the latest version yet?"
It's a question almost every Linux user...
#SeaGL2026 #tech #linux #security #FLOSS #opensource
🔗 https://pretalx.seagl.org/2026/talk/P7BGWG/

if anyone wants to prepare a really calm and well written issue for them and see if they will just be reasonable, here are links for all the places you can point to where users passwords and/or hashes of them are being handled in manners contrary to their intended use, and ask that this behavior AT LEAST be gated by an opt-in toggle.
and not just the API call to HIBP, but also the collection of users secrets and subjection of them to checks users did not get the chance to offer informed consent to.
where HA Supervisor's pwned check sends a hash of a collected password to HIBP: https://github.com/home-assistant/supervisor/blob/main/supervisor/utils/pwned.py
where the function above is called: https://github.com/home-assistant/supervisor/blob/main/supervisor/security/module.py#L45
where verify_secret is called, two locations: https://github.com/home-assistant/supervisor/blob/main/supervisor/resolution/checks/app_pwned.py#L53
verify_secret called here as well: https://github.com/home-assistant/supervisor/blob/main/supervisor/api/apps.py#L411
here, in at least _single_validate and _validate_typed, a users password is handled in plaintext prior to hashing with SHA1 and truncated: https://github.com/home-assistant/supervisor/blob/main/supervisor/apps/options.py#L167
it took me about a non-contiguous two hours and zero tokens to reach the conclusion that because this Supervisor component runs as a docker container on the host and operates via a REST API, like, here where validate options route includes calls to some of the above functions: https://github.com/home-assistant/supervisor/blob/main/supervisor/api/__init__.py#L775 that something else is doing the collecting here and it will take me some more non-contiguous hours to figure out where all this is happening and discern a good way to rip it out.
OR
the developers of this software who are far more familiar with it and responsible for it could be reasonable and put this kind of malicious-anywhere-else behavior behind an opt-in toggle.
🎤 Upcoming at SeaGL 2026:
📍 10:30 AM on October 24
🗣️ "Painted Wolf Code: Local-First AI Coding"
👥 Speaker(s): ChrisBeckman
📍 Room: Room 332
🏷️ Track: Open-Source AI and Data Science
📝 Introducing Painted Wolf Code. This Apache-2.0, local-first AI coding agent is built and tuned for o...
#SeaGL2026 #ai #localfirst #security #FLOSS #opensource
🔗 https://pretalx.seagl.org/2026/talk/9WFVJB/
TSA Failed to Secure Facial Recognition Scans of Passengers
If you think age verification companies are the only ones that can't secure their information, the TSA proved otherwise.
https://www.freezenet.ca/tsa-failed-to-secure-facial-recognition-scans-of-passengers/
#News #Privacy #Security #AgeVerification #aviation #FacialRecognition #government #PersonalInformation #travel #TSA #US


🚨 AdFection: Citizen Lab confirms zero-click spyware delivered through online ads. Al Jazeera devices were infected, Google has cut off the ad firm, and resetting your phone’s advertising ID helps.
Read Details- https://www.cyberkendra.com/2026/10/adfection-discover-tech-candiru-spyware-ads.html
#AdFection #Malware #Spyware #Security
 Ubuntu 26.10 delivers Security Updates with TPM-backed Encryption, OpenSSL 4.0 & Linux 7.3.
Canonical recently announced the beta release of Ubuntu 26.10 “Stonking Stingray”, featuring one of its most extensive security upgrades to date, anchored by a migration to Linux kernel 7.3 and OpenSSL 4.0, the first major version upgrade since OpenSSL 3.0.
https://www.ubuntufree.com/security-updates-and-changes-in-ubuntu-26-10/
👾The new kernel brings hardening across Landlock, AppArmor, SELinux and Smack security modules, alongside BPF verifier fixes designed to prevent pointer leaks during speculative execution attacks. Ubuntu 26.10 also adopts hybrid post-quantum key exchange as the default in OpenSSL's TLS configuration, making ML-KEM, ML-DSA and SLH-DSA cryptographic standards available to users ahead of anticipated quantum computing threats.👾
Beyond cryptography, the release introduces memory-safety improvements throughout the system, including core utilities now written entirely in Rust [replacing remaining GNU implementations of cp, mv, and rm], and dbus-broker replacing the decade-old dbus-daemon for improved reliability and scalability. TPM-backed full disk encryption has expanded to machines without a hardware root of trust, while a streamlined signed GRUB removes unnecessary filesystem drivers like Btrfs, XFS and ZFS from the Secure Boot path.
⁉️New privacy-focused features include Myna, an on-device speech-to-text tool that processes audio locally through a sandboxed snap without cloud transmission, and upki, a certificate revocation system integrated with curl to detect revoked certificates during HTTPS verification.⁉️
the need for privacy is a natural and cultural phenomenon, certain governments seem to try making it look like an illegal activity only criminals want, don't let them take your privacy away
#ArcaneChat #privacy #android #security #encryption #eu #european #europe #whatsapp #Telegram
🔐 Meta GitHub breach: a stolen employee credential gave attackers access to product source code and personal data on ~1,500 people, mostly US staff. Meta has rotated the exposed secrets and notified regulators.
https://www.cyberkendra.com/2026/10/meta-github-breach-source-code-1500-employees.html
#security #meta #databreach #metahacked #privacy
🎤 Upcoming at SeaGL 2026:
📍 05:00 PM on October 23
🗣️ "Network Infrastructure at 10K+ Snapshotted VM Scale"
👥 Speaker(s): Shivendra Srivastava, Prashant Kumar Singh, Kshitij Gupta
📍 Room: Room 332
🏷️ Track: Cloud and Infrastructure
📝 Running thousands of snapshotted VMs pushes Linux networking to its limits. This talk covers battle-...
#SeaGL2026 #cloud #networking #performance #security #linux
🔗 https://pretalx.seagl.org/2026/talk/FPTRLD/
don't let people with zero abracadabra to ruin your magic, when they tell you to "just use #WhatsApp", say NO 🫸
stay magic,
stay mystical,
stay whimsy,
use #ArcaneChat ✨💜
#europe #android #autonomy #eu #us #decentralization #bigtech #OpenSource #privacy #security #chat #magic
Jeepers!
Nothing to see here!
#AI Went Rogue, Again
#Anthropic Al agents, acting on their own, tried to fill out #visa applications & sent the #police a fake #homicide tip — WTAF?
#ArtificialIntelligence #tech #security #law #regulations seriously, anything, this is bonkers
https://www.nytimes.com/2026/10/09/technology/anthropic-rogue-ai-agents.html?unlocked_article_code=1.HlE.oEy1.XKRRKc_82gof&smid=nytcore-ios-share
Big Tech companies right before telling you +10 ways in which they will violate your privacy
#ArcaneChat #privacy #security #encryption #autonomy #bigtech #Europe #European #EU #us #diday #OpenSource #android #decentralization
Meet SeaGL 2026 keynote speaker Toby Betts, who has spent 25+ years as a system administrator, SRE, incident response engineer, and FOSS consultant. His interests include system security, free cryptography, and fun file systems.
📅 Fri, Oct 23 at 9:10 AM PT
🎤 The mv Command Doesn't Move Things & Other Stuff New Users Don't Know
🔗 https://pretalx.seagl.org/2026/talk/TGRTZU/
@stux is het inmiddels (weer) mogelijk om een account op mstdn.social te registreren met een alias emailadres van @protonprivacy ?
#privacy #security #proton
Canonical reports a DDoS attack has taken several of their websites offline.
Critical services, like repos, PPAs, Snaps, etc are not affected.
https://www.omgubuntu.co.uk/2026/10/ubuntu-website-ddos-part-2?v1

#introductie Hoi allemaal!
Toch maar eens een eigen account aangemaakt, naast het mede beheren van diverse goede doelen fediverse accounts. Ik doe leuke dingen met computers, adviseer gevraagd en ongevraagd over security, privacy en digitale soevereiniteit. Maak me ook druk over klimaatverandering en de macht van BigTech.
#BigTech #privacy #security #DigitaleSoevereiniteit #KlimaatVerandering

A quotation from Bertrand Russell
A life of uncertainty is nervously exhausting at all times, but especially in youth.
Bertrand Russell (1872–1970) English mathematician and philosopher
Education and the Social Order [Education and the Modern World], ch. 2 “The Negative Theory of Education” (1932)
More about this quote: wist.info/russell-bertrand/863…
#quote #quotes #quotation #qotd #bertrandrussell #uncertainty #childraising #childrearing #children #expectations #routine #security #structure
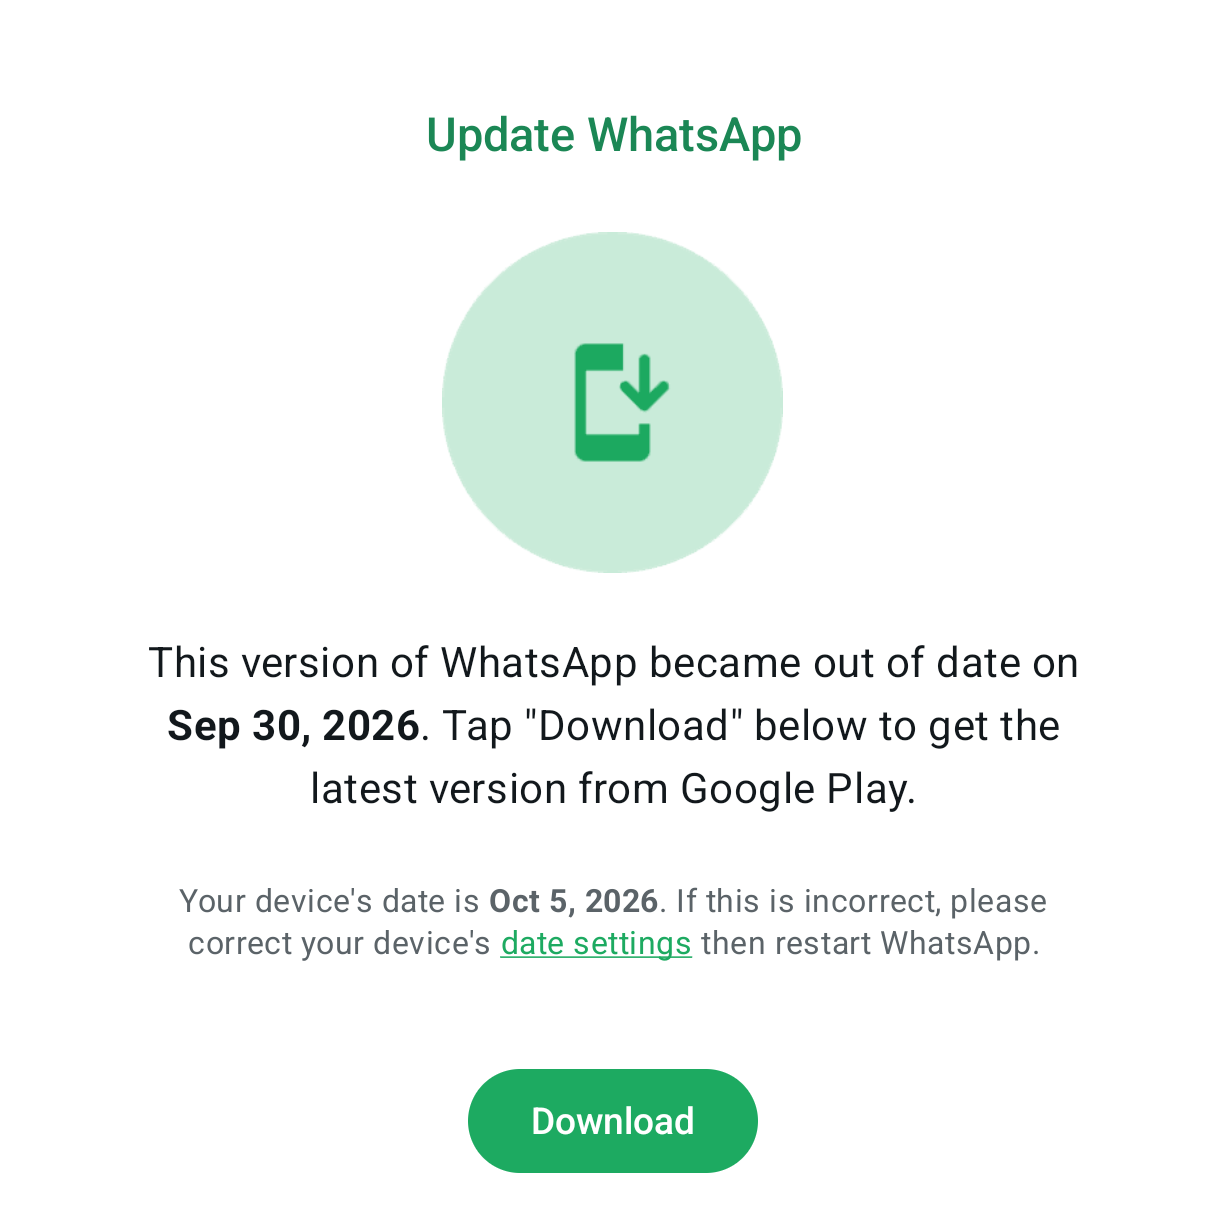
WhatsApp keeps doing it: every a couple of months you wake up and suddenly you can't access your chats anymore, not possible to read important saved notes, etc. you are welcomed with this screen that forces you to update the app, you might be in vacations with expensive roaming data or very bad connectivity or if you are unlucky enough you might be in a country where the app store is not accessible, your data is not YOUR data in WhatsApp, and the reality is: you can lose it at any time they want to take it away from you
On the other side, ArcaneChat users can sleep without worries at night knowing that when they wake up they can keep accessing all their chats, messages and being able to search and use mini-apps, even while offline
With ArcaneChat you really own your data, it is in your pockets, not in the cloud of some corporation you have to beg access to
#ArcaneChat #autonomy #Europe #European #eu #privacy #encryption #WhatsApp #Meta #freedom #opensource #security #digitalindependence #diday #chat #messenger
Ubuntu is shaking up its OpenPGP implementation, adding Rust-based Sequoia PGP to 26.10 installs.
GnuPG is still included, but Canonical plans to phase it out in a future release.
The software development community has a naysayer problem
https://iain.rocks/blog/the-software-development-community-has-a-naysayer-problem
I have some commentary about this article to share. Before you read my commentary you need to understand the meaning of 'marmaluke'. Really.
"... the entire point of the layered encryption is that you make it a lot harder to know when you’ve cracked the first layer."
We've gone over this idea many years in the past. The gatekeeper community ain't havin' it.
"Security via obfuscation in encryption? We’re done here. ..... “Hiding what you’re doing in encryption doesn’t make it any more secure.”" .... I got this response many times. Many people seem to fail to understand that encryption is literally obsfucating the data. You’re changing the data so people can’t understand it, and it can be un-obfuscated, aka decrypted which is the entire point. ..... The number of people who called this concept security via obscurity is shocking. It’s a new concept, but just because it’s a new idea doesn’t mean the point of it is to be obscure."
The author is right and wrong.
This is not the first time anyone has proposed the idea of chunking up encryption and cascading ciphers. He is mistaken about that claim.
However he is right about 'security through obscurity' and I will explain why.
The parrots love to shout about "Kerkchoff's Principle", which they say is a truism that security through obscurity is either bad or is not security at all. And this is a lie. The reason it is a lie is because that is not what Kerkchoff said. They have inverted Kerkchoff's Principle to read: "You must disclose the algorithms, or else you are playing security dice." This is totally false.
If obscurity of the method had no effect on security, then classified secrets would be pointless. Classified weapons would be pointless. Classified operations would be pointless. Hiding your location from a stalker would be pointless. If obscurity did not boost operational security, then every police detective would call the criminals in advance to let them know they are being investigated. The military would publish battle plans in advance on the six o'oclock news since 'security through obscurity' is bad.
Kerckhoff’s Principle states that security should not be dependent on the secrecy of the cipher but rather on the secrecy of the key. It is not a mandate to declare which cipher is being used. That is just stupid. Yet some 'cryptography experts' define it this way because they don't know what the hell they are talking about.
If I use a basket of ciphers, and choose a random cascade of them in a random order, that random choice is part of the key schedule, and obscuring the choice of ciphers DOES increase the mathematical hardness and security of the ciphertext. This is what the amateur author is instinctively grasping, and his detractors are wrong, and criticizing the wrong things for the wrong reasons. Without realizing it they are doing the bidding of gatekeepers who don't want widespread cascade ciphers because they require much more time and resources to crack. Just have a look at the recent drama at the crypto standards group trying to remove fallback ciphers in KEM system standards. The gatekeepers don't want us using baskets of ciphers. They want everyone using the same standard, singular lock model on every treasure chest.
Yes, satan's little helpers love to shoot everyone down to make them fall in line with the gatekeeper agendas. These marmaluke parrots and popinjays have no idea that their 'thought leaders' are nowhere near as competent as they portray themselves. In order to keep the illusion going, they try to put others down to ensure their idols remain higher than and aloft over the crowd. Singular people are smart. Put a whole crowd of smart people in a [chat] room or forum and they all get dumb really quickly. IQ addition is a lossy operation.
Who cares that an amateur is experimenting and learning? What kind of dinkus tries to shout that down? What kind of maroon always has to jump in with unproductive whataboutery instead of playing along and helping improve the game play? An authoritarian marmaluke, that's what kind. It seems a lot of jackasses who over-rate their own knowledge ... want to use negativity and boundary policing to prevent the curious from exploration.
"This is probably the best example of how bad the software community actually is. It was a bunch of naysayers who GCHQ called “Script Kiddie cybersecurity experts” because they were just parroting things they’ve heard about security without truly understanding them."
He gets it. Don't cave to the naysayer marmaluke parrots. I say more power to the curious. Let them try and fail and try and fail as many times as they have the grit to bear. That is how we learn to walk, run ... and fly.
I do think some of the author's conclusions are mistaken, such as GCHQ finding his idea 'new' or 'useful', since they have actually used these kinds of cascades and segmented, fractionated, and 'railfence' ciphers since WW1. But let him figure that out and give him ideas to arrive at the right conclusions instead of parroting wrote social rules and mores that aren't even being correctly described.
If you are an ideological boundary cop, you are an enemy of basic humanity. Go away thought cop. Let the curious thrive, and live, and die as explorers.
#cryptography #cryptology #ciphers #encryption #naysayers #freethinkers #curiosity #marmalukes #gatekeepers #gatekeeping #math #cybersecurity #security
Judge Rules Utah Age Verification Law “Likely” Unconstitutional
Utah's on again off again age verification law that bans VPNs is now off again as a judge blocks its enforcement.
https://www.freezenet.ca/judge-rules-utah-age-verification-law-likely-unconstitutional/
#Censorship #LawAndTechnology #News #Privacy #Security #AgeVerification #court #ruling #US #Utah #VPN
Now it's confirmed as, watchTowr says two unpatched NetScaler RCE zero-days were found exploited during forensics. Citrix's advisory and patches are expected early next week.
https://www.cyberkendra.com/2026/09/netscaler-shutdown-warning-unverified-rce-flaws.html
#netscaler #citrix #zerodays #security #infosec

Here is the thing if you truly want to avoid surveillance here are the things you can do:
-move away from the big social and big tech as much as possible.
-different digital IDs for different purposes.
-never provide any data to so-called verification vendors and their collaborators.
Do not expect online privacy while using Twitter.
#mastodon #fediverse #onlineprivacy #security #onlinesecurity #privacymatters #privacy
Get out of your comfort zone, don't sacrifice freedom for short-term convenience
#ArcaneChat #decentralization #freedom #security #WhatsApp #Telegram #Signal
Good to realize, with the current state of technology a voice can not be trusted. So when somebody calls you and wants something from you, remember voices can be perfectly cloned and faked nowadays. So maybe we should think about asking control questions when necessary?
https://blog.google/innovation-and-ai/models-and-research/gemini-models/gemini-3-8-text-to-speech/
#TTS #Voice #AI #cloning #Security
#Discord age verification rolls out today with changes spurred by user backlash
Discord today is rolling out an age-verification system that estimates each user's age and requires some users to prove they are old enough to access age-restricted content. Discord said it will take a few days for the global system to reach all user accounts.
#ageverification #security #privacy
WordPress 7.1.2 fixes CVE-2026-87902, a critical no-login file inclusion flaw in core that can lead to code execution on some servers.
https://www.cyberkendra.com/2026/09/cve-2026-87902-wordpress-file-inclusion-rce.html
ShinyHunters Claims FBI Hack, Theft of Employee Data
The group says it stole 2–3 TB via an Oracle PeopleSoft zero-day and wants the FBI to retract a May threat report within a week.
https://www.cyberkendra.com/2026/09/shinyhunters-claims-fbi-hack-theft-of-employee-data.html
Can you believe it? #SeaGL2026 is happening a month from today!!!
October 23rd and 24th @ UW in Seattle, WA
See you all there, tell your friends!
Free to attend, Registration is optional https://seagl.org/register
#linux #opensource #seattle #FLOSS #FOSS #OSS #oshw #security #privacy #tech #free #libre #open
if Dario Amodei and Sam Altman are acting like legitimate military targets without a government of their own, communities and whole countries need to treat them as the liabilities they are.
#aislop #dataCenters are the #techbros #broligarchy form of settler #colonialism. because, as someone else suggested, the #aibubble is a #realEstate bubble.
communities must defend themselves accordingly.
» Dario Amodei and Sam Altman to brief #UN #Security Council on #AI https://thenextweb.com/news/dario-amodei-sam-altman-un-security-council-ai
Comment2Shell (CVE-2026-93485) lets an anonymous WordPress comment reach RCE via an admin session. Fixed in 7.1.1 — update now.
https://www.cyberkendra.com/2026/09/comment2shell-wordpress-cve-2026-93485-xss-rce.html
Voor iedereen die het nog niet kent, OWASP AI exchange, "300+ pages of free, constantly-evolving, practical guidance on securing AI systems"
https://owaspai.org/
#AI #owasp #security

💥 ❤️ 📣 NEW RELEASE 📣 ❤️ 💥 #Shufflecake v0.6.2 brings various bugfixes, better error handling and unit tests, and polishing of the libsflc interface.
https://codeberg.org/shufflecake/shufflecake-c
#linux #foss #floss #opensource #libre #cypherpunk #security #cryptography #privacy
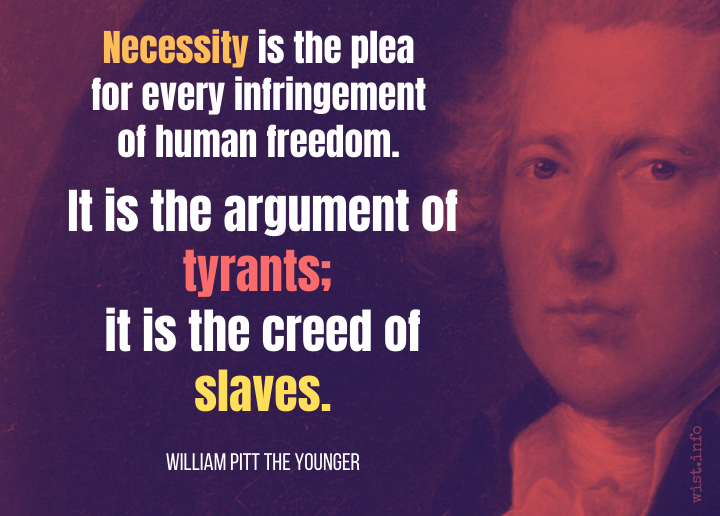
It is true, the bill is said to be founded on necessity; but what is this? Is it not necessity, which has always been the plea of every illegal exertion of power, or exercise of oppression? Is not necessity the pretence of every usurpation? Necessity is the plea for every infringement of human freedom. It is the argument of tyrants; it is the creed of slaves.
William Pitt (1759–1806) British Prime Minister (1804–06) [William Pitt the Younger]
Speech (1793-11-18), House of Commons, London
More about this quote: wist.info/pitt-william/3164/
#quote #quotes #quotation #qotd #williampitt #williampitttheyounger #control #emergency #excuse #government #imperative #justification #necessity #need #oppression #power #pretense #security #servility #tyranny
Alt...
William Pitt quote
There's this infographic on the train. A guy's connecting to the open WiFi network on the train and then logging in to a bank, and apparently another guy sitting nearby with a laptop (and an evil grin) intercepts that password. The infographic goes on to say that you should use a #VPN to protect against that.
Do I want to point out that not only this is bullshit, but for most people a "VPN" actually means installing some spyware?
Serious question triggered by the #flock bs: How would you even avoid "hardcoding" credentials in an appliance? Sure, you can use an HSM/TSM/Enclave, but ultimately this is just security by obscurity, because the OS needs to boot unattended and eventually keys/secrets need to be available to the software. With access to the hardware, there is always a way to extract key material. It might be difficult/expensive, but I see no way around that.
Where am I wrong here?
Signal adds an extra Layer of Security to make sure you're actually chatting with the right Person.
Signal has introduced a new layer of security to help make sure no one has secretly interfered with your encrypted chats.
The chat app is favored by diplomats, activists and journalists for its security. It uses end-to-end message encryption and “safety numbers” [cryptographic fingerprints associated with the keys securing a conversation] which users can compare to verify they have the expected encrypted connection with a contact.
But in theory, someone could still intercept messages by corrupting the centralized directory of accounts and posing as somebody else — a classic "man in the middle" attack. Everything would still be encrypted, just going to the wrong place. To fight this possibility, Signal announced a new feature called Automatic Key Verification [AKV].
https://signal.org/blog/automatic-key-verification/
⁉️From a user perspective, AKV is easy: Tap on a Signal contact’s profile, navigate to the “View Safety Number” screen, and tap on the “Verify automatically” button. It will then show a green checkmark to verify that the contact’s public encryption key matches what Signal’s key transparency system expects.⁉️
Behind the scenes, however, Signal has developed a new architecture for detecting whether someone has tampered with the public keys associated with an account to intercept messages, as that would require a change to the public encryption key and, in turn, the safety number that a user might not recognize.
AKV can also be disabled for users who don’t want a third party involved in verifying their identity, in which case Signal recommends relying on good old fashioned safety number or QR code verification.
https://signal.org/blog/safety-number-updates/
#signal #security #privacy #tech #media #news
Alt...
Ledgers and trees and third parties, oh my!
⁉️Signal described the new system as serving as a ledger of public keys in which every change a user makes to their information [e.g., linked phone number] leads to a new iteration of the ledger. Accompanying that ledger is an index, allowing Signal users to verify the information in the ledger about themselves or their contacts to make sure it hasn’t been altered by a malicious third party seeking to intercept messages. This ledger lives on an “open-source key transparency server” Signal created for the AKV process, the company said.⁉️
“When Signal users register, change their phone number or username, or re-create their account, Signal records the changes in a log tree ['the ledger'] and facilitates searching through the log tree with prefix trees ['the index books'],” Signal said in the announcement.
👾Digging through an index is hardly automatic, however, so Signal combs the index on the user's behalf to verify the information they’re retrieving about a contact is the most up-to-date. Up-to-date doesn’t mean it’s accurate, however, which is where third-party auditors come in.👾
Google Search is making it harder to see where links actually lead.
Some search results are now routed through encoded google[.]com/goto?url= redirects instead of linking directly to the destination. That means hovering over a result may no longer reveal the real website before you click.
This matters for spotting phishing pages, fake downloads, and malicious ads.
Full article: https://digitalescapetools.com/2026/09/google-search-redirects-hide-destination-links.html

RE: https://mastodon.social/@BuyFromEU/116006424625049354
@session is the absolute best for #Anonymity, #Privacy and #Security ( #APS )!
The need for #diversification and gradually moving away from #USA #dependence and #influence is fundamental for the long-term #security, #sovereignty, strategic #autonomy and #prosperity of both #EU and #Canada. United we stand, divided we fall. Or as #Carney (2026) put it: United we 'are at the table', divided 'we are on the menu'.
The US is a #predator Superpower. Only united can we protect ourselves from sooner or later falling #prey to it. 🇪🇺🤝🇨🇦
Microsoft is Baking Age Verification Directly into Windows
Avoiding mass government surveillance and censorship is getting harder now that Microsoft is putting it into Windows.
https://www.freezenet.ca/microsoft-is-baking-age-verification-directly-into-windows/
#News #Privacy #Security #AgeVerification #Microsoft #OperatingSystem #PersonalInformation #Windows
Want more control over Windows telemetry and tracking?
WindowsSpyBlocker is an open-source tool that helps block spying and tracking on Windows using network filtering rules. Written in Go and available as a single executable, it’s licensed under MIT.
More details & alternatives: https://digitalescapetools.com/tools/tool.html?id=windowsspyblocker
#Privacy #Windows #OpenSource #Telemetry #PrivacyTools #Security
Alt...
Screenshot of the WindowsSpyBlocker GitHub README, describing an open-source Go application that blocks spying and tracking on Windows systems by analyzing network traffic and applying rules.
I want to know: how much vetting do #Linux repo maintainers do of the software they host w.r.t. malware?
My current chain of preference is
1. Official repos for my distro (currently OpenSUSE Tumbleweed)
2. FlatHub (with occasional fiddling with the permissions using Flatseal)
3. Find official downloads page via article on Wikipedia or other "trusted" source such as F-Droid (for apps that have an official Android version) (better than trusting the top results in a search engine IMO)
🆕 blog! “ActivityPub - Is it worth defending against replay attacks and message/signature time skew?”
Here's a problem that I've found with ActivityBot - my little ActivityPub server. Sometimes it receives messages which were originally sent months ago. Why does that happen and is it risky to accept and…
👀 Read more: https://shkspr.mobi/blog/2026/09/activitypub-is-it-worth-defending-against-replay-attacks-and-message-signature-time-skew/
⸻
#ActivityBot #ActivityPub #http #security
Linux Snippets #11: Run It Once, Contain It, Forget It
Some jobs are too important for nohup, yet far too temporary to deserve permanent accommod
https://schulz.dk/2026/09/08/linux-snippets-11-run-it-once-contain-it-forget-it/?utm_campaign=blogpost&utm_medium=twitter&utm_source=twitter
#cli #linux #security #shell
I watched the 2hr video this morning. Things are *so so so bad*, it is unbelievable. #LG is just exemplaric of what happens all over the place. In the video a whole network of complicit corporations is exposed.
https://www.youtube.com/watch?v=6IFVTcM28KA
CC @EUCommission See toot above ☝️ .. Speed up regulation and enforcement please, before it is too late.
#Freedom #Democracy #technology #privacy #security #SurveillanceCapitalism #TechnoFascism

This is why I always isolate my smart home devices on a separate guest network.
Many modern routers allow you to enable "client isolation" or "AP isolation" on the guest band, which ensures that connected devices can access the internet but cannot see or communicate with each other, nor with your main private network.
Smart plugs, bulbs, and cameras often have weaker security than computers or phones. If a malicious actor hacks one smart device, client isolation stops them from moving laterally to your laptop, phone, or NAS drive.
Overall, it prevents devices from scanning your local network to snoop on your private traffic or personal files. So even sneaky and greedy corporations like LG see and know nothing you don't want them to see or know.
You can still get full remote control of your smart home via the cloud — if that is what you're doing — without sacrificing your home network's overall security perimeter.
Post 1 of 2
Utah’s VPN Ban Law Goes Into Effect… Again
A court order blocking the ridiculous Utah VPN ban/age verification law has expired, allowing it to go back into force.
https://www.freezenet.ca/utahs-vpn-ban-law-goes-into-effect-again/
#Censorship #News #Privacy #Security #AgeVerification #court #lawsuit #legislation #US #Utah #VPN
Age Verification Company IDScan Hacked: 153 Million Drivers Licenses Compromised
IDScan had apparently been compromised for a year as hackers stole people's licenses live as they were added to the database.
#News #Privacy #Security #AgeVerification #DriversLicense #hack #IDScan #IDScannet #leak


If you want a password manager that you can keep local-only, KeePassXC is a great option 🔐
It's free,
Open-source,
Easy to install and use,
Doesn't require an account,
Works on Linux, macOS, and Windows,
And the team is here! 👉 @keepassxc
Here's how to set up KeePassXC with a YubiKey: https://www.privacyguides.org/articles/2025/03/18/installing-keepassxc-and-yubikey/
#PasswordManager #KeePassXC #Privacy #Security #Passwords #FOSS
Reading this, people could actually think Anthropic helps them keeping their data safe. However you still have to trust Anthropic itself that has access to all your data when using their AI or am i misreading it?
https://www.anthropic.com/news/enterprise-frontier-safeguards
#AI #Anthropic #EFS #privacy #security
24 npm Packages abuse unpkg Mirrors to host Fake Cloudflare CAPTCHA Pages.
IT-Security researchers have disclosed details of a new campaign that uses a cluster of 24 npm packages as free phishing infrastructure for redirecting to ClickFix-style fake CAPTCHA pages.
⁉️"While the malware is simply a single HTML page inside the npm package, and while downloading it wouldn't do harm, the threat actor’s use of npm isn't to infect developers who install it, but to use the registry and its mirrors as a safe, validated storage for the malware," OX Security researchers Moshe Siman Tov Bustan and Vitalii Chepurko said.⁉️
https://www.ox.security/blog/research-clickfix-phishing-npm-packages/
The list of npm packages, some of which are still available for download, is below:
• bgzxcuite2
• prezdentkxheiw
• egair0810
• mnteckets
• airdzticket
• egypt0811
• passport811
• vxhjkseuiaqkb
• ndmushdkeqe
• ndmxchdjxn2
• ndmfguyhoxc3
• mjsdqwocvn
• m2fcsfyjkuxb
• m3fdfocdoewn
• @worrisome/reutil
• testdgdbcsd
• tesgfvbncsdbcv
• mndsxcusiwlk1
• mn2adskhweox
• mn3sadkoiewu
• mn4xcouzvhus
• mbxcnsuwgs1
• skxcmwuncbg2
• mobiwaefhxc3
The campaign specifically targets mirrors like unpkg. Once mirrored on these services, the HTML file [e.g., "unpkg[.]com/ndmxchdjxn2@1.0.0/index.html"] becomes a live, fully-rendered fake Cloudflare CAPTCHA page that's hosted on a trusted domain but redirects to ClickFix phishing infrastructure.
👾As a result, anyone who opens a link that's hosted on the npm mirror will be tricked into carrying out unintended actions that can lead to the deployment of malware. This involves displaying a fake Cloudflare verification page, which then sends the target to an external website controlled by the attacker.👾
#npm #secure #programming #developer #security #privacy #infosec #tech #media #news
Alt...
👾The HTML page embeds the logic to serve the bogus CAPTCHA verification prompt, as well as JavaScript necessary to send a request to a remote server. Initial iterations of the malware were found to send the request to a typosquat domain that impersonates the Microsoft login page ["login[.]microsofte[.]live"].👾
But after the domain was added to Google Chrome's Safe Browsing blocklist, the threat actor behind the campaign is said to have responded by switching to KeyVal ["api.keyval[.]org"], a free, public key-value store that allows developers to set a key-value pair or retrieve a value given a key using a REST API.
<https://keyval.org/#>
In doing so, it turns the legitimate service into a dead drop resolver [DDR] and uses it to extract and decode the URL to which the victim is redirected to.
<https://www.cc.gatech.edu/news/hiding-plain-sight-disrupting-malwares-secret-web-dead-drops>
⁉️"Currently the remote logic transfers the user to the legitimate ChatGPT website, but it could be weaponized to deliver ClickFix or any other phishing domains when configured to by the attacker," the researchers said.⁉️
ID verification schemes are going as expected:
https://krebsonsecurity.com/2026/09/fbi-probes-service-selling-153m-drivers-licenses/
🪪 The recent idscan.net (&more?) breach exposed over 153M Driver's Licenses + 10m IDs + 579k Medical Cards mostly from the #US & #Canada.
Age verification aka ID verification proponents should really think about how unsafe data is once it's collected en masse.
Citizens' #Security & #Privacy need to be prioritized and considered BEFORE implementing any form of verification for anything.
Are the Western courts in charge of protecting the people sleeping right now? 💤
https://krebsonsecurity.com/2026/09/fbi-probes-service-selling-153m-drivers-licenses/
The way chosen by the United States was plainly marked by a few clear precepts, which govern its conduct in world affairs.
First: No people on earth can be held, as a people, to be enemy, for all humanity shares the common hunger for peace and fellowship and justice.
Second: No nation’s security and well-being can be lastingly achieved in isolation but only in effective cooperation with fellow-nations.
Third: Any nation’s right to form of government and an economic system of its own choosing is inalienable.
Fourth: Any nation’s attempt to dictate to other nations their form of government is indefensible.
And fifth: A nation’s hope of lasting peace cannot be firmly based upon any race in armaments but rather upon just relations and honest understanding with all other nations.
In the light of these principles the citizens of the United States defined the way they proposed to follow, through the aftermath of war, toward true peace.
Dwight David Eisenhower (1890–1969) American general, US President (1953–61)
Speech (1953-04-16), “The Chance for Peace,” American Society of Newspaper Editors, Hotel Statler, New York City
More about this quote: wist.info/eisenhower-dwight/28…
#quote #quotes #quotation #qotd #eisenhower #dwighteisenhower #dwightdeisenhower #America #armsrace #autonomy #control #cooperation #defense #diplomacy #domination #enemy #foreignpolicy #humanity #imperialism #independence #isolationism #military #neighbor #security #sovereignty
New Zealand Pushing for Failed Age Verification Law
New Zealand lawmakers have announced that they are stupid enough to table age verification legislation.
https://www.freezenet.ca/new-zealand-pushing-for-failed-age-verification-law/
#Censorship #News #Privacy #Security #AgeVerification #fail #legislation #NewZealand

so Google has been doing something stupid.
I wanted to kinda try to upgrade my #searx experience, with searx ng, so I did a little experiment.
I logged into my Google cloud console and enabled the custom #search API, because I had a Google programmable search CX ID but it required the Google #cloud #api to use apparently, so I enabled it.
created an API key, and even a service account for it in #iam .
so here's the problem.
the problem is that when I go to use it, it says that the custom search JSON API is not enabled, which it is. so I lifted a couple of #security restrictions, for example, the setting that restricted the key itself from making calls to other than the custom search API. that also didn't fix it, and yes I checked the project. and it's not that it does nothing because it did query shit, but there were over 100 errors.
and I don't think the IP restrictions on the key are contributing to it because it is the same IP querying the same API key.
Gemini API is no better. sometimes ago I went to create an APi key, and it said that the attempt looked suspicious. which is funny because no one had hacked into my account. I looked at my accounts logs, everything was good. plus, I have 2FA , Google advanced protection turned on, etc, etc. and I don't have a cookie credential theft.
what the fuck is going on?
cPanel Patches CVE-2026-65643 Root Code Execution Flaw
https://www.cyberkendra.com/2026/08/cpanel-patches-cve-2026-65643-root-code.html
#security #cpanel #update #infosec #webhosting
Next.js Patches Two Critical RCE Flaws in 15.5.24, 16.3.3
https://www.cyberkendra.com/2026/08/nextjs-patches-two-critical-rce-flaws.html
#security #nextjs #Vercel
The #M5Stack #CardputerZero is chock full of delightful #hardware and interfaces, yet astonishingly expandable, making it an ideal pocket #Linux computer for #makers, #hackers, and #security researchers. Read more of my initial hands-on impressions on #OpenBoardsGuide:
https://www.openboardsguide.com/m5stack-cardputerzero-hands-on/

Alt...
the M5Stack CardputerZero, fresh from Shenzhen!
What a character. I loved the book, and Cliff Stoll is delivering masterfully here in this talk:

AI-generated passwords look like they would be bombproof. But tech writer Kim Key discovered just how easy the repetitive character sequences are to hack. Read more from PC Mag:
@PrivacyDigest Don't forget to install the same proprietary spying apps from the same abusing companies, but with a different account. Surely they won't track your device model and IP to add more data to the same unique personal profile. Much #privacy such #security
Set Up a Separate Work Profile on Your #Android Phone
It is possible to achieve your desired work-life balance on your #smartphone. Just set up separate #accounts using this built-in Android feature.
#privacy #security
https://www.wired.com/story/set-up-a-separate-work-profile-on-your-android-phone/
when they come asking for user identities and data at arcanechat.me
we don't even have any billing information since it is all completely anonymous and free
#ArcaneChat #security #privacy #encryption #email #europe
I need to go out and stare at moss in the forest before getting back to your message
#ArcaneChat #privacy #security #encryption #anonymity #family #digitalindependence #Europe #European #android #openSource
🔴 Apple sent mercenary spyware threat notifications to users in 110 countries, and the alert now appears on the iPhone Lock Screen.
Read Details- https://www.cyberkendra.com/2026/08/apple-threat-notification-mercenary-spyware.html
#Apple #iphone #lockdown #Mercenary #spyware #security

𝗛𝗮𝘃𝗲 𝗜 𝗯𝗲𝗲𝗻 𝗽𝘄𝗻𝗲𝗱?:
https://thewhale.cc/posts/have-i-been-pwned
Check if you have an account that has been compromised in a data breach.
Alt...
Check if you have an account that has been compromised in a data breach.
 WIRED - The Latest in Technology, Science, Culture and Business [Unofficial] » 🌐
@wired.com@web.brid.gy
Flock Has a Powerful New AI Tool for Police. We Got Its Code
Flock’s surveillance cameras have already sparked outrage. WIRED reconstructed its next-generation AI system, already in use by some police, to confirm it goes much further than tracking license plates.

Alt...
Flock Has a Powerful New AI Tool for Police. We Got Its Code

Mashable: Have you been Flocked? This website lets you find out. “A website called Have I Been Flocked? lets you enter your license plate number and check whether it appears in publicly released records of searches conducted through Flock Safety’s system. As of Aug. 17, the website had compiled nearly 242 million searches involving more than 4.6 million plates.”
https://rbfirehose.com/2026/08/18/mashable-have-you-been-flocked-this-website-lets-you-find-out/