Search results for tag #cybersecurity
Cryptography on the web: the illusion of safety #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/cryptography-on-the-web-the-illusion-of-safety/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Trust without identity: hashes and signatures #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/trust-without-identity-hashes-and-signatures/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Fake IDs: uncovering inconsistencies #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/fake-ids-uncovering-inconsistencies/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Louis Pouzin and the datagram revolution #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/louis-pouzin-and-the-datagram-revolution/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog

Ever feel like online privacy is more than just clicking a button? 🤔 This short dives into why a VPN alone isn't enough – it's about rethinking your whole approach. Brisket and VPNs? Trust me, you'll want to know why. Check it out! 💻 #Cybersecurity #Privacy #VPNs
https://www.youtube.com/watch?v=0ScSF_0YRYQ
Alt...
🔴 LIVE
Behind Discord: Citron and Vishnevskiy #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/behind-discord-citron-and-vishnevskiy/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Privacy, surveillance, and the crypto wars #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/privacy-surveillance-and-the-crypto-wars/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Internet subcultures: kin communities #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/internet-subcultures-kin-communities/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
How ideas gain momentum online #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/influence-and-narrative-amplification-how-ideas-gain-momentum-online/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog

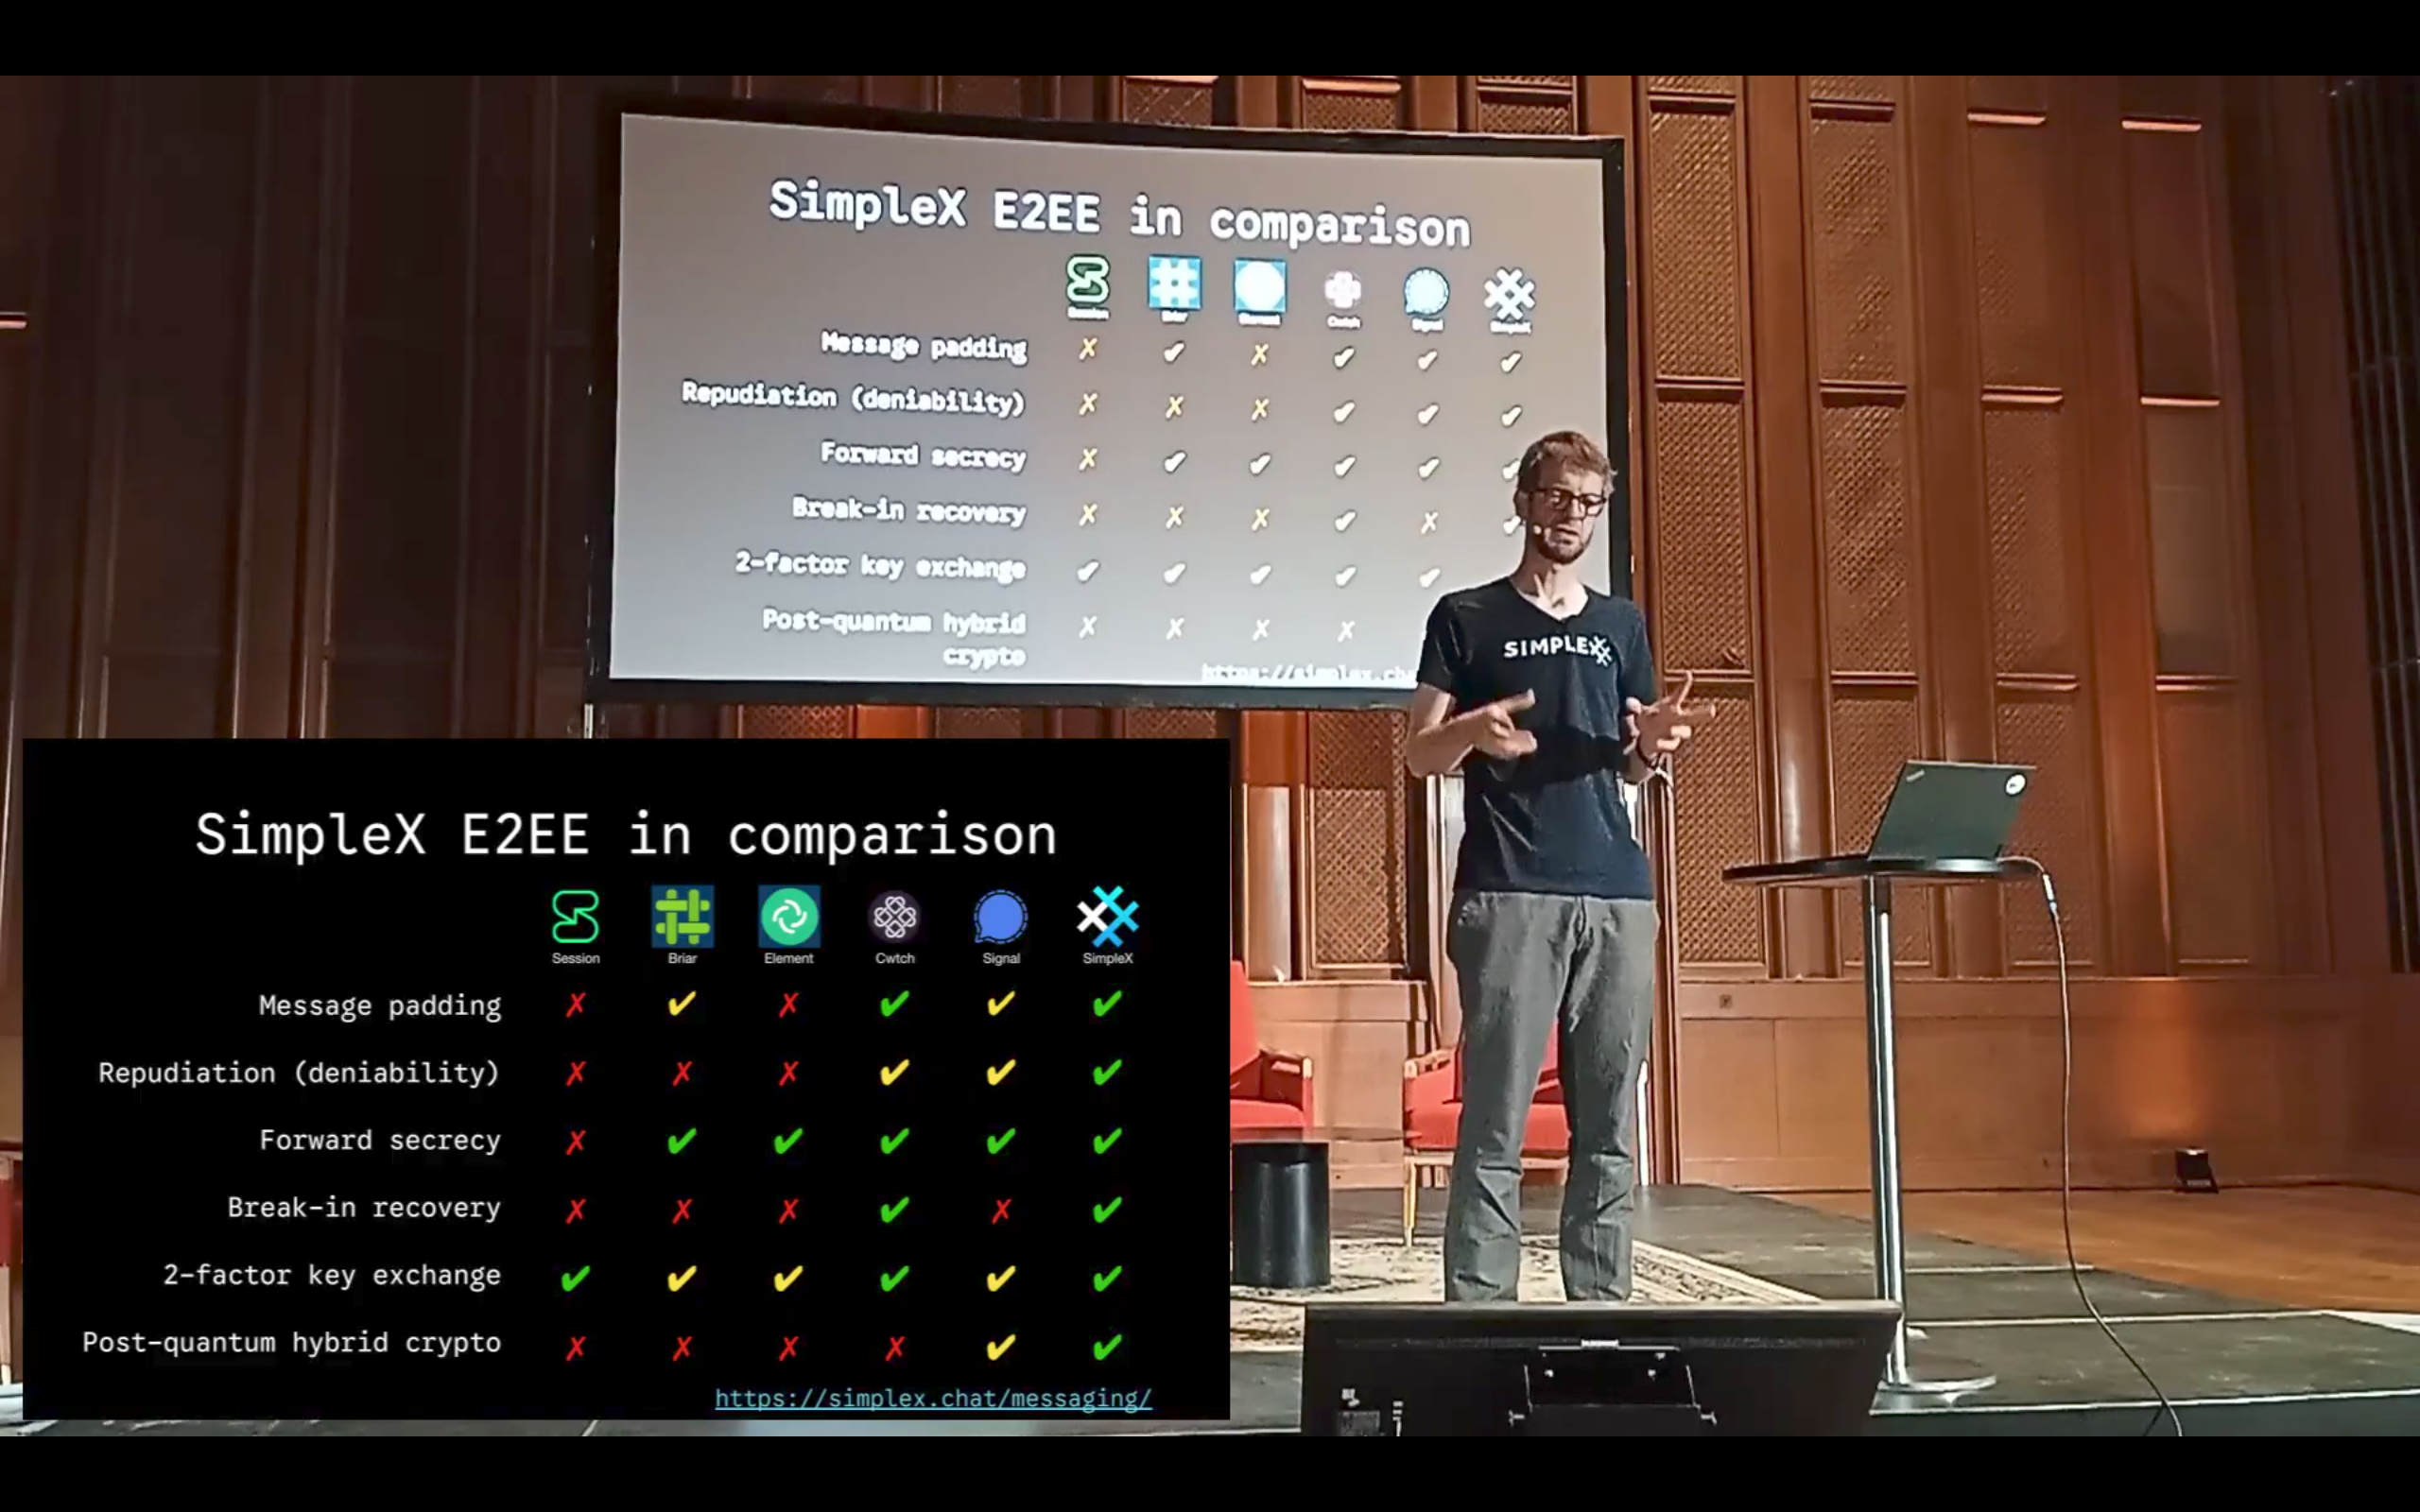
If you're going to bash the competition, at least be honest about it. @simplex
I can't speak to the other points here, but Session does have message padding, though only for attachments up to 10 MB. This is highlighted in section 6.2 of their whitepaper, which is linked on the first page of their website; they also mentioned it in multiple interviews. So they deserve a yellow check mark.
This is achieved by first padding each attachment to fit within a fixed number of constant sizes between 0 and 10 megabytes, then encrypting the attachment with a random symmetric AES key.
It should be a no-brainer to read the whitepaper of the competition before making any claims about them.
I'm happy to be proven wrong.
Whitepaper: https://arxiv.org/pdf/2002.04609
Session website: https://getsession.org/
SimpleX presentation: https://www.youtube.com/watch?v=UhW8AuoRgxg
Also: Checklists Are The Thief Of Joy
#session #sessionmessenger #simplexchat #simplex #dataprotection #privacy #cybersecurity #messenger @session
Alt...
Presentation by a SimpleX employee discussing the differences between SimpleX and Session, Briar, Element, Cwtch, and Signal. The chart lists multiple security factors, and next to them are crosses, yellow check marks, and green check marks.
Quantum hardware: building a quantum computer #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/quantum-hardware-building-a-quantum-computer/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
How to detect the signals of a fraud #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/how-to-detect-the-signals-of-a-fraud/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
"This technical analysis provides the most detailed view yet into the inner workings of the Pegasus spyware system. This includes confirmation of key technical capabilities such as the infection vectors and methodologies used to infect devices, supported by analysis of internal NSO Group documents, that until now had only been identified via forensic investigations. It also presents new material further validating the accuracy and significance of the dataset underpinning the original Pegasus Project investigation. Finally, this research provides an updated analysis, drawing on previously published Pegasus forensic evidence and newly released materials, to validate the technical methodology used to forensically link Pegasus spyware attacks targeting different victims as originating from the same Pegasus customer.
A key aim of this publication is to document and demystify the functionality and operations of technological systems like Pegasus. We hope that it will inform the wider spyware accountability community on how complex surveillance systems such as Pegasus are used by government customers, and also illustrate the key and ongoing role of spyware vendors in keeping such systems operational. We believe this public understanding is of critical value to technologists, researchers, and policy makers and others with an interest in understanding the targeted surveillance ecosystem and threats posed to human rights by surveillance technologies.
The contents of this technical research draw heavily on a large pool of confidential NSO Group training material, presentations and internal technical documentation which were disclosed as part of a long-running civil case taken by WhatsApp and Meta against NSO Group in U.S. court. This new material provides an unprecedented insight into the evolution of NSO Group’s spyware."
#CyberSecurity #Spyware #NSOGroup #Pegasus #Surveillance #Privacy
"Health data is increasingly an important part of law enforcement or government investigations. Wearable data has been critical in a number of cases, where information about heart rate and steps was used to determine the whereabouts of individuals. And the surveillance company Penlink calls fitness trackers and wearables an “overlooked source” for law enforcement since they tend to show movement patterns and changes in heart rates. Law enforcement can try to get access to this data through subpoenas or warrants.
There are many potential privacy issues with these sorts of devices, including whether the companies who make them share or sell information to third-parties. But here we are choosing to focus on two facets we’re concerned with around health data itself: 1) whether the company shares information with law enforcement and governments and 2) if they offer end-to-end encryption, which means the company itself can’t access that health data to begin with."
#SmartObjects #SmartWatches #SmartRings #IoT #Surveillance #Privacy #CyberSecurity #Encryption
Corporate red flags: the invisible risks of partnerships #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/corporate-red-flags-the-invisible-risks-of-partnerships/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
AI and the next wave of conspiracies #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/ai-and-the-next-wave-of-conspiracies/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Ward Christensen and the invention of BBS #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/ward-christensen-and-the-invention-of-bbs/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Post-quantum cryptography: preparing for the unknown #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/post-quantum-cryptography-preparing-for-the-unknown/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
High tech, low life: the cyberpunk world #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/high-tech-low-life-the-cyberpunk-world/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Behind YouTube: Hurley, Chen, and Karim #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/behind-youtube-hurley-chen-and-karim/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
This is a great distillation of some important points about risk, cybersecurity, and the NIST CSF. If your work touches on any of those, this is worth a read.
https://cyberriskbook.com/ai-wont-save-you-from-weak-cybersecurity-fundamentals/

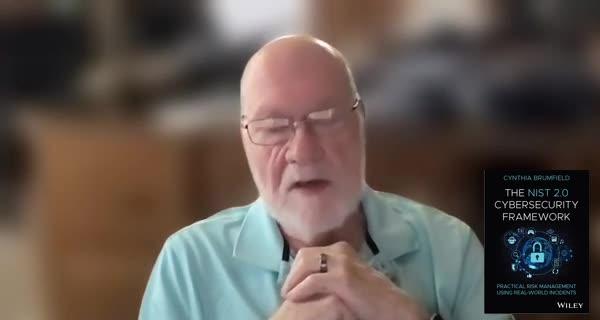
I sat down with cybersecurity pioneer and distinguished professor of computer science at Purdue University, Gene Spafford -- who wrote the foreword to my book on the NIST Cybersecurity Framework -- to discuss why we need stalwart frameworks such as the NIST CSF more than ever in the AI era.
One fascinating point he made: AI isn't uncovering new vulnerabilities; it's exposing old ones, which Gene calls a form of willful tech debt.
Willful debt is the security investment an organization, mostly vendors, chose to skip, the same way you'd choose a new TV over paying the electric bill. AI just makes the consequences show up faster.
Watch his explanation below and read more about our full conversation at https://cyberriskbook.com/ai-wont-save-you-from-weak-cybersecurity-fundamentals/
#CyberSecurity #NIST #NISTCSF #RiskManagement
Alt...
Gene Spafford talking about willful tech debt.
Scam victimology: why did they pick me? #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/scam-victimology-why-did-they-pick-me/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Dave Winer, RSS and the rise of blogging #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/dave-winer-rss-and-the-rise-of-blogging/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Women who shaped vulnerability disclosure #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/women-who-shaped-vulnerability-disclosure/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
The digital mind: how technology shapes mental health #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/the-digital-mind-how-technology-shapes-mental-health/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
 WIRED - The Latest in Technology, Science, Culture and Business [Unofficial] » 🌐
@wired.com@web.brid.gy
A Leak of San Francisco Police Drone Footage Exposes the New Reality of Urban Surveillance
The SFPD’s exposure of hours of videos from drone platform Skydio reveals how broadly it’s watching the city from above—and how the results can spill online.

Alt...
A Leak of San Francisco Police Drone Footage Exposes the New Reality of Urban Surveillance
Organized cybercrime: the rise of cybercrime syndicates #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/organized-cybercrime-the-rise-of-cybercrime-syndicates/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
From concept to reality: what is AI? #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/from-concept-to-reality-what-is-ai/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Fort Firewall gives you detailed control over which Windows apps can access the network with custom rules, blocklists, bandwidth limits, and traffic statistics.
⚠️ Note: On Windows 10+, it currently requires disabling HVCI (Memory Integrity), so check the requirements first.
More details: https://digitalescapetools.com/tools/tool.html?id=fort
#Windows #Privacy #OpenSource #Firewall #SelfHosted #CyberSecurity

Alt...
Screenshot of the Fort Firewall project page showing the app logo, release badges, a description, and the Windows interface with per-application firewall rules for allowing or blocking internet access.
The brains behind the machines: how AI learns #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/the-brains-behind-the-machines-how-ai-learns/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Online dating: the multi-billion dollar swipe #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/online-dating-the-multi-billion-dollar-swipe/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Organized cybercrime: the Crime-as-a-Service model #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/organized-cybercrime-the-crime-as-a-service-model/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Online dating: demographics, bias, and discrimination #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/online-dating-demographics-bias-and-discrimination/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
The forced labour behind fraud operations #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/the-forced-labour-behind-fraud-operations/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
The psychology of cybercrime entrepreneurs #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/the-psychology-of-cybercriminal-entrepreneurs/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Trust without institutions: crypto and blockchain #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/trust-without-institutions-crypto-and-blockchain/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Women in modern offensive security #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/women-in-modern-offensive-security/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog

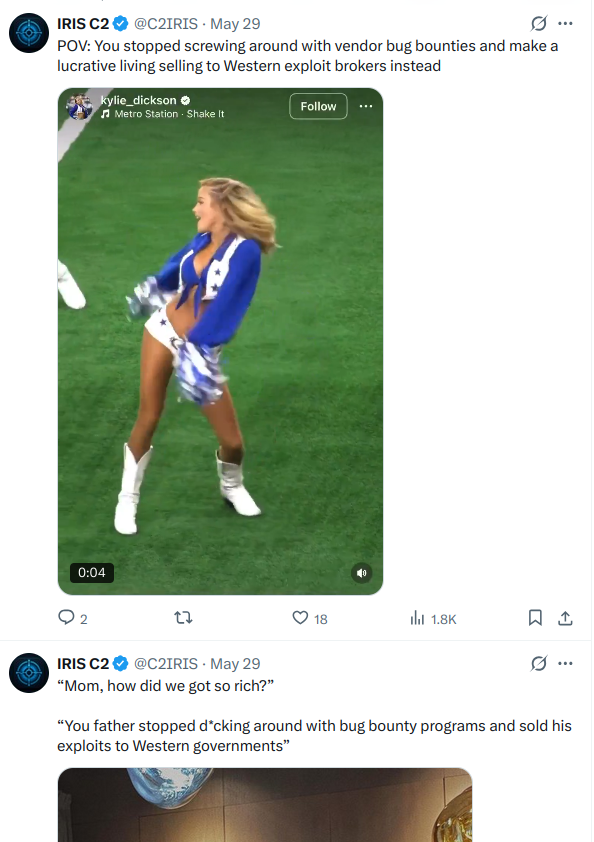
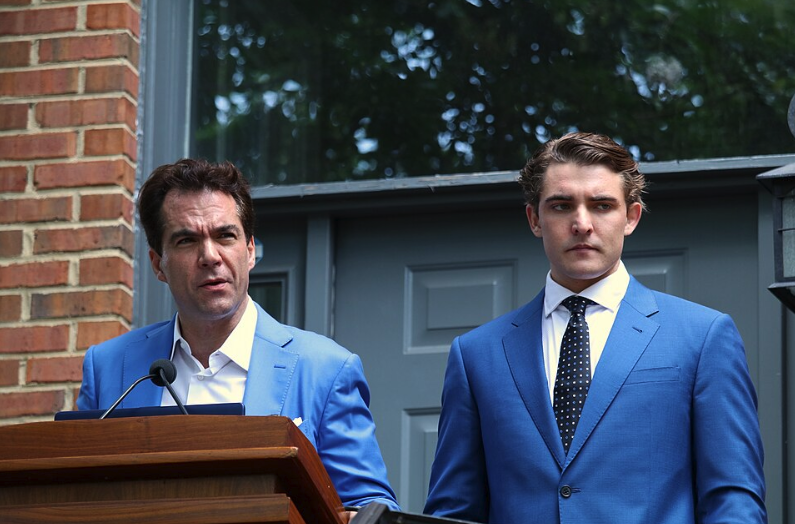
New, by me: Felons, Fraudsters Flog Offensive Cybersecurity Startup
A cybersecurity startup dangling millions of dollars to acquire zero-day security vulnerabilities in popular software is run by a pair of far-right conspiracy theorists and convicted felons whose most recent ventures included fake intelligence companies and a now-defunct AI-based lobbying platform they operated under assumed names.
https://krebsonsecurity.com/2026/07/felons-fraudsters-flog-offensive-cybersecurity-startup/
#c2iris #irisc2 #cybersecurity #maga
Alt...
A screenshot of two Twitter/X posts from the IRIS C2 account. One features a still shot from a video of a Dallas Cowboy cheerleader standing on a green field waving pom-poms and looking to the left. The caption reads: POV: You stopped screwing around with vendor bug bounties and make a lucrative living selling to Western exploit brokers instead. The post below that says, "Mom, how did we get so rich?" The reply: "Your father stopped d*cking around with bug bounty programs and sold his exploits to western governments."
Alt...
A photo of Burkman (left) and Wohl) outside his Arlington, Va. in a 2020 press conference where they made up sexual assault allegations against public figures. Burkman is and standing at a podium in a blue suit. Wohl, also in a blue suit and tie, stands to the right of Burkman, looking down.
Digital addiction: when devices take over #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/digital-addiction-when-devices-take-over/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog
Organized cybercrime: the Ransomware cartels #negativepid #digitalInvestigations #OSINT #cybersecurity #AI #tech #onlineInvestigations #robotics #cyberpsychology #cybercrime https://negativepid.blog/organized-cybercrime-the-ransomware-cartels/?utm_source=mastodon&utm_medium=social&utm_campaign=fedica-Negative-PID-Blog