Search results for tag #infosec


⚠️ PHP CVE-2026-109618 & CVE-2026-109619 leaked before patch Two embargoed PHP vulnerabilities have leaked before fixes shipped (via Kevin Beaumont). No advisory, versions or CVSS yet. A release is expected this week.
https://www.cyberkendra.com/2026/10/php-cve-2026-109618-cve-2026-109619-rce.html
#PHPRCE #security #hack #infosec
The long term impact of this #eMudhra intermediate CA cert private key disclosure: It is now possible to perform TLS MiTM to millions and millions of older #IoT devices (or other devices that won't or can't get updated). The root certificate that has signed the affected intermediate certificate was added to trust stores in about beginning of 2019 (*). It expires only in 18-feb-2043.
This opens the avenue for all kinds of nasty things.
I saw the news about the compromised TLS certificates here on mastodon first.
Then I saw the jokes about "4" here.
But I had to search to find any coverage stating that "4" was literally the private key.
Here you go.
https://www.reddit.com/r/linux/comments/1xau81w/leaked_ssl_intermediate_certificates_https
"Edit: EM OV TLS CA - G3C has 4 as its private key. The number 4. 0x4."
And the detailed coverage that doesn't mention "4"
https://thehackernews.com/2026/10/eight-emudhra-ca-keys-compromised.html
Ugh. Ampath patient records stolen in data breach: https://techcentral.co.za/ampath-breach-no-evidence-test-results-taken/287314/?utm_source=MastodonAfrica
If you've ever had blood work done in South Africa, chances are, Ampath has your details. :/
We don't often think of refrigeration as critical infrastructure, lest of all when we talk of 'cyber attacks' targeting the nuts and bolts of living.
But here we are reminded of this as legacy & unpatched network-enabled refrigeration units in over 300 supermarkets in France had their thermals attacked, raising temperatures internally (to the point of sparking fires in some cases), and spoiling food within them.
Perpetrator & rationale remain unknown.

Can anyone get me a linux-heavy blue team security job in Marquette or Sault Sainte Marie, Michigan?
#GetFediHired #UP #Linux #InfoSec #CyberSecurity #BlueTeam #PurpleTeam #Marquette #Michigan #TheSoo #DaUP #Yooper
New rule!
Whenever anyone suggests using "AI" for anything technical or integrating it with any kind of pipeline, I am going to respond with:
> Okay, what is your plan on dealing with incubated ML exploits? You do know about incubated ML exploits, right?
Seriously, watch this talk:
https://www.youtube.com/watch?v=Z38pTFM0FyU
📢 DEF CON Training is now accepting course submissions for 2027!
Whether you’re an experienced instructor or bringing a new course to the community, we’re looking for high-quality, hands-on training that helps security professionals build real-world skills.
Submit your training material today for the opportunity to teach alongside the DEF CON community in locations around the world including Las Vegas, the Middle East, and Singapore!
For more details, see the application. The deadline to apply is November 13, 2026.
Apply here today 🔗: https://forms.cloud.microsoft/r/z2f4igJPuu
Already submitted your course for Singapore March 2027? As long as you selected your other sessions of interest at the end of the application form, you don’t need to reapply! We have your application on file.
Questions? Email us at training@defcon.org
#DEFCON #DEFCON35 #DEFCONSG #DEFCONME #DEFCONTraining #training #cybersecurity #handsonlearning #infosec #AI #incidentresponse #threathunting #cloud #IoT #hacking

Alt...
Call for trainers

A big batch of updates in our Security Conferences Archives at #InfoCon, everything should be up and seeding + web streaming should be improved. Please enjoy! https://infocon.org
Next up we will update some of the skills and documentaries collections.
#Hacking #InfoSec
@auscert @botconf @brucon @_c0c0n_ @cactuscon @CYBERWARCON @CypherCon @dnsoarc @globsec @hacktivityconf @ietf @layerone @nanog @NorthSec @offensivecon @REverseConf @rsaconference @rvasec @securityfest @steel_con @summercon @iacr_news @WEareTROOPERS @wootsecurity @vehiclesec_conf @x33fcon @zeronights

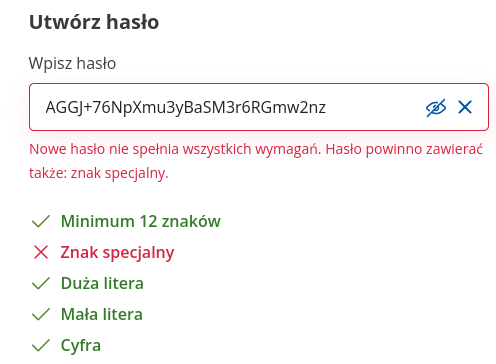
Profil taki Zaufany, profesjonalnie mocno, bardzo bezpieczeństwo, wow uszanowanko.
Alt...
Zrzut ekranu z interfejsu tworzenia hasła dla Profilu Zaufanego.
Hasło zawiera znak "+". Interfejs ostrzega, że:
"Nowe hasło nie spełnia wszystkich wymagań. Hasło powinno zawierać także: znak specjalny."
🚨 Antino backdoor hides its commands in Outlook and OneDrive
Cisco Talos says the Antino Windows backdoor uses Microsoft Graph, Outlook mailboxes, and OneDrive for command-and-control, blending into trusted Microsoft 365 traffic.
The campaign also used a spoofed phishing email that reached its target despite failing DMARC, because the impersonated domain had a p=none policy.
More details: https://digitalescapetools.com/2026/10/antino-backdoor-outlook-onedrive-dmarc-spoofing.html
#CyberSecurity #Malware #Phishing #Microsoft365 #DMARC #Windows #Infosec
#tech #technology #BigTech #data #security #privacy #safety #InfoSec #IT #surveillance #computing #digital #online #internet #web #cloud #meme
Alt...
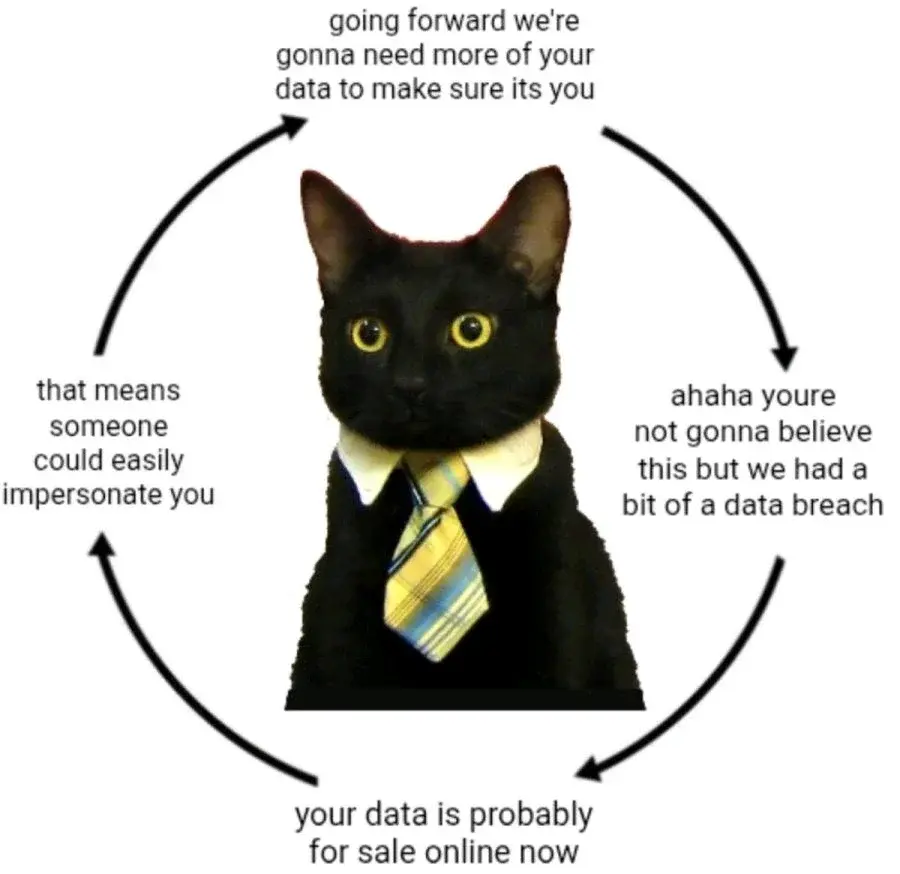
Meme, showing a continuous circle of data breach messages from corporations…
Ahaha you're not gonna believe this but we had a bit of a data breach.
Your data is probably for sale online now.
That means someone could easily impersonate you.
Going forward we're gonna need more of your data to make sure its you.


 Built something I’ve wanted for a while...
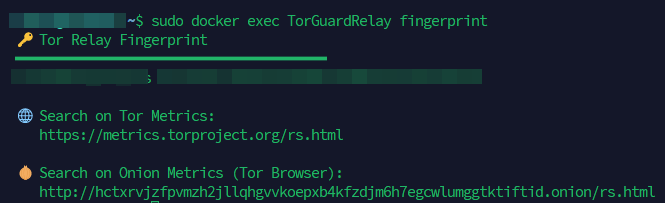
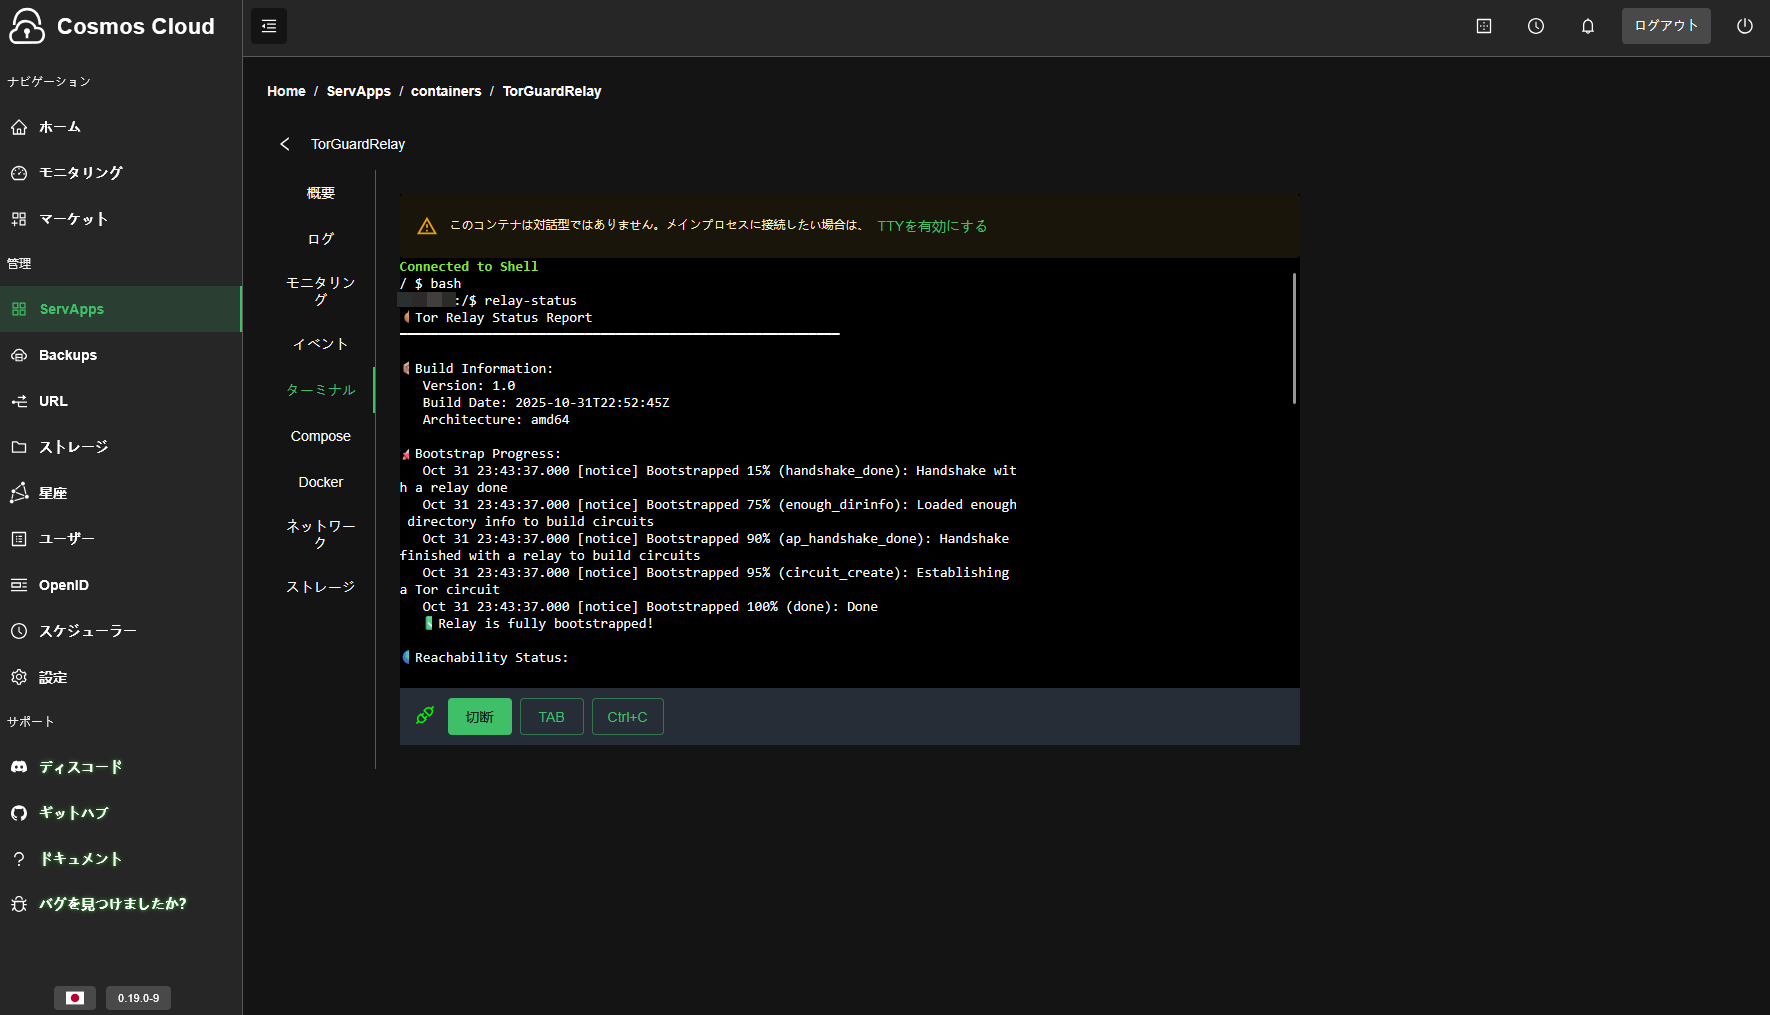
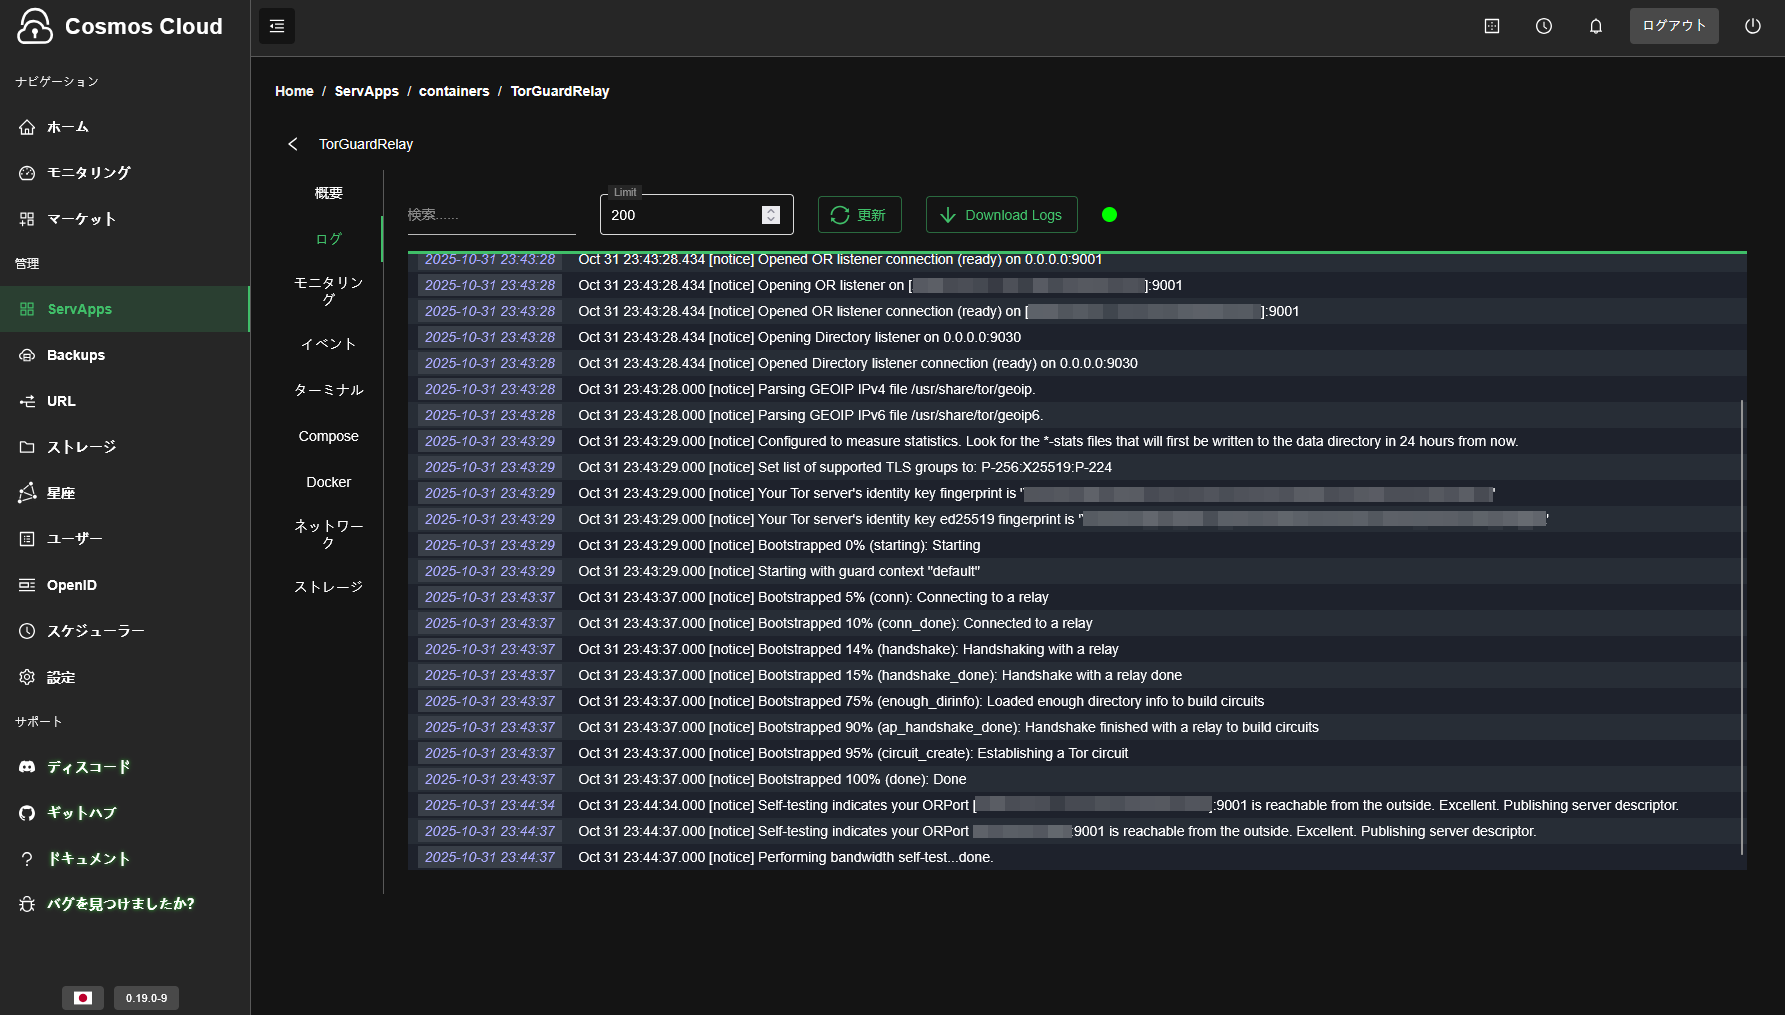
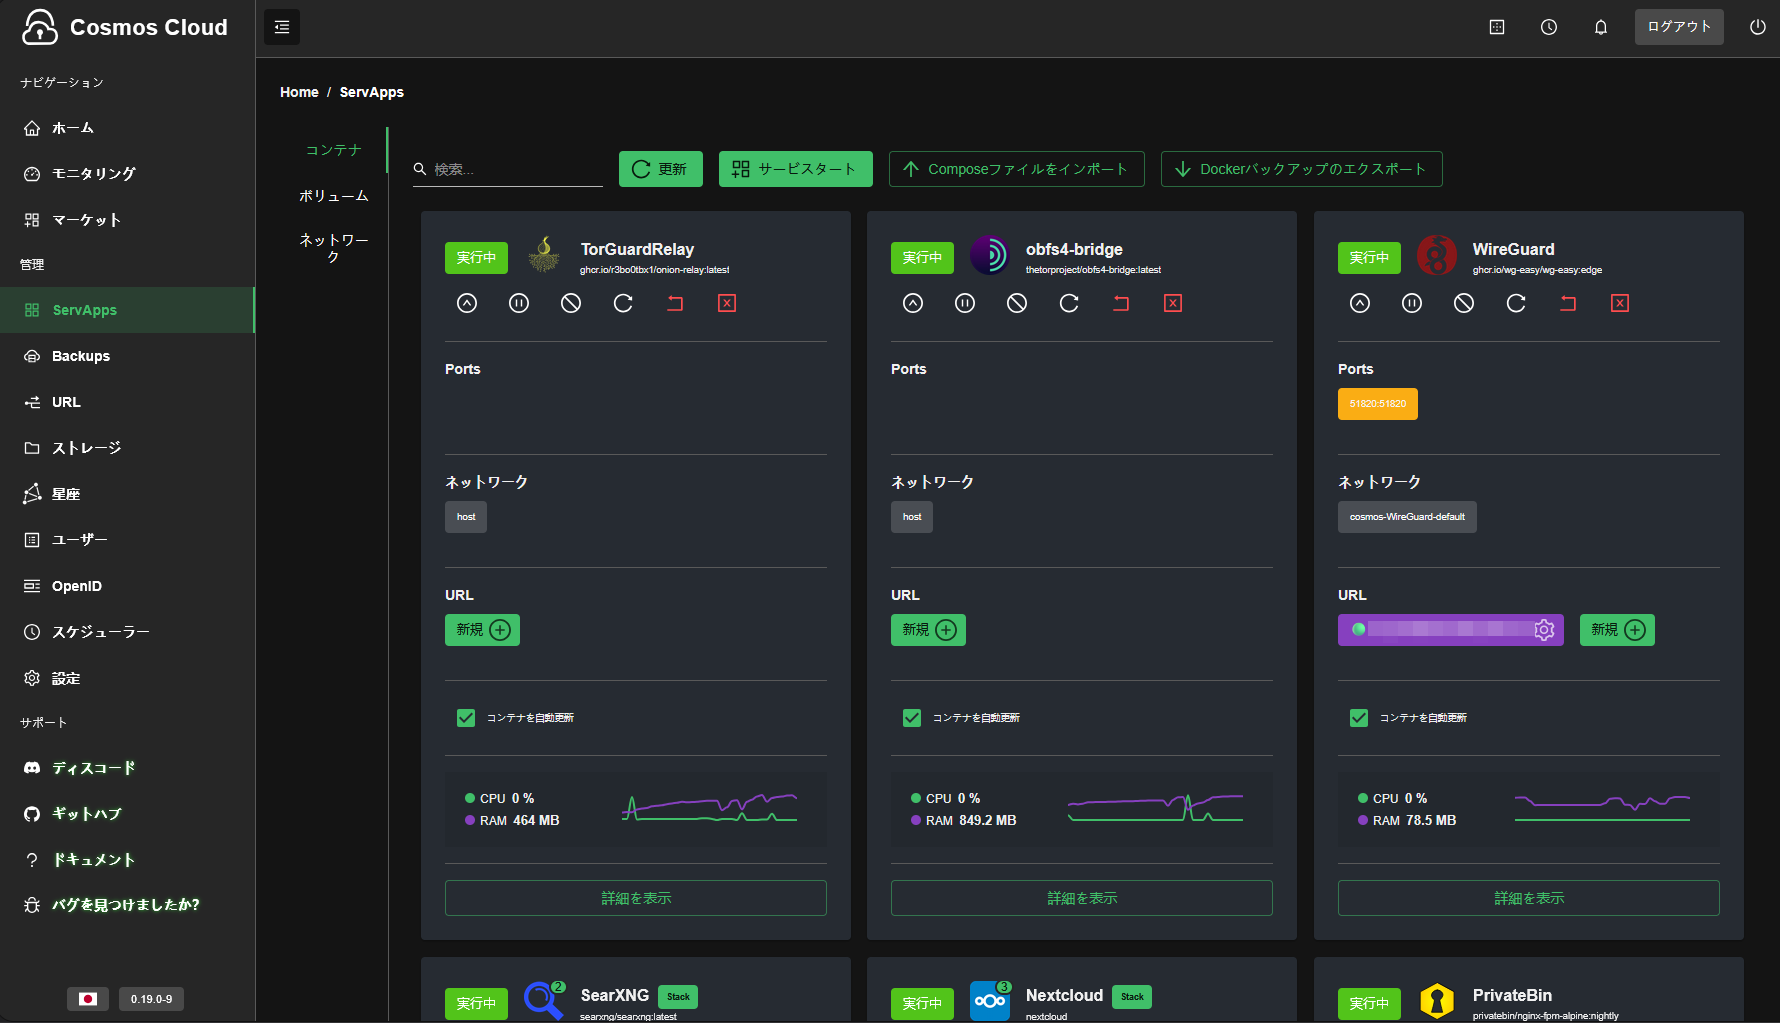
An open-source Docker container that makes running a Tor relay actually simple and reliable.
One command. Self-healing. Multi-arch. Runs everywhere from Raspberry Pi  to VPS

🔗 https://github.com/r3bo0tbx1/tor-guard-relay
If you care about privacy infrastructure:
🧱 Try it out
🐛 Report bugs
💡 Suggest features
⭐ Star it to help others discover it
 Maintaining this in my free time, donation info’s in the README (and please support @torproject, @eff and @privacyguides too).
Protecting privacy, one relay at a time ✨
#Tor #Privacy #OpenSource #Docker #FOSS #SelfHosting #Infosec
📜 Scrolls volume 32 is out! Go check it out for the latest #indieweb, #fediverse and #infosec / #cybersecurity stuff.
https://shellsharks.com/scrolls/scroll/2026-03-06
Have a great weekend!
 [
https://feddit.uk/post/45043385
#signal #moxiemarlinspike #telegram #paveldurov #infosec #encryption
Delta Chat is a messaging platform that works over email.
Setup is similar to a email client.
Messaging is decentralized and interoperable.
Supports end-to-end encryption via PGP.
PGP encryption keys are created automatically.
Default desktop client is based on Electron.
Electron is based on the Google Chromium web browser.
Website: https://delta.chat
Mastodon: @delta
#DeltaChat #Messaging #Privacy #InfoSec #E2EE #OpenPGP #PGP #OpenSource #FOSS #CyberSecurity #Encryption #FreeSoftware
Alt...
Delta Chat logo.
Cryptomator is a client-side encryption tool for cloud storage services.
Data protected via AES-256 encryption.
Individual and business features.
Managed and self-hosted options.
ENCRYPTED
File content.
File/Folder name.
NOT ENCRYPTED
File/Folder access/creation/modification timestamp.
Number of files/folders in a folder/vault.
File size.
Website: https://cryptomator.org
Mastodon: @cryptomator
#Cryptomator #Encryption #InfoSec #Privacy #CyberSecurity #FreeSoftware #FOSS #FLOSS #OpenSource
Alt...
Cryptomator logo.

NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @crypto@a.gup.pe @infosec@a.gup.pe @selfhosting@a.gup.pe

Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.

I wish people would stop giving credit to "prominent cybersecurity/cryptography experts" just because they released some "cypherpunk" book or software of unproven impact 30 years ago and have since then retreated into golden tenure, writing technically empty but catchy preprints with provocative titles. These "Ludd grandpas" (you know at least a couple of names of who I'm referring to) are, unfortunately, still worshipped by a large number of semireligious followers, who contribute to the spread of their moldy ignorance.
Thinking deeper, maybe mine is a typical case of rejection for the image in the mirror: I hope I will never become like that in the future.
The world does not stop at your rants. Keep moving and stay open-minded, or become obsolete.
#cybersecurity #security #infosec #cryptography #crypto #academia #rant #luddism
NEWSCARD Publish and fetch permanent named records via Network News
Newscard creates a decentralized, encrypted, named record paste bin.
[git repo] https://codeberg.org/OCTADE/newscard (use most recent version only)
With a single command, name the card, snarf the file and encrypt it.
With another command, push the encrypted file to the public network.
With another short command, snarf a file from the network.
Only users knowing the name [key] of the record will be able to decrypt it.
If a strong passphrase is used to name the file, it will be very secure.
This is useful for quickly snarfing, encrypting, and publishing a text file:
$~: card enc [passphrase] [file]
$~: card put [passphrase]
It is useful for retrieving a text file with just a key:
$~: card get [passphrase]
$~: card show [passphrase]
If and when you want the general public to access the record just share the keyword.
Newscard uses nine (9) (NINE) layers of encryption with OpenSSL chacha20 cipher.
Newscard generates 9 each of: cipher keys, salts, key iteration parameters.
It would be nice if something like this were added to the ActivityPub protocol, such that keyword[@]host.url would do the same thing. Then secret text records could be stored securely for later retrieval or revelation.
#NewsCard #Pastebin #Usenet #NNTP #NetworkNews #Encryption #Cryptography #Messaging #Anonymity #Protocols #OpenSource #FreeSoftware #BlackHackJack #Censorship #Retro #InfoSec #Ciphers #Codes #FOSS
@infostorm@a.gup.pe @crypto@a.gup.pe @infosec@a.gup.pe

Alt...
Playing card of the Jack of Clubs. The Jack is a moustached man in a black top hat and suit in a oval center cameo. The colors are inverted so that everything on the face is black except the lines which are white, like a charcoal cutout picture., giving it a retro digital appearance mixed with retro handicraft vibes.